Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

tobes

@tobes@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange
0 Followers
0 Following
18 Posts
Joined October 31, 2022
Open post
tobes @tobes@infosec.exchange
· 2w ago
Part seven of my apidays workshop demo series. Two new features shipped correctly and the chat model couldn't reach either of them, because a Model Context Protocol server and a chat route keep two separate tool lists in this codebase - updating one doesn't update the other. Also found: every page's browser tab had read "Create Next App" since the very first commit. https://tobytes.com/a/74 #auth0 #mcp #ai
tobytes.com

The feature was built and the model never heard about it

Two new capabilities shipped in the same session, wired into the backend correctly and invisible to the chat model anyway - because registering a tool and telling the model it exists turned out to be two separate, separately-forgettable steps.

1
0
1
0
Open post
tobes @tobes@infosec.exchange
· 3mo ago
Part three in the delegated access series. The approval flow: FGA resolves the approver, Auth0 CIBA sends a Guardian push, approval creates a delegation. Also: why CIBA consent does not persist across sessions, and why that's fine. https://tobytes.com/articles/delegated-access-approval-auth0-ciba #Auth0 #CIBA #Identity #FGA
tobytes.com

Delegated access part three: approval flows and Auth0 CIBA

The previous post covered how a patient proactively grants a carer access to their record. This post covers the inverse: a user requests access they do not yet have, and the account holder approves it in real time using Auth0's Client-Initiated Backchannel Authentication.

0
0
0
0
Open post
tobes @tobes@infosec.exchange
· 3mo ago
OpenID's Shared Signals Framework and Continuous Access Evaluation Profile went final in August 2025. Auth0 has no native role in either direction of the standard. I built a reference implementation anyway - signed SETs out, verified CAEP signals in, a shared policy enforcement point instead of a heavier authorisation service, and CIBA as the backend-initiated step-up mechanism. https://tobytes.com/articles/continuous-access-evaluation-for-auth0-caep-ssf-demo #auth0 #identity #ciba
tobytes.com

Continuous Access Evaluation for Auth0: Building a CAEP/SSF Reference Demo

OpenID's Shared Signals Framework and Continuous Access Evaluation Profile went final in August 2025, but Auth0 supports neither natively. This post details a from-scratch reference implementation, and what building it revealed about the gap between a finalised spec and the tooling around it.

0
0
0
0
Open post
tobes @tobes@infosec.exchange
· 3mo ago
Built a live Auth0 demo with eight integration patterns side by side. The interesting part: a unified profile page that correlates Traditional, BFF, and SPA sessions via the session_id field on refresh tokens - showing which apps share an Auth0 AS session and which are isolated. Also covers MRRT exchange ledger, Fingerprint ad-blocker bypass, On-Behalf-Of delegation, and Custom Token Exchange. https://tobytes.com/articles/auth0-token-session-demo #Auth0 #OAuth #Identity
Building a Live Auth0 Token and Session Demo
tobytes.com

Building a Live Auth0 Token and Session Demo

Every Auth0 session and token option in one live demo - Traditional Web App, SPA with DPoP, BFF with Multi-Resource Refresh Tokens, SSO isolation, On-Behalf-Of, Custom Token Exchange, and a unified profile view that correlates all of them at the Authorization Server layer.

0
0
0
0
Open post
tobes @tobes@infosec.exchange
· 3mo ago
A reader asked for an RSS feed on this blog. Next.js App Router makes it surprisingly straightforward - a Route Handler for the XML, metadata.alternates for autodiscovery, and zero new dependencies in about fifty lines. https://tobytes.com/articles/adding-rss-to-nextjs-app-router #nextjs #webdev #rss
tobytes.com

Adding an RSS Feed to a Next.js App Router Site

A reader asked me to add an RSS feed to this blog. With Next.js App Router, the whole thing is about fifty lines of code and zero new dependencies - the framework handles more than you might expect.

0
0
0
0
Open post
tobes @tobes@infosec.exchange
· 2mo ago
Tap 'Open in browser' in a mobile app and get asked to log in again - that's two independent OAuth clients with no shared context. Auth0's session_transfer_token fixes it: single-use, 60s, IP-bound. Exchange your refresh token for the STT and pass it to /authorize. Full web session, no re-auth. https://tobytes.com/articles/auth0-native-to-web-sso-session-transfer-token #Auth0 #identity #oauth
Native-to-Web SSO with Auth0: How the Session Transfer Token Works
tobytes.com

Native-to-Web SSO with Auth0: How the Session Transfer Token Works

When a user taps 'Open in browser' inside your mobile app, they get asked to log in again. Auth0's Native-to-Web SSO solves this by exchanging a refresh token for a short-lived session transfer token that the web app can consume without any re-authentication.

0
0
0
0
Open post
tobes @tobes@infosec.exchange
· 2mo ago
Auth0's session_transfer_token generalises from native-to-web handoffs to bridging two different domains on one tenant - but the audience parameter has an undocumented requirement. Name the wrong domain and you get a 200 response that looks like success and isn't. https://tobytes.com/articles/auth0-cross-domain-sso-session-transfer-token-audience-domain #auth0 #identity #oauth
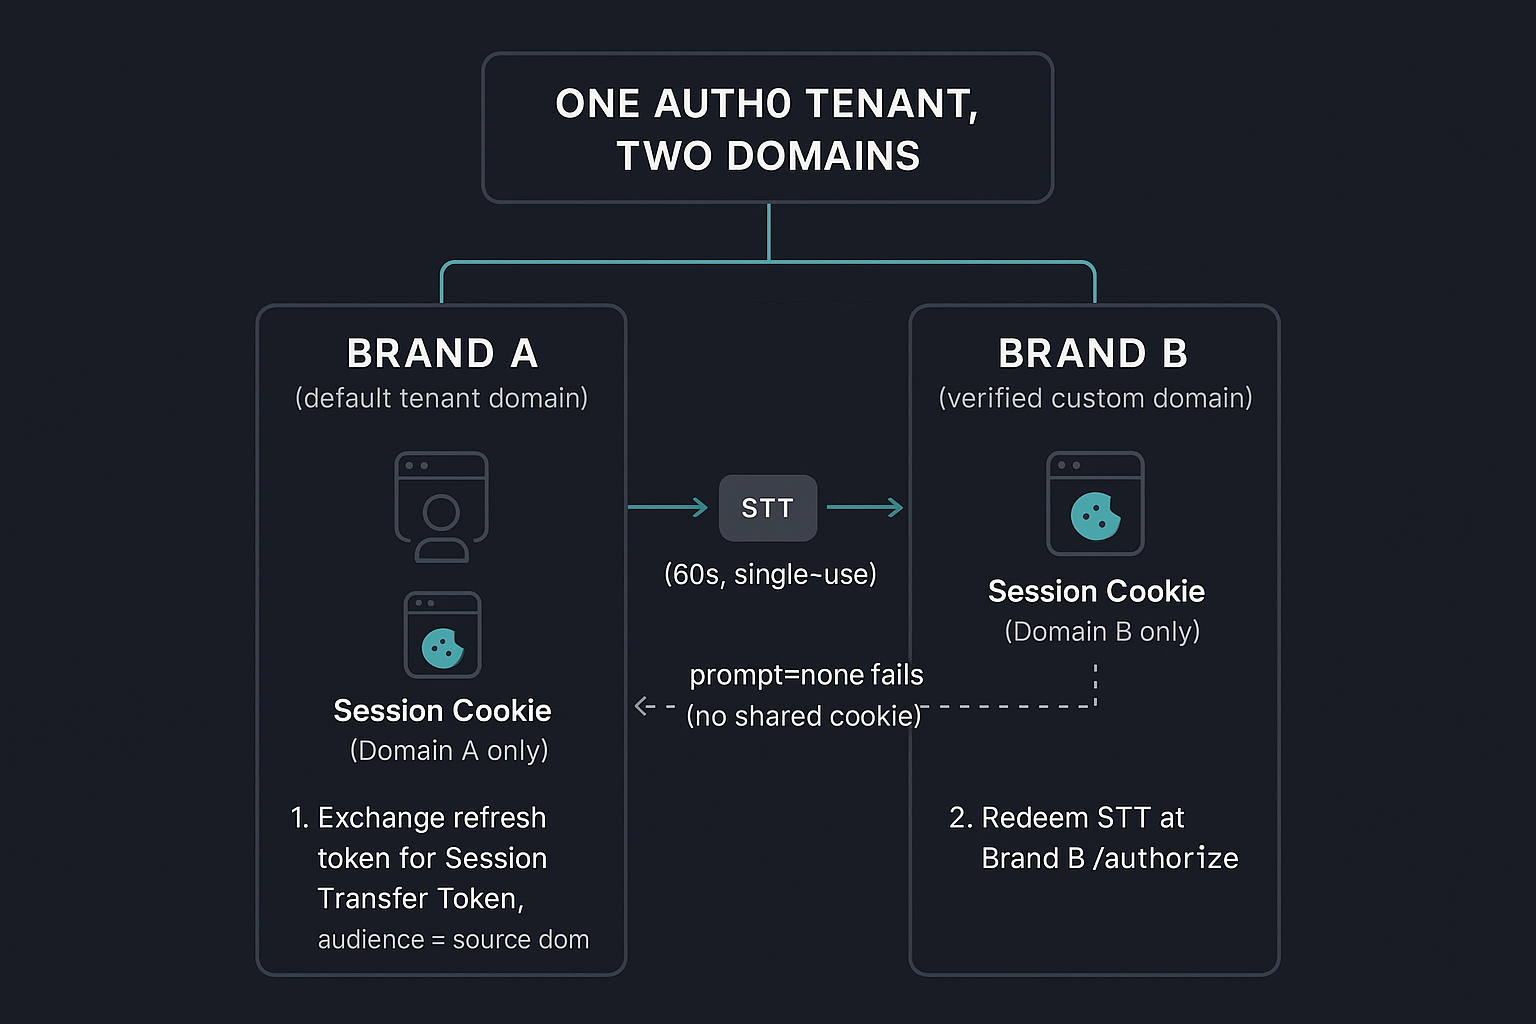
Cross-Domain SSO with Auth0: The Session Transfer Token Audience Gotcha
tobytes.com

Cross-Domain SSO with Auth0: The Session Transfer Token Audience Gotcha

Auth0's session_transfer_token was built for handing a session from a native app to a web app on the same domain. Point it at two genuinely different Auth0 domains in the same tenant and the audience parameter has an undocumented requirement - get it wrong and Auth0 doesn't error, it silently hands you a plain access token instead.

0
0
0
0
Open post
tobes @tobes@infosec.exchange
· 2mo ago
Updated my Auth0 session and token management taxonomy with two grant types I'd left out the first time: CIBA and the Device Authorization Grant. Both are decoupled from the requesting device's own browser but solve different problems. Also added what Rich Authorization Requests (part of Highly Regulated Identity) changes on a CIBA push - structured fields instead of one opaque string. https://tobytes.com/articles/auth0-session-token-management-options-explained #auth0 #oauth #identity
tobytes.com

Auth0 Session and Token Management: Every Option Explained

Auth0 gives you a lot of knobs to turn when it comes to sessions and tokens. This post maps out every option - including RFC 8693 token exchange flows for service delegation, external identity bridging, and customer-support impersonation - and shows how they work together for different application types.

0
0
0
0
Open post
tobes @tobes@infosec.exchange
· 2mo ago
My live Auth0 session and token demo grew three new patterns since I first wrote this up: CIBA against a real Guardian push (now with a Rich Authorization Requests toggle), the Device Authorization Grant, and a comparison against a real Hono app on Cloudflare Workers. The session view also moved out of a single profile page into a sidebar that's visible on every page in the app. https://tobytes.com/articles/auth0-token-session-demo #auth0 #oauth #identity
Building a Live Auth0 Token and Session Demo
tobytes.com

Building a Live Auth0 Token and Session Demo

Every Auth0 session and token option in one live demo - Traditional Web App, SPA with DPoP, BFF with Multi-Resource Refresh Tokens, SSO isolation, On-Behalf-Of, Custom Token Exchange, and a unified profile view that correlates all of them at the Authorization Server layer.

0
0
0
0
Open post
tobes @tobes@infosec.exchange
· 2mo ago
Auth0 published a guide for running @auth0/auth0-hono on Cloudflare Workers. I built the real thing and hit two gotchas the guide skips: authRequired defaults to true and locks every route including the homepage, and the SDK's cookie handler needs the nodejs_compat flag for an undocumented async_hooks dependency. https://tobytes.com/articles/auth0-hono-cloudflare-workers-gotchas #auth0 #cloudflare #oauth
tobytes.com

Deploying @auth0/auth0-hono to Cloudflare Workers: Three Things the Guide Doesn't Mention

Auth0 published a guide for running a confidential client on Cloudflare Workers with @auth0/auth0-hono. I built the guide's example for real and hit three things it doesn't mention — a middleware default that locks down every route, an undocumented Node API dependency, and a session model that changes what revoking a session actually means.

0
0
0
0
Open post
tobes @tobes@infosec.exchange
· 2mo ago
A login and the person behind it aren't the same security principal. Extending the delegated-access model from earlier this year with person/persona/business, and mapping it to real Auth0 sub claims for a personal login versus one federated through a workplace IdP. https://tobytes.com/articles/separating-people-from-accounts-persona-model #auth0 #identity #fga
tobytes.com

Separating people from accounts: why a login isn't a person

The delegated-access series treated the authenticated login as the whole security principal. It isn't quite. The same real person routinely holds more than one login, and an authorisation model that can't tell them apart ends up merging blast radii it shouldn't.

0
0
0
0
Open post
tobes @tobes@infosec.exchange
· 2mo ago
Auth0 Anonymous Sessions sets the auth0_anon cookie only on a genuine create call, never on a renewal - confirmed by testing both explicit session_token and cookie-only renewals. Metadata is fixed at creation too, by design. Same underlying reason for both, and it forces a different pattern for tracking anything (a cart, in my case) across the handoff to login. https://tobytes.com/articles/auth0-anonymous-sessions-fixed-at-creation #auth0 #identity #webdev
tobytes.com

Auth0 Anonymous Sessions: Cookies and Metadata Are Both Fixed at Creation

An anonymous session's cookie and its metadata are both set once, at the moment the session is created, and neither one changes again for the rest of that session's life. That single fact reshapes how you have to track state across the handoff into a known identity.

0
0
0
0
Open post
tobes @tobes@infosec.exchange
· 2mo ago
Running the same OpenFGA model, unchanged, across six industries - and the interesting part isn't that it's reused, it's which primitive gets reused for what. Joint ownership vs a permanent limited role vs an actual delegation, and where flattening them would go wrong. https://tobytes.com/articles/one-fga-model-twelve-industries #auth0 #fga #identity
tobytes.com

One authorisation model, a dozen industries

It's easy to claim an authorisation model is generic. It's more convincing to run the exact same model, unmodified, across media, healthcare, financial services, telco, retail and legal case management, and show the tests passing every time.

0
0
0
0
Open post
tobes @tobes@infosec.exchange
· 2mo ago
Auth0's Passkey APIs let you build passkey sign-in directly into your own UI instead of redirecting to Universal Login. Wrote up how the two fit together, hand-rolled vs pre-built self-service passkey management, and one Allowed Origins (CORS) setting worth checking before you go chasing a WebAuthn bug that isn't there. https://tobytes.com/articles/building-embedded-passkey-login-with-auth0 #auth0 #passkeys #identity
tobytes.com

Building Embedded Passkey Login with Auth0

Auth0's Passkey APIs let you build passkey sign-in directly into your own UI instead of redirecting to Universal Login. Here's how that fits alongside Universal Login, what self-service passkey management looks like hand-rolled versus with Auth0's official pre-built components, and one Allowed Origins (CORS) setting worth checking before you go looking for a WebAuthn bug that isn't there.

0
0
0
0
Open post
tobes @tobes@infosec.exchange
· 2mo ago
Delegation bounded by an amount instead of time: a capped in-game purchase allowance, a category-scoped grocery basket, and why neither is a running total - OpenFGA holds nothing between checks. The same shape turns up again in a minor's graduated account access as they age. https://tobytes.com/articles/delegation-bounded-by-amount-fga #auth0 #fga
tobytes.com

Delegation you can put a number on

Every delegation in this series so far has been bounded by time. This post covers the other kind: bounded by a dollar figure, or a dollar figure and a category together, checked fresh against every attempted spend rather than a stored running total.

0
0
0
0
Open post
tobes @tobes@infosec.exchange
· 1mo ago
Building an apidays workshop demo with Claude Code doing the implementation, I had it run an adversarial review of the build plan before either of us wrote application code. It found a structural flaw in the Auth0 FGA model, not a polish problem - the check was always true, so there was nothing for an AI agent to be denied and nothing to delegate. https://tobytes.com/articles/why-the-apidays-workshop-plan-restarted-from-scratch #auth0 #fga #ai #identity
tobytes.com

Why an apidays workshop proposal had to be replanned from the requirements up

An adversarial review of a conference workshop's build plan found a genuine structural flaw in its Auth0 FGA model, not a polish problem. The check it ran on a citizen's own record was trivially always true, which meant the demo's actual premise - authorising an AI agent acting on someone's behalf - was never being tested at all.

0
1
1
0
Open post
tobes @tobes@infosec.exchange
· 1mo ago
A password login and a passkey login are the same verified persona, holding the same role, with a completely different answer to "how strongly did you just prove that." Modelling session assurance and step-up in OpenFGA as a public wildcard plus a condition that stores nothing on the tuple at all - and why the elevated session behind it has to stay genuinely ephemeral for any of it to be honest. https://tobytes.com/articles/session-assurance-step-up-fga #auth0 #fga #identity
tobytes.com

Session assurance: what a login proves depends on how it happened

Verification level answers who a persona provably is, established once and true forever. Session assurance answers something else entirely - how strongly the current login just proved it - and it has no business being stored as a fact at all.

0
0
0
0
Open post
tobes @tobes@infosec.exchange
· 2w ago
Asked Claude to generate one technical diagram with gpt-image-1. Ten regenerations later: the fix that shipped first got a clean render by quietly dropping the exact claim the diagram existed to show. Caught it after publishing, not before. https://tobytes.com/a/78 #AI #imagegeneration #promptengineering
tobytes.com

Ten attempts, one diagram: what fixing an AI-generated image actually taught me

I asked Claude Code to generate a technical architecture diagram with gpt-image-1 for a blog post. Getting one five-box diagram fully correct took ten regenerations, and the version that shipped first was itself wrong - it got a clean render by quietly dropping the exact claim the whole post was about.

0
0
1
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Pricing
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 21:30:29 UTC