Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

The Threat Codex

@threatcodex@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange

The Threat Codex is a website that tracks news articles on threat actors, malware families, vulnerabilities, and online services.

132 Followers
0 Following
50 Posts
Joined September 28, 2023
Website:
https://threatcodex.com/
Open post
The Threat Codex @threatcodex@infosec.exchange
· 3w ago

Malicious Twitch Browser Extension Exposes 30,000 Users’ OAuth Tokens to Russian Bot Service
#Twitch
https://socket.dev/blog/malicious-twitch-browser-extension

socket.dev
1
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 1mo ago

IDScan confirms breach tied to 153 million stolen driver’s licenses
#IDScan.net
https://www.bleepingcomputer.com/news/security/idscan-confirms-breach-tied-to-153-million-stolen-drivers-licenses/

IDScan confirms breach tied to 153 million stolen driver’s licenses
BleepingComputer

IDScan confirms breach tied to 153 million stolen driver’s licenses

Identity verification company IDScan has confirmed that hackers accessed customer data stored in its cloud platform, days after reports linked the company to a massive database containing more than 153 million driver's license scans.

1
0
2
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 1mo ago

Tracking BigBear 2.0 Evilginx2 Phishing Campaign
#BigBear2.0
https://www.cloudsek.com/blog/tracking-bigbear-2-0-evilginx2-phishing-campaign

Tracking BigBear 2.0 Evilginx2 Phishing Campaign | CloudSEK
cloudsek.com

Tracking BigBear 2.0 Evilginx2 Phishing Campaign | CloudSEK

CloudSEK researchers uncovered BigBear 2.0, a global Microsoft 365 phishing-as-a-service operation targeting hundreds of organizations across 40+ countries. The investigation exposed the attacker’s admin panel, affiliate network, phishing infrastructure, and thousands of stolen credentials and session cookies, revealing how modern AiTM attacks can hijack authenticated sessions even after MFA.

1
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 1mo ago

ShinyHunters claims breach of Florida DMV, threatens data leak
#ShinyHunters
https://cyberinsider.com/shinyhunters-claims-breach-of-florida-dmv-threatens-data-leak/

cyberinsider.com
1
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 2mo ago
CJP protests: India tells GitHub to block Bitchat app, Jack Dorsey leaks notice #Bitchat #GitHubhttps://www.indiatoday.in/technology/news/story/cjp-protests-india-tells-github-to-block-bitchat-app-jack-dorsey-leaks-notice-2955199-2026-07-24
CJP protests: India tells GitHub to block Bitchat app, Jack Dorsey leaks notice
India Today

CJP protests: India tells GitHub to block Bitchat app, Jack Dorsey leaks notice

The Indian government has ordered GitHub to remove all repositories of Jack Dorsey's Bitchat, alleging that the Bluetooth messaging app could be used to bypass internet shutdowns and hinder investigations amid the ongoing CJP protests in Delhi.

2
0
2
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 4w ago

CVE-2026-86218: Active Exploitation of N-able N-central: Critical Pre-Auth Remote Code Execution (RCE) Vulnerability
#N_central #CVE_2026_86218
https://arcticwolf.com/resources/blog/cve-2026-86218/

CVE-2026-86218: Active Exploitation of N-able N-central: Critical Pre-Auth Remote Code Execution (RCE) Vulnerability - Arctic Wolf
Arctic Wolf

CVE-2026-86218: Active Exploitation of N-able N-central: Critical Pre-Auth Remote Code Execution (RCE) Vulnerability - Arctic Wolf

Threat Summary A maximum-severity (CVSS 10.0) vulnerability CVE-2026-86218 has been discovered in N-able N-central prior to build 2026.3.1.14. This flaw allows unauthenticated attackers to execute arbitrary code on the N-central server before authentication enabling remote takeover of the platform. The vulnerability is classified as static code injection (consistent with CWE-96) in a public-facing application endpoint. ... CVE-2026-86218: Active Exploitation of N-able N-central: Critical Pre-Aut

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 2mo ago
Europol-led action against nihilistic violent extremist network "The Com" #TheComhttps://www.europol.europa.eu/media-press/newsroom/news/europol-led-action-against-nihilistic-violent-extremist-network-com
Europol-led action against nihilistic violent extremist network "The Com" – Referral Action Days disrupt online ecosystem and leads to the referral of 4340 URLs referencing disturbing content | Europol
Europol

Europol-led action against nihilistic violent extremist network "The Com" – Referral Action Days disrupt online ecosystem and leads to the referral of 4340 URLs referencing disturbing content | Europol

Over several weeks in June and July 2026, Europol supported an action targeting nihilistic violent extremist content online. Investigators from nine countries participated in these ‘Referral Action Days’, with the common goal to disrupt The Com online ecosystem and limit propaganda dissemination, as well as to find new investigative leads. The action also aimed at enhancing platforms’ response to and awareness of terrorist content online produced and disseminated by The Com groups.

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 2mo ago
CVE-2026-59873: Decompression DoS Via Unlimited Input In node-tar, 90M Weekly Downloads Affected #CVE_2026_59873https://www.ox.security/blog/cve-2026-59873-decompression-dos-via-unlimited-input-in-node-tar-90m-weekly-downloads-affected/
CVE-2026-59873: Decompression DoS Via Unlimited Input In node-tar, 90M Weekly Downloads Affected
OX Security

CVE-2026-59873: Decompression DoS Via Unlimited Input In node-tar, 90M Weekly Downloads Affected

CVE-2026-59873: A high-severity decompression DoS vulnerability in node-tar (<=7.5.18). How it works and how to patch

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 1mo ago

An alignment assessment of recent cybersecurity incidents
#Claude
https://www.anthropic.com/research/alignment-assessment-cybersecurity-incidents

An alignment assessment of recent cybersecurity incidents
anthropic.com

An alignment assessment of recent cybersecurity incidents

We present an alignment assessment of four incidents in which Claude models gained unauthorized access to real third-party systems.

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 3w ago

Active exploitation of Cisco Secure Firewall Management Center vulnerabilities
#CVE_2026_20079 #CVE_2026_20316 #UAT_12197 #UAT_11823 #CyclopsBlink #UAT_11988
https://blog.talosintelligence.com/fmc-ongoing-exploitation/

blog.talosintelligence.com
0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 2mo ago
Hugging Face discloses breach linked to autonomous AI agent #HuggingFacehttps://www.bleepingcomputer.com/news/security/hugging-face-breach-autonomous-ai-agent-system-internal-datasets-credentials/
Hugging Face warns an autonomous AI agent hacked its network
BleepingComputer

Hugging Face warns an autonomous AI agent hacked its network

The Hugging Face artificial intelligence repository disclosed that attackers gained access to internal datasets and credentials after breaching its production infrastructure using an autonomous AI agent system.

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 3w ago

Popular travel app used by 23M lets anyone spy on users, including soldiers
#Polarsteps
https://cybernews.com/security/polarsteps-travel-app-exposes-users-soldiers/

Polarsteps data exposure put travelers’ locations at risk
Cybernews

Polarsteps data exposure put travelers’ locations at risk

230 million photos and videos were accessible in a Polarsteps data exposure, along with GPS points and home addresses. Read what the evidence shows

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 1mo ago

CVE-2026-67276: MikroTik RouterOS SSH Zero-Day Exploited in Router Takeover Attacks
#CVE_2026_67276
https://socprime.com/blog/cve-2026-67276-mikrotik-routeros-ssh-zero-day/

socprime.com
0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 1mo ago

Mind the (Patch) Gap: Multiple Chinese Threat Actors Chain 0-day Exploits in Chrome & Windows
#CVE_2026_85046 #UTA0560 #JungleBamboo #GRIMWEDGELoader #LONGTALE
https://www.volexity.com/blog/2026/09/09/mind-the-patch-gap-multiple-chinese-threat-actors-chain-0-day-exploits-in-chrome-windows/

Mind the (Patch) Gap: Multiple Chinese Threat Actors Chain 0-day Exploits in Chrome & Windows
Volexity

Mind the (Patch) Gap: Multiple Chinese Threat Actors Chain 0-day Exploits in Chrome & Windows

On September 1, 2026, Volexity’s Network Security Monitoring service detected a spear-phishing campaign from a Chinese threat actor it tracks as UTA0560 targeting customers at multiple non-governmental organizations (NGOs). The emails contained a message encouraging the users to a click a link that led to the website of a US-based university. These links abused a reflected cross-site scripting (XSS) vulnerability on the website, redirecting recipients to threat-actor-controlled infrastructure ho

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 2mo ago
A Shell Is Worth a Thousand Images: Bing Images RCEs #CVE_2026_32194 #CVE_2026_32191 #CVE_2026_21536https://xbow.com/blog/bing-images-rce-vulnerabilities
Bing Images RCEs: How XBOW Found Three Critical Flaws | XBOW
XBOW

Bing Images RCEs: How XBOW Found Three Critical Flaws | XBOW

See how XBOW autonomously uncovered three critical Microsoft RCEs by tracing ordinary image-processing and file-upload paths to proven code execution.

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 2mo ago
New 7-Zip Vulnerability Could Let Crafted XZ Archives Run Code During Extraction #7_Zip #CVE_2026_14266https://thehackernews.com/2026/07/new-7-zip-vulnerability-could-let.html
thehackernews.com

New 7-Zip Vulnerability Could Let Crafted XZ Archives Run Code During Extraction

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 2mo ago
Shark vacuum flaw exposes cameras, home maps and Wi-Fi passwords #SharkVacuumCleanershttps://www.malwarebytes.com/blog/news/2026/07/shark-vacuum-flaw-exposes-cameras-home-maps-and-wi-fi-passwords
Shark vacuum flaw exposes cameras, home maps and Wi-Fi passwords
Malwarebytes

Shark vacuum flaw exposes cameras, home maps and Wi-Fi passwords

One compromised Shark robot vacuum could unlock remote access to many others.

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 2mo ago
CVE-2026-42533: Critical NGINX Bug Could Turn HTTP Requests Into Server Takeovers #CVE_2026_42533https://securityaffairs.com/195674/hacking/cve-2026-42533-critical-nginx-bug-could-turn-http-requests-into-server-takeovers.html
CVE-2026-42533: Critical NGINX Bug Could Turn HTTP Requests Into Server Takeovers
Security Affairs

CVE-2026-42533: Critical NGINX Bug Could Turn HTTP Requests Into Server Takeovers

F5 fixes critical nginx flaw CVE-2026-42533 that can crash servers and, in some cases, allow remote code execution through crafted HTTP requests.

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 2mo ago
Large-Scale GitHub Actions Abuse Powers a Distributed cPanel and WHM Exploitation Campaign #Packagist #GitHub #cPanel #CVE_2026_41940https://socket.dev/blog/github-actions-abuse-powers-cpanel-and-whm-exploitation
socket.dev
0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 1mo ago

More than 100,000 fake stores are out to steal your card details
#DoppelCart
https://www.malwarebytes.com/blog/scams/2026/09/more-than-100000-fake-stores-are-out-to-steal-your-card-details

malwarebytes.com
0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 2mo ago
Hackers abuse Notepad++ plugins to stealthily install malware #APT44 #Notepad++ #CVE_2025_56383https://www.bleepingcomputer.com/news/security/hackers-abuse-notepad-plus-plus-plugins-to-stealthily-install-malware/
Hackers abuse Notepad++ plugins to stealthily install malware
BleepingComputer

Hackers abuse Notepad++ plugins to stealthily install malware

Ukraine's CERT has uncovered attacks distributing an archive containing the legitimate Notepad++ application and a malicious utility called LunchPoke disguised as a plugin to establish persistence.

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 2mo ago
Cl0p Exploitation of PTC Windchill & FlexPLM (CVE-2026-12569) #Cl0p #CVE_2026_12569https://ransom-isac.org/blog/clop-windchill-flexplm-exploitation/
Cl0p Exploitation of PTC Windchill & FlexPLM (CVE-2026-12569)
Ransom-ISAC

Cl0p Exploitation of PTC Windchill & FlexPLM (CVE-2026-12569)

A coordinated Unified Threat Advisory covering active Cl0p ransomware affiliate exploitation of internet-exposed PTC Windchill and FlexPLM deployments.

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 2w ago
Contagious Interview Campaign Compromises 30,000 Devices, Steals $10.71M in Crypto #ContagiousInterviewhttps://thehackernews.com/2026/09/contagious-interview-campaign.html
thehackernews.com

Contagious Interview Campaign Compromises 30,000 Devices, Steals $10.71M in Crypto

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 2mo ago
Co-Founder of Controversial Spyware Firm Had Israeli Diplomatic Passport #NSOGroup #Pegasushttps://www.occrp.org/en/project/the-pegasus-project/co-founder-of-controversial-spyware-firm-had-israeli-diplomatic-passport
Co-Founder of Controversial Spyware Firm Had Israeli Diplomatic Passport
OCCRP

Co-Founder of Controversial Spyware Firm Had Israeli Diplomatic Passport

Spyware company NSO Group’s co-founder Shalev Hulio used an Israeli diplomatic passport to enter Panama in 2013, raising questions over the firm’s claims of independence from the Israeli state.

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 2mo ago
Zoom warns of critical account takeover vulnerability #Zoom #CVE_2026_53412https://www.bleepingcomputer.com/news/security/zoom-warns-of-critical-account-takeover-vulnerability/
Zoom warns of critical account takeover vulnerability
BleepingComputer

Zoom warns of critical account takeover vulnerability

Zoom is warning of a critical vulnerability in its desktop client and software development kit for Windows that could be exploited by an unauthenticated party to hijack accounts.

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 2mo ago
FrigidStealer Explained: macOS Infostealer and Gatekeeper Bypass #FrigidStealer #TA2727https://www.picussecurity.com/resource/blog/frigidstealer-explained-macos-infostealer-and-gatekeeper-bypass
FrigidStealer Explained: macOS Infostealer and Gatekeeper Bypass
picussecurity.com

FrigidStealer Explained: macOS Infostealer and Gatekeeper Bypass

Understand how FrigidStealer infects macOS through fake updates and how to validate your defenses against this infostealer with Picus.

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 1mo ago

Adobe Patches Magento Zero-Day Exploited to Deploy Rust Backdoor and PHP Web Shell
#CVE_2026_75650
https://thehackernews.com/2026/09/adobe-patches-magento-zero-day.html

thehackernews.com
0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 2mo ago
TAG-195 Upgrades MaaS Ecosystem with Modular Tools #TAG_195 #TinyEgg #ChonkyChickenhttps://www.recordedfuture.com/research/tag-195-evolves-maas-ecosystem
recordedfuture.com
0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 1mo ago

Gray Rabbits and the Tale of a One-Click Backdoor
#CVE_2026_51990 #UNC3569 #GRAYRABBIT
https://www.gendigital.com/blog/insights/research/one-click-backdoor-sogou

Gray Rabbits and the Tale of a One-Click Backdoor
gendigital.com

Gray Rabbits and the Tale of a One-Click Backdoor

One click. Three critical failures. One backdoor.

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 2mo ago
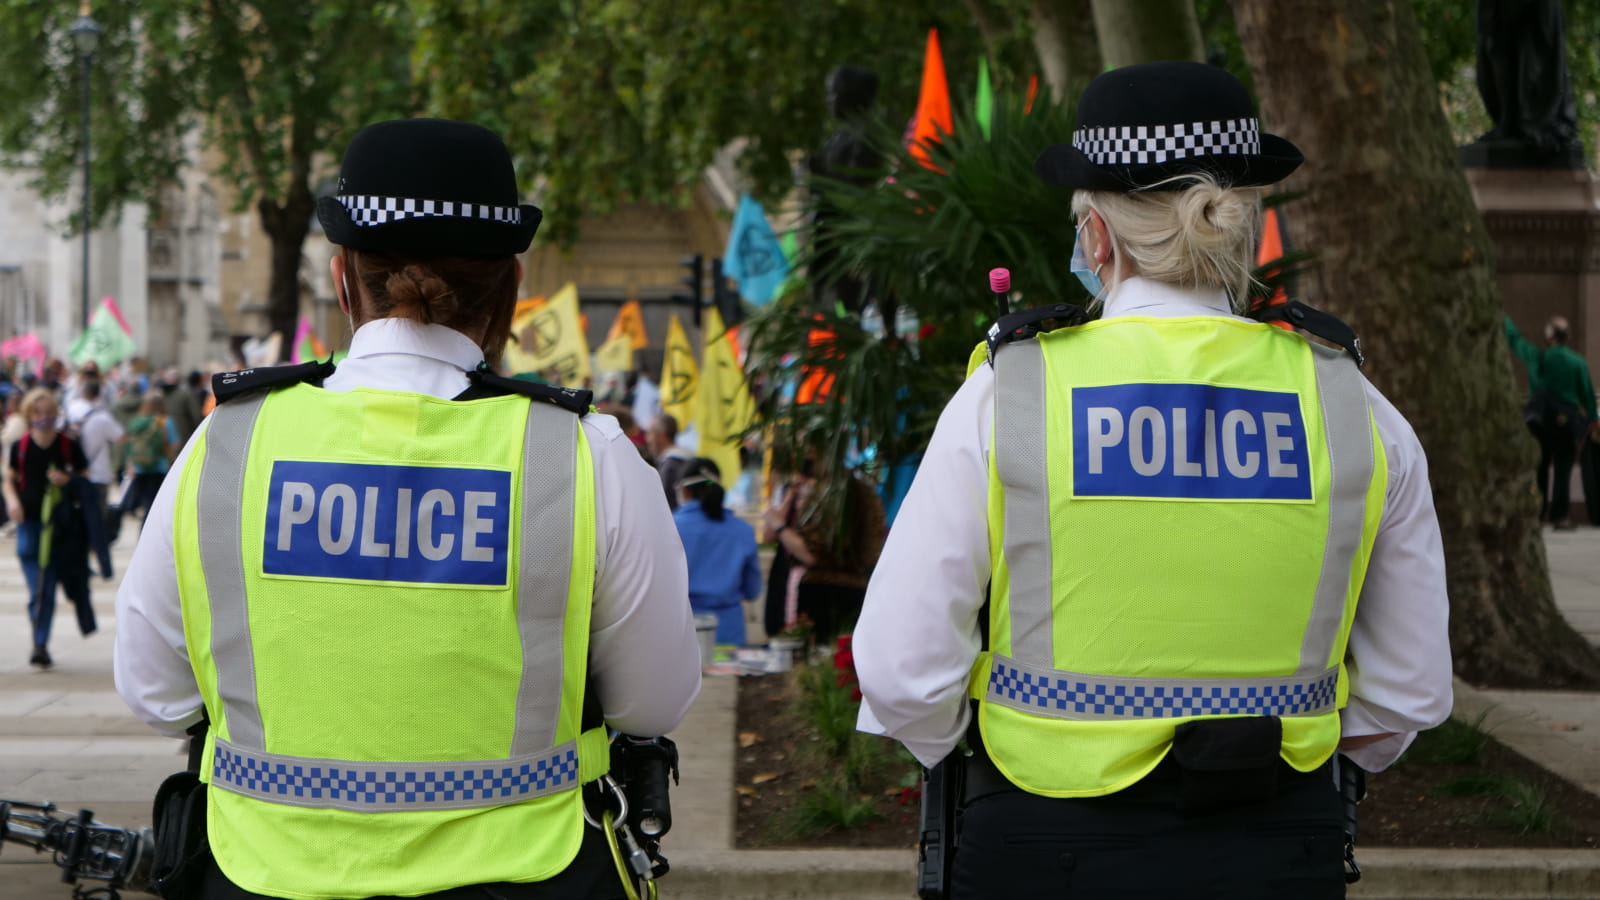
ExfilSquad hackers leak info of over 100,000 UK police officers, staff #ExfilSquadhttps://www.bleepingcomputer.com/news/security/exfilsquad-hackers-leak-info-of-over-100-000-uk-police-officers-staff/
ExfilSquad hackers leak info of over 100,000 UK police officers, staff
BleepingComputer

ExfilSquad hackers leak info of over 100,000 UK police officers, staff

A cyberattack on the U.K.'s Police National Legal Database (PNLD) has compromised contact data of more than 100,000 police officers and other criminal justice professionals.

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 2w ago
ShinyHunters Claims FBI Breach, Says It Stole Data on Agents and Job Applicants #ShinyHuntershttps://thehackernews.com/2026/09/shinyhunters-claims-fbi-breach-says-it.html
thehackernews.com

ShinyHunters Claims FBI Breach, Says It Stole Data on Agents and Job Applicants

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 1mo ago

Once in a BlueMoon: Multiple State-Aligned Threat Actors Rapidly Adopt Novel Exploit Chain Using Chrome and Windows Zero-Days
#BlueMoon #TA412 #CVE_2026_85046 #CVE_2026_85880 #GemStone #UNK_LateNight #UNK_DoubleCheck #UNK_QuietRacket
https://www.proofpoint.com/us/blog/threat-insight/once-bluemoon-multiple-state-aligned-threat-actors-rapidly-adopt-novel-exploit

proofpoint.com
0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 2mo ago
Alleged Russian cyber spy in Boston case previously worked for Kaspersky, source says and documents show #Kaspersky #VoidBlizzardhttps://www.reuters.com/world/alleged-russian-cyber-spy-boston-case-previously-worked-kaspersky-source-says-2026-07-15/
reuters.com
0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 3w ago

CVE-2026-85706: Critical GitLab Path Traversal Exploited in the Wild
#CVE_2026_85706
https://www.rapid7.com/blog/post/etr-cve-2026-85706-critical-gitlab-path-traversal-exploited-in-the-wild/

Rapid7
Rapid7

Rapid7

GitLab has patched CVE-2026-85706, a CVSSv3.1 10.0 path traversal vulnerability in the repository commits API that allows an unauthenticated user to read arbitrary files from GitLab CE and EE servers. CISA added the vulnerability to its Known Exploited Vulnerabilities catalog on September 11, 2026. Self-managed instances should be upgraded to 19.1.8, 19.2.6, or 19.3.2 on an emergency basis.

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 2mo ago
Healthcare giant Abbott probes two cyber incidents amid extortion claims #ShinyHuntershttps://www.malwarebytes.com/blog/data-breaches/2026/07/healthcare-giant-abbott-probes-two-cyber-incidents-amid-extortion-claims
Healthcare giant Abbott probes two cyber incidents amid extortion claims
Malwarebytes

Healthcare giant Abbott probes two cyber incidents amid extortion claims

Extortion groups ShinyHunters and ShadowByt3$ claim they stole vast amounts of patient data. Those allegations have not been verified.

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 1mo ago

CVE-2025-25249 Exploitation Delivers PivotC2, a FortiGate Post-Exploitation RAT
#CVE_2025_25249 #PivotC2
https://socradar.io/blog/cve-2025-25249-pivotc2-fortigate-rat/

socradar.io
0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 2mo ago
Check and Protect: Analysis of Telegram Phishing Operation Targeting Exiled Activist #Telegram #NGOhttps://resident.ngo/lab/writeups/check-and-protect-analysis-of-telegram-phishing-operation-targeting-exiled-activist/
RESIDENT.NGO THREAT LAB

Check and Protect: Analysis of Telegram Phishing Operation Targeting Exiled Activist - RESIDENT.NGO THREAT LAB

In July 2026, RESIDENT.NGO investigated a cloaked phishing operation targeting the Telegram account of an exiled Belarusian activist living in Lithuania. Delivered in a private Telegram Secret Chat as a fake Telegram security alert, the phishing link led to a convincing Telegram-themed page designed to capture one-time login codes in…

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 2mo ago
Russia accuses Telegram founder of aiding terrorism, seeks international arrest #Telegramhttps://therecord.media/russia-telegram-durov-arrest
Russia accuses Telegram founder of aiding terrorism, seeks international arrest
therecord.media

Russia accuses Telegram founder of aiding terrorism, seeks international arrest

Russia is seeking to place Telegram founder Pavel Durov on an international wanted list, alleging that the app has been used by Ukrainian intelligence to organize terrorist attacks and conduct espionage inside Russia.

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 2mo ago
Dolphin X Stealer Targets 300+ Apps and Profiles Users with AI #Kontraktnik #DolphinXStealerhttps://www.varonis.com/blog/dolphin-x-stealer
Dolphin X Stealer Targets 300+ Apps and Profiles Users with AI
varonis.com

Dolphin X Stealer Targets 300+ Apps and Profiles Users with AI

Dolphin X, a new Windows stealer and remote access trojan, targets hundreds of applications from browsers to crypto wallets and includes an AI Profiler that helps attackers zero in on victims.

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 3w ago
Detecting and countering misuse of AI: September 2026 #GTG_20006 #PowerChrome #WUEngine #ShadowC2 #MiniPlasma #GiftDrop #GTG_50014 #GTG_10007 #GTG_50021https://www.anthropic.com/threat-intelligence-report-september-2026
Countering misuse of AI: September 2026 / Anthropic
anthropic.com

Countering misuse of AI: September 2026 / Anthropic

Case studies from threat actors disrupted between December 2025 and August 2026 across seven areas of harm, from cyber operations to biological misuse.

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 2mo ago
Not Every Fox is Silver: Inside an AtlasRAT loader chain #AtlasRAThttps://asec.ahnlab.com/en/94704/
Not Every Fox is Silver: Inside an AtlasRAT loader chain - ASEC
ASEC

Not Every Fox is Silver: Inside an AtlasRAT loader chain - ASEC

Not Every Fox is Silver: Inside an AtlasRAT loader chain ASEC

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 1mo ago

CVE-2026-0310: PAN-OS Buffer Overflow Can Enable Root RCE on PA-Series Firewalls
#CVE_2026_0310
https://socprime.com/blog/cve-2026-0310-analysis/

CVE-2026-0310: Critical PAN-OS Buffer Overflow Flaw
SOC Prime

CVE-2026-0310: Critical PAN-OS Buffer Overflow Flaw

Palo Alto Networks patched CVE-2026-0310, a PAN-OS buffer overflow flaw that can lead to root RCE on PA-Series firewalls

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 3w ago

Inside ‘Project Lily’: The Humans Reading Your ChatGPT Chats
#ChatGPT
https://www.404media.co/inside-project-lily-the-humans-reading-your-chatgpt-chats/

Inside ‘Project Lily’: The Humans Reading Your ChatGPT Chats
404 Media

Inside ‘Project Lily’: The Humans Reading Your ChatGPT Chats

Humans are reading ChatGPT users’ prompts to improve OpenAI’s models, and those chats can include sensitive, personal information, according to leaked internal documents and real prompts seen by 404 Media.

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 1mo ago

Update Chrome now to protect against an actively exploited vulnerability
#CVE_2026_87491
https://www.malwarebytes.com/blog/bugs/2026/09/update-chrome-now-to-protect-against-an-actively-exploited-vulnerability

Update Chrome now to protect against an actively exploited vulnerability
Malwarebytes

Update Chrome now to protect against an actively exploited vulnerability

Chrome issues another monster update, fixing an actively exploited V8 vulnerability and 229 other flaws.

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 2mo ago
Check Point SmartConsole Authentication Bypass Technical Analysis (CVE-2026-16232) #CVE_2026_16232https://www.rapid7.com/blog/post/ra-check-point-smartconsole-authentication-bypass-technical-analysis-cve-2026-16232/
Rapid7
Rapid7

Rapid7

Root cause technical analysis of CVE-2026-16232, an authentication bypass in the SmartConsole login process affecting Check Point Security Management Server and Multi-Domain Security Management Server (MDS).

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 2w ago
Group Policy hijacked: PAYLOAD ransomware weaponizes Active Directory GPO #PAYLOADhttps://securelist.com/tr/payload-ransomware-via-group-policy/121335/
PAYLOAD ransomware attacks through Active Directory GPO
Securelist

PAYLOAD ransomware attacks through Active Directory GPO

Kaspersky GERT experts dive into the technical incident analysis of PAYLOAD ransomware: an encryptionless, binary-less operation that abused Active Directory mechanisms for managing Group Policy Objects.

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 2mo ago
Critical ServiceNow AI Platform Flaw Exploited for Unauthenticated Code Execution #ServiceNow #CVE_2026_6875https://thehackernews.com/2026/07/critical-servicenow-ai-platform-flaw.html
thehackernews.com
0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 2mo ago
Flying Eagle Android RAT: Leaked Source Code, 170 Active Servers, and a New Platform Called Night Dragon #NightDragon #FlyingEagleFrameworkhttps://hunt.io/blog/flying-eagle-android-rat-170-servers-night-dragon
Flying Eagle Android RAT: Leaked Source Code, 170 Active Servers, and a New Platform Called Night Dragon
hunt.io

Flying Eagle Android RAT: Leaked Source Code, 170 Active Servers, and a New Platform Called Night Dragon

Hunt.io and NetAskari trace a leaked Android RAT framework across 170 active servers, analyze the APK builder internals, and document a successor platform called Night Dragon targeting Chinese users.

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 2mo ago
Cleaning Out Inboxes: TA488 Comes for Outlook with Another Half-Click Exploit #TA488 #CVE_2026_42897 #OWAReaperhttps://www.proofpoint.com/us/blog/threat-insight/cleaning-out-inboxes-ta488-comes-outlook-another-half-click-exploit
Cleaning Out Inboxes: TA488 Comes for Outlook with Another Half-Click Exploit | Proofpoint US
Proofpoint

Cleaning Out Inboxes: TA488 Comes for Outlook with Another Half-Click Exploit | Proofpoint US

Threat Research would like to thank the Proofpoint Cloudmark Authority team for their collaboration. Key Findings On 22 July 2026, one day prior to Proofpoint’s recent joint release

0
0
0
0
Open post
The Threat Codex @threatcodex@infosec.exchange
· 3w ago

CVE-2026-75650: StyleSmuggler — Critical RCE in Adobe Commerce and Magento
#CVE_2026_75650 #AdobeCommerce
https://www.akamai.com/blog/security-research/2026/sep/cve-2026-75650-stylesmuggler-adobe-commerce-magento
akamai.com
0
0
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Pricing
  • Contact
  • FAQ
  • Lite (no JS)
Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 22:22:24 UTC