Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

CyberSecureFox :loading:

@cybersecurefox@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange
9 Followers
10 Following
50 Posts
Joined June 07, 2026
Website :loading::
https://cybersecurefox.com/
Discord 👾:
https://discord.gg/wPSdKxABgm
Telegram Channel :verified::
https://t.me/cybersecurefox
Twitter :twitter::
https://twitter.com/cybersecurefox
Alt :mastodon::
https://infosec.exchange/@r3_0x1
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 1w ago
CVE-2026-87902: Critical LFI in WordPress Core 🔗 https://cybersecurefox.com/en/cve-2026-87902-critical-lfi-in-wordpress-core #CVE-2026-87902 #WordPress #vulnerability #LFI #RCE
CVE-2026-87902: Critical LFI In WordPress Core
CyberSecureFox

CVE-2026-87902: Critical LFI In WordPress Core

On September 22, 2026, WordPress released the emergency update 7.1.2, which fixes the critical vulnerability CVE-2026-87902 (CVSS 9.2) in the platform core.

2
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2w ago
CVE-2026-85889: CVSS 10.0 vulnerability in Azure AI Foundry 🔗 https://cybersecurefox.com/en/cve-2026-85889-azure-ai-foundry-cvss-10-privilege-escalation #CVE-2026-85889 #Azure #AI #Foundry #Microsoft #CVSS #10.0 #privilege #escalation
CVE-2026-85889: CVSS 10.0 Vulnerability In Azure AI Foundry
CyberSecureFox

CVE-2026-85889: CVSS 10.0 Vulnerability In Azure AI Foundry

Microsoft has announced that it has fixed six vulnerabilities, including CVE-2026-85889 with a maximum CVSS score of 10.0 in the Azure AI Foundry platform.

3
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2w ago
CVE-2026-93952: CVSS 10.0 vulnerability in Arista VeloCloud Orchestrator 🔗 https://cybersecurefox.com/en/cve-2026-93952-arista-velocloud-orchestrator-cvss-10-active-exploitation #CVE-2026-93952 #VeloCloud #Orchestrator #Arista #CVSS #10.0 #SD-WAN
CVE-2026-93952: CVSS 10.0 Vulnerability In Arista VeloCloud Orchestrator
CyberSecureFox

CVE-2026-93952: CVSS 10.0 Vulnerability In Arista VeloCloud Orchestrator

On 22 September 2026, Arista published Security Advisory 0183 describing the critical vulnerability CVE-2026-93952 in VeloCloud Orchestrator On-Prem — the

2
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2w ago
CVE-2026-76460: Cisco ISE authentication bypass with CVSS 10.0 🔗 https://cybersecurefox.com/en/cve-2026-76460-cisco-ise-authentication-bypass-cvss-10-0 #CVE-2026-76460 #Cisco #ISE #authentication #bypass #CVSS #10.0 #CISA #KEV
CVE-2026-76460: Cisco ISE Authentication Bypass With CVSS 10.0
CyberSecureFox

CVE-2026-76460: Cisco ISE Authentication Bypass With CVSS 10.0

Cisco has published an alert about a critical vulnerability, CVE-2026-76460 (CVSS 10.0), in Identity Services Engine (ISE) and ISE Passive Identity Connector

2
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 3w ago
CVE-2026-58704: Pixel modem vulnerability added to CISA KEV catalog 🔗 https://cybersecurefox.com/en/cve-2026-58704-pixel-modem-privilege-escalation-cisa-kev #CVE-2026-58704 #Google #Pixel #Cellular #Modem #CISA #KEV #privilege #escalation
CVE-2026-58704: Pixel Modem Vulnerability Added To CISA KEV Catalog
CyberSecureFox

CVE-2026-58704: Pixel Modem Vulnerability Added To CISA KEV Catalog

The privilege escalation vulnerability CVE-2026-58704 in the cellular modem of Google Pixel smartphones was added to CISA’s Known Exploited Vulnerabilities

2
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 1mo ago
Marimo CVE-2026-75149: High-Severity MCP Injection Fixed 🔗 https://cybersecurefox.com/en/marimo-cve-2026-75149-mcp-command-injection #Marimo #CVE-2026-75149 #MCP #notebook #vulnerability #code #injection
Marimo CVE-2026-75149: High-Severity MCP Injection Fixed
CyberSecureFox

Marimo CVE-2026-75149: High-Severity MCP Injection Fixed

The interactive notebook Marimo has patched a high-severity vulnerability CVE-2026-75149 that allowed an attacker to inject an arbitrary Model Context

2
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 1mo ago
US Lets Private Cyber Firms Hit Foreign Crime Rings 🔗 https://cybersecurefox.com/en/white-house-private-offensive-cyber-operations #white #house #memo #private #cyber #operations #offensive #cybersecurity #cybercrime #ransomware
US Lets Private Cyber Firms Hit Foreign Crime Rings
CyberSecureFox

US Lets Private Cyber Firms Hit Foreign Crime Rings

The White House published a presidential memorandum that creates a legal framework for engaging private cybersecurity companies to conduct offensive

2
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
Google Blogger Bug Flags Hundreds of Legit Blogs as Malware 🔗 https://cybersecurefox.com/en/google-blogger-false-malware-positives-august-2026 #google #blogger #malware #false #positive #blogger #lockout #automatic #moderation #content #deletion #risk
Google Blogger Bug Flags Hundreds Of Legit Blogs As Malware
CyberSecureFox

Google Blogger Bug Flags Hundreds Of Legit Blogs As Malware

On August 4, 2026, the automatic moderation system of Google Blogger began massively blocking legitimate blogs, mistakenly classifying them as sources of

2
0
4
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
Critical HashiCorp, Veeam, Django fixes in August 2026 🔗 https://cybersecurefox.com/en/hashicorp-veeam-django-august-2026-security-patches #HashiCorp #Veeam #Django #Terraform #MCP #Server #Veeam #VSPC
Critical HashiCorp, Veeam, Django Fixes In August 2026
CyberSecureFox

Critical HashiCorp, Veeam, Django Fixes In August 2026

HashiCorp, Veeam and the Django Software Foundation released fixes in early August 2026 for 11 vulnerabilities, three of which are rated critical. The most

2
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
CVE-2026-18577: N-able N-central Auth Bypass Exploited 🔗 https://cybersecurefox.com/en/cve-2026-18577-n-able-n-central-auth-bypass #CVE-2026-18577 #N-able #N-central #CISA #KEV #authentication #bypass #RMM #security
CVE-2026-18577: N-able N-central Auth Bypass Exploited
CyberSecureFox

CVE-2026-18577: N-able N-central Auth Bypass Exploited

CVE-2026-18577 is an authentication bypass vulnerability in the N-able N-central remote monitoring platform (CVSS 8.2). It was added by CISA to the Known

2
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
CISA Adds Cisco Secure FMC CVE-2026-20316 to KEV 🔗 https://cybersecurefox.com/en/cisco-secure-fmc-cve-2026-20316-kev #cisco #secure #fmc #cve-2026-20316 #cve-2026-20079 #cisa #kev #static #credentials
CISA Adds Cisco Secure FMC CVE-2026-20316 To KEV
CyberSecureFox

CISA Adds Cisco Secure FMC CVE-2026-20316 To KEV

The root cause of CVE-2026-20316 is the presence of hard-coded (static) credentials for a low-privileged account in Cisco Secure FMC software. As Cisco stated

2
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago

SAP July 2026 Patches Fix Three Critical Vulnerabilities

🔗 https://cybersecurefox.com/en/sap-july-2026-security-patches-critical-vulnerabilities

#sap #security #patches #july #2026 #netweaver #abap #sap #approuter #sap #commerce #cloud

cybersecurefox.com
3
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
BlueHammer (CVE-2026-33825): Windows Local Privilege Escalation and MSRC Dispute 🔗 https://cybersecurefox.com/en/cve-2026-33825-bluehammer-windows-privilege-escalation #CVE-2026-33825 #BlueHammer #Windows #local #privilege #escalation #SAM #database #Nightmare #Eclipse
BlueHammer (CVE-2026-33825): Windows Local Privilege Escalation And MSRC Dispute
CyberSecureFox

BlueHammer (CVE-2026-33825): Windows Local Privilege Escalation And MSRC Dispute

The local privilege escalation vulnerability CVE-2026-33825 affecting Microsoft Windows has become the starting point of a public conflict between a security

2
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
OpenWrt 24.10.8 Ships Fix for Critical odhcpd RCE 🔗 https://cybersecurefox.com/en/openwrt-24-10-8-cve-2026-53921-odhcpd-rce #openwrt #24.10.8 #cve-2026-53921 #odhcpd #exploit #dhcpv6 #buffer #overflow #luci #vulnerabilities
OpenWrt 24.10.8 Ships Fix For Critical Odhcpd RCE
CyberSecureFox

OpenWrt 24.10.8 Ships Fix For Critical Odhcpd RCE

The OpenWrt project has released version 24.10.8, which fixes the critical vulnerability CVE-2026-53921 (CVSS 3.1: 9.8) — a stack buffer overflow in the

2
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
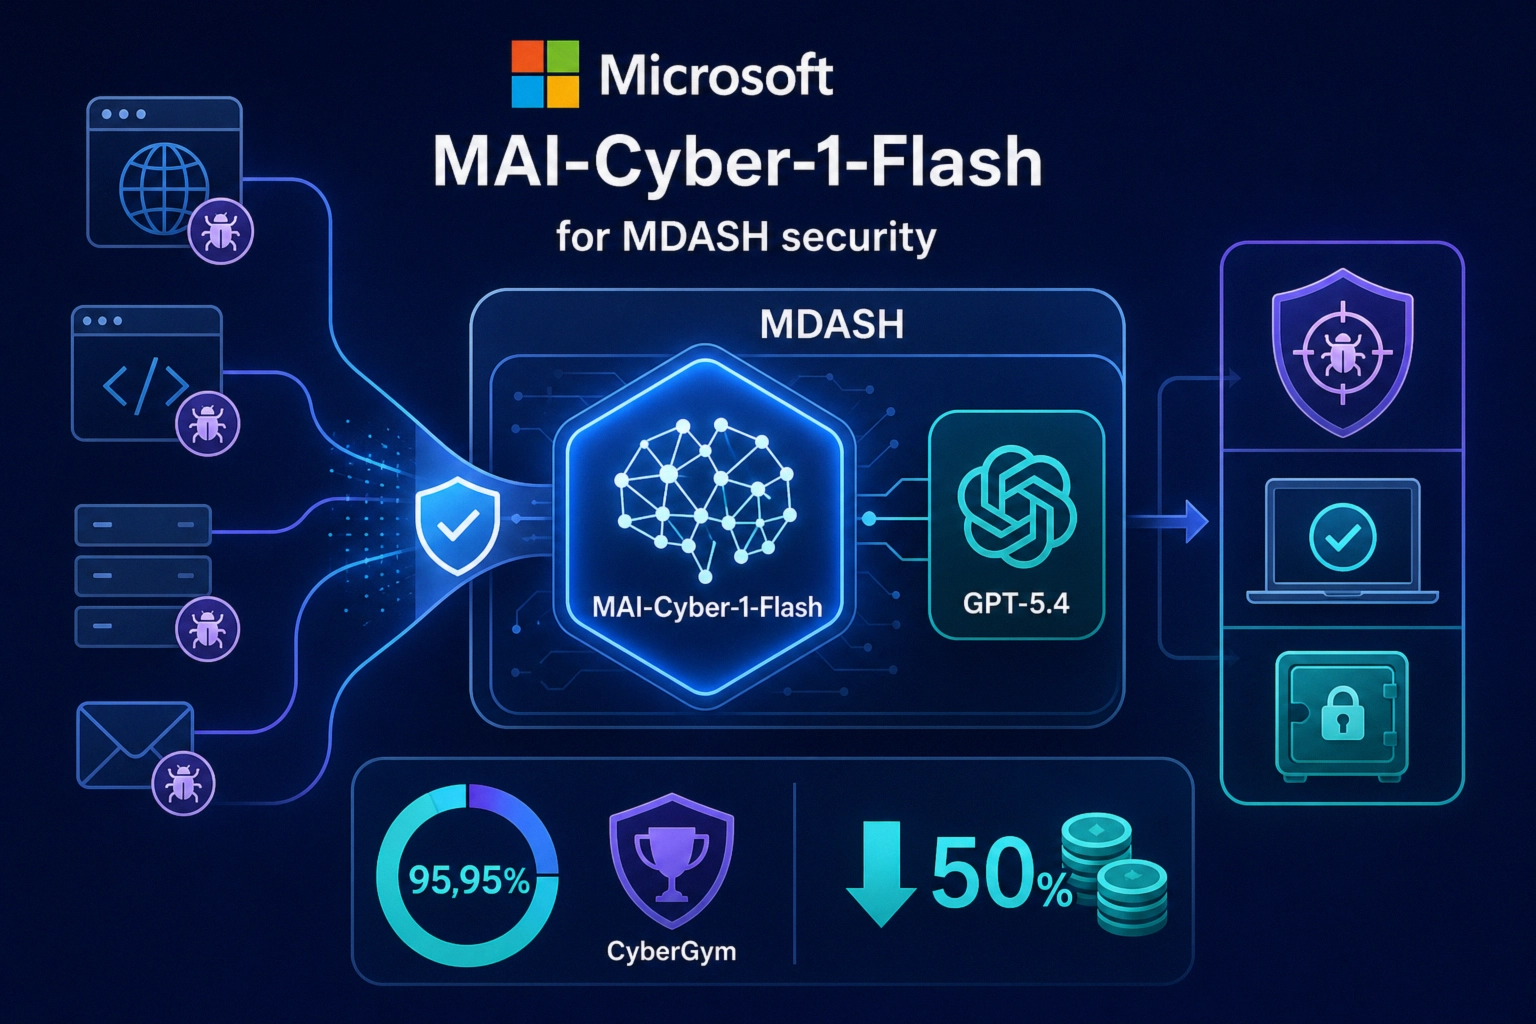
Microsoft unveils MAI-Cyber-1-Flash for MDASH security 🔗 https://cybersecurefox.com/en/microsoft-mai-cyber-1-flash-mdash-security #Microsoft #MAI-Cyber-1-Flash #MDASH #Project #Perception #CyberGym
Microsoft Unveils MAI-Cyber-1-Flash For MDASH Security
CyberSecureFox

Microsoft Unveils MAI-Cyber-1-Flash For MDASH Security

Microsoft has introduced MAI-Cyber-1-Flash, its first artificial intelligence model designed specifically for cybersecurity tasks. The model runs exclusively

2
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
SourTrade: Browser-Assembled Malware Targets Traders 🔗 https://cybersecurefox.com/en/sourtrade-browser-assembled-malware-bun #SourTrade #browser-assembled #malware #Bun #runtime #malvertising #TradingView
SourTrade: Browser-Assembled Malware Targets Traders
CyberSecureFox

SourTrade: Browser-Assembled Malware Targets Traders

Researchers at Confiant have disclosed details of a malvertising campaign called SourTrade, in which the victim’s browser independently assembles the final

2
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
CVE-2026-16723: Critical RCE in Alibaba Fastjson 1.x 🔗 https://cybersecurefox.com/en/cve-2026-16723-fastjson-1x-rce-spring-boot #CVE-2026-16723 #Fastjson #1.x #Alibaba #Fastjson #Spring #Boot #fat-JAR #SafeMode
CVE-2026-16723: Critical RCE In Alibaba Fastjson 1.x
CyberSecureFox

CVE-2026-16723: Critical RCE In Alibaba Fastjson 1.x

The critical remote code execution vulnerability CVE-2026-16723 in the Alibaba Fastjson 1.x library (versions 1.2.68–1.2.83) allows an attacker to execute

2
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
BlueNoroff ClickFix Phishing Targets Crypto via Zoom 🔗 https://cybersecurefox.com/en/bluenoroff-clickfix-zoom-teams-crypto-phishing #BlueNoroff #ClickFix #phishing #Zoom #Microsoft #Teams
BlueNoroff ClickFix Phishing Targets Crypto Via Zoom
CyberSecureFox

BlueNoroff ClickFix Phishing Targets Crypto Via Zoom

Researchers at JUMPSEC have disclosed details of an active phishing platform that, according to their findings, is linked to the North Korean group

2
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
AgentForger: CSRF in OpenAI ChatGPT Agent Builder Exposed 🔗 https://cybersecurefox.com/en/agentforger-chatgpt-agent-builder-csrf #AgentForger #ChatGPT #Agent #Builder #CSRF #OpenAI #Zenity #Labs
AgentForger: CSRF In OpenAI ChatGPT Agent Builder Exposed
CyberSecureFox

AgentForger: CSRF In OpenAI ChatGPT Agent Builder Exposed

Researchers from Zenity Labs disclosed a CSRF-class vulnerability in the OpenAI ChatGPT Agent Builder tool, which received the codename AgentForger. According

2
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
Critical Bing ImageMagick RCE: CVE-2026-32194/32191 🔗 https://cybersecurefox.com/en/bing-imagemagick-rce-cve-2026-32194-32191 #bing #imagemagick #rce #cve-2026-32194 #cve-2026-32191
Critical Bing ImageMagick RCE: CVE-2026-32194/32191
CyberSecureFox

Critical Bing ImageMagick RCE: CVE-2026-32194/32191

Microsoft has assigned two critical CVEs — CVE-2026-32194 and CVE-2026-32191 — to vulnerabilities in Bing’s image-processing infrastructure, each with a CVSS

2
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago

wp2shell: Critical WordPress RCE Chain Under Active Exploit

🔗 https://cybersecurefox.com/en/wp2shell-wordpress-rce-chain-cve-2026-63030-60137

#wp2shell #wordpress #rce #cve-2026-63030 #cve-2026-60137 #sql #injection

cybersecurefox.com
2
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
Critical CVE-2026-6875 in ServiceNow AI Platform (CVSS 9.5) 🔗 https://cybersecurefox.com/en/servicenow-ai-platform-cve-2026-6875-pre-auth-rce #ServiceNow #AI #Platform #CVE-2026-6875 #pre-auth #RCE #sandbox #escape #ServiceNow #vulnerability
Critical CVE-2026-6875 In ServiceNow AI Platform (CVSS 9.5)
CyberSecureFox

Critical CVE-2026-6875 In ServiceNow AI Platform (CVSS 9.5)

A critical vulnerability CVE-2026-6875 with a CVSS 9.5 score has been discovered in the ServiceNow AI Platform, allowing an unauthenticated attacker to

2
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago

FakeGit Campaign Uses AI Agents to Spread SmartLoader Malware

🔗 https://cybersecurefox.com/en/fakegit-agentbaiting-mcp-smartloader-stealc

#FakeGit #AgentBaiting #MCP #servers #SmartLoader #StealC

cybersecurefox.com
2
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
Google's Gemini 3.5 Flash Cyber for Code Security 🔗 https://cybersecurefox.com/en/gemini-3-5-flash-cyber-ai-code-security #gemini #3.5 #flash #cyber #google #deepmind #codemender #ai #code #security #vulnerability #detection
Google's Gemini 3.5 Flash Cyber For Code Security
CyberSecureFox

Google's Gemini 3.5 Flash Cyber For Code Security

Google DeepMind has introduced Gemini 3.5 Flash Cyber — a specialized artificial intelligence model designed to detect, validate, and remediate

2
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
Palo Alto PAN-OS CVE-2026-0257 Used for Qilin Ransomware 🔗 https://cybersecurefox.com/en/palo-alto-pan-os-cve-2026-0257-qilin-ransomware #Palo #Alto #Networks #PAN-OS #CVE-2026-0257 #Qilin #ransomware #Agenda #ransomware
Palo Alto PAN-OS CVE-2026-0257 Used For Qilin Ransomware
CyberSecureFox

Palo Alto PAN-OS CVE-2026-0257 Used For Qilin Ransomware

The authentication bypass vulnerability CVE-2026-0257 (CVSS 7.8) in the portal and gateway components of Palo Alto Networks PAN-OS is, according to Arctic

2
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
Invisible Prompts: RCE Attacks on Mobile AI Agents 🔗 https://cybersecurefox.com/en/invisible-prompts-rce-mobile-ai-agents #mobile #ai #agents #rce #invisible #prompts #android #debugging #appagent
Invisible Prompts: RCE Attacks On Mobile AI Agents
CyberSecureFox

Invisible Prompts: RCE Attacks On Mobile AI Agents

A team of researchers from Simon Fraser University, the Chinese University of Hong Kong, Shandong University and the Xingtu (QAX) lab has published a paper on

2
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
AWS Kiro IDE RCE via MCP Config and Hidden Text 🔗 https://cybersecurefox.com/en/aws-kiro-ide-remote-code-execution-mcp #aws #kiro #kiro #ide #remote #code #execution #rce #mcp.json
AWS Kiro IDE RCE Via MCP Config And Hidden Text
CyberSecureFox

AWS Kiro IDE RCE Via MCP Config And Hidden Text

Researchers from Intezer together with Kodem Security discovered in the agentic IDE AWS Kiro an attack chain that allowed an attacker, via hidden text on an

2
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
Rapid7 Exposes WebDAV Malware Lab Testing CVE-2025-33053 🔗 https://cybersecurefox.com/en/rapid7-webdav-malware-lab-cve-2025-33053 #Rapid7 #WebDAV #malware #CVE-2025-33053 #CURP #phishing #Mexico
Rapid7 Exposes WebDAV Malware Lab Testing CVE-2025-33053
CyberSecureFox

Rapid7 Exposes WebDAV Malware Lab Testing CVE-2025-33053

Researchers at Rapid7 discovered an unsecured malware delivery server containing 1,048 files — ranging from phishing lure templates and filename spoofing

2
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago

HollowGraph: Stealthy Microsoft 365 Calendar Backdoor

🔗 https://cybersecurefox.com/en/hollowgraph-microsoft-365-calendar-c2

#hollowgraph #microsoft #365 #microsoft #graph #api #oauth #apps #iran #apt
cybersecurefox.com
2
0
3
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
Daxin Rootkit and Stupig Backdoor Discovered in Taiwan 🔗 https://cybersecurefox.com/en/daxin-rootkit-stupig-backdoor-taiwan-incident #daxin #rootkit #stupig #backdoor #windows #keyboard #layout #winlogon.exe #taiwan #cyber #espionage
Daxin Rootkit And Stupig Backdoor Discovered In Taiwan
CyberSecureFox

Daxin Rootkit And Stupig Backdoor Discovered In Taiwan

Teams from Symantec and the Carbon Black Threat Hunter Team have discovered an active instance of the Daxin rootkit on a compromised host belonging to the

2
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
xAI Grok Build Uploaded Entire Git Repos to Cloud Storage 🔗 https://cybersecurefox.com/en/xai-grok-build-git-repository-upload-incident #xai #grok #build #git #repository #upload #source #code #privacy #secrets #exposure #google #cloud #storage
XAI Grok Build Uploaded Entire Git Repos To Cloud Storage
CyberSecureFox

XAI Grok Build Uploaded Entire Git Repos To Cloud Storage

The Grok Build CLI tool from xAI, designed to help with writing code, was, according to a researcher, uploading to xAI’s cloud storage not only the files

2
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
Legacy UEFI Shims Signed by Microsoft Bypass Secure Boot 🔗 https://cybersecurefox.com/en/legacy-microsoft-uefi-shims-secure-boot-bypass #secure #boot #uefi #shim #legacy #bootloaders #eset #research #cve-2026-8863
Legacy UEFI Shims Signed By Microsoft Bypass Secure Boot
CyberSecureFox

Legacy UEFI Shims Signed By Microsoft Bypass Secure Boot

Researchers at ESET identified 11 legacy UEFI bootloaders (so-called shims) signed by Microsoft that are still considered trusted on most UEFI systems and can

2
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
CISA Flags CVE-2026-58644 SharePoint RCE in KEV Catalog 🔗 https://cybersecurefox.com/en/cisa-adds-cve-2026-58644-sharepoint-kev #CISA #CVE-2026-58644 #SharePoint #Server #vulnerability #KEV #catalog #IIS #machine #keys
CISA Flags CVE-2026-58644 SharePoint RCE In KEV Catalog
CyberSecureFox

CISA Flags CVE-2026-58644 SharePoint RCE In KEV Catalog

On July 16, 2026, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the CVE-2026-58644 vulnerability in Microsoft SharePoint Server to

2
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
ClickLock Stealer: New macOS Malware Hijacks Desktop 🔗 https://cybersecurefox.com/en/clicklock-stealer-macos-infostealer #clicklock #stealer #macos #malware #macos #infostealer #group-ib #clickfix
ClickLock Stealer: New MacOS Malware Hijacks Desktop
CyberSecureFox

ClickLock Stealer: New MacOS Malware Hijacks Desktop

Researchers at Group-IB have discovered a new macOS infostealer, ClickLock Stealer, which uses a fundamentally different approach to obtaining the system

2
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
n8n Enterprise token exchange flaw CVE-2026-59208 🔗 https://cybersecurefox.com/en/n8n-enterprise-cve-2026-59208-token-exchange-auth-bypass #n8n #enterprise #cve-2026-59208 #token #exchange #jwt #sub #iss #authentication #bypass
N8n Enterprise Token Exchange Flaw CVE-2026-59208
CyberSecureFox

N8n Enterprise Token Exchange Flaw CVE-2026-59208

Administrators of n8n Enterprise with token exchange enabled and multiple trusted issuers should treat updating as urgent. Even with the vulnerability’s

2
0
2
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 1mo ago
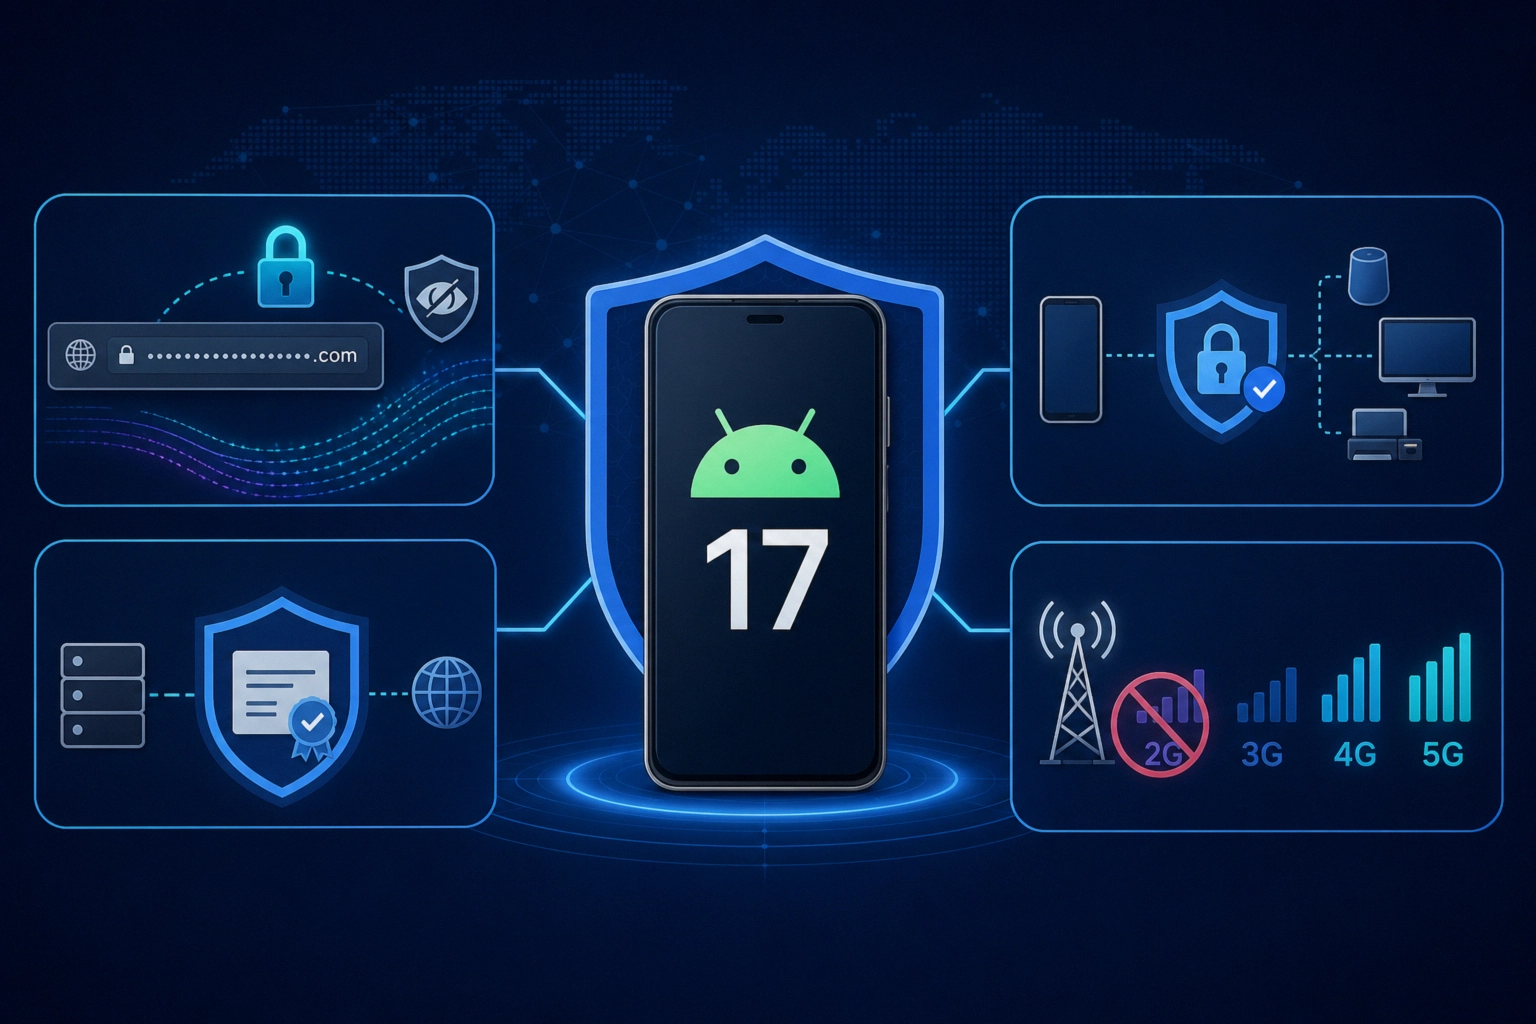
Android 17: New Network Security Protections Explained 🔗 https://cybersecurefox.com/en/android-17-network-security-ech-local-network-ct-2g #android #17 #encrypted #client #hello #ech #local #network #protection #certificate #transparency
Android 17: New Network Security Protections Explained
CyberSecureFox

Android 17: New Network Security Protections Explained

Android 17 (API level 37) introduces four major network security improvements: platform support for Encrypted Client Hello (ECH) to hide the names of visited

0
0
0
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
Iranian APT Nimbus Manticore Deploys NightLedger Backdoor 🔗 https://cybersecurefox.com/en/nimbus-manticore-nightledger-bridgehead-arcbridge #Nimbus #Manticore #NightLedger #BridgeHead #ArcBridge #Iranian #APT
Iranian APT Nimbus Manticore Deploys NightLedger Backdoor
CyberSecureFox

Iranian APT Nimbus Manticore Deploys NightLedger Backdoor

According researchers, the Iranian group Nimbus Manticore (also known as Mirage Kitten, Smoke Sandstorm, UNC1549) is carrying out a series of cyberattacks

0
0
0
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
CISA Adds Three Actively Exploited Flaws to KEV Catalog 🔗 https://cybersecurefox.com/en/cisa-adds-langflow-tomcat-n-central-kev #cisa #kev #catalog #langflow #rce #apache #tomcat #encryption #bypass #n-able #n-central #authentication #bypass
CISA Adds Three Actively Exploited Flaws To KEV Catalog
CyberSecureFox

CISA Adds Three Actively Exploited Flaws To KEV Catalog

CISA has added three vulnerabilities with confirmed active exploitation to the Known Exploited Vulnerabilities (KEV) catalog: a critical RCE in Langflow

0
0
0
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
SMOKE#SCREEN: ScreenConnect Abuse and Powercat Stealer 🔗 https://cybersecurefox.com/en/smoke-screen-screenconnect-abuse-powercat-roblox-cheats #ScreenConnect #abuse #SMOKE#SCREEN #Powercat #stealer #fake #Roblox #cheats #ConnectWise #ScreenConnect
SMOKE#SCREEN: ScreenConnect Abuse And Powercat Stealer
CyberSecureFox

SMOKE#SCREEN: ScreenConnect Abuse And Powercat Stealer

Researchers at Securonix have uncovered an active multi-wave campaign dubbed SMOKE#SCREEN, in which attackers use phishing lures — fake Adobe and Zoom

0
0
0
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
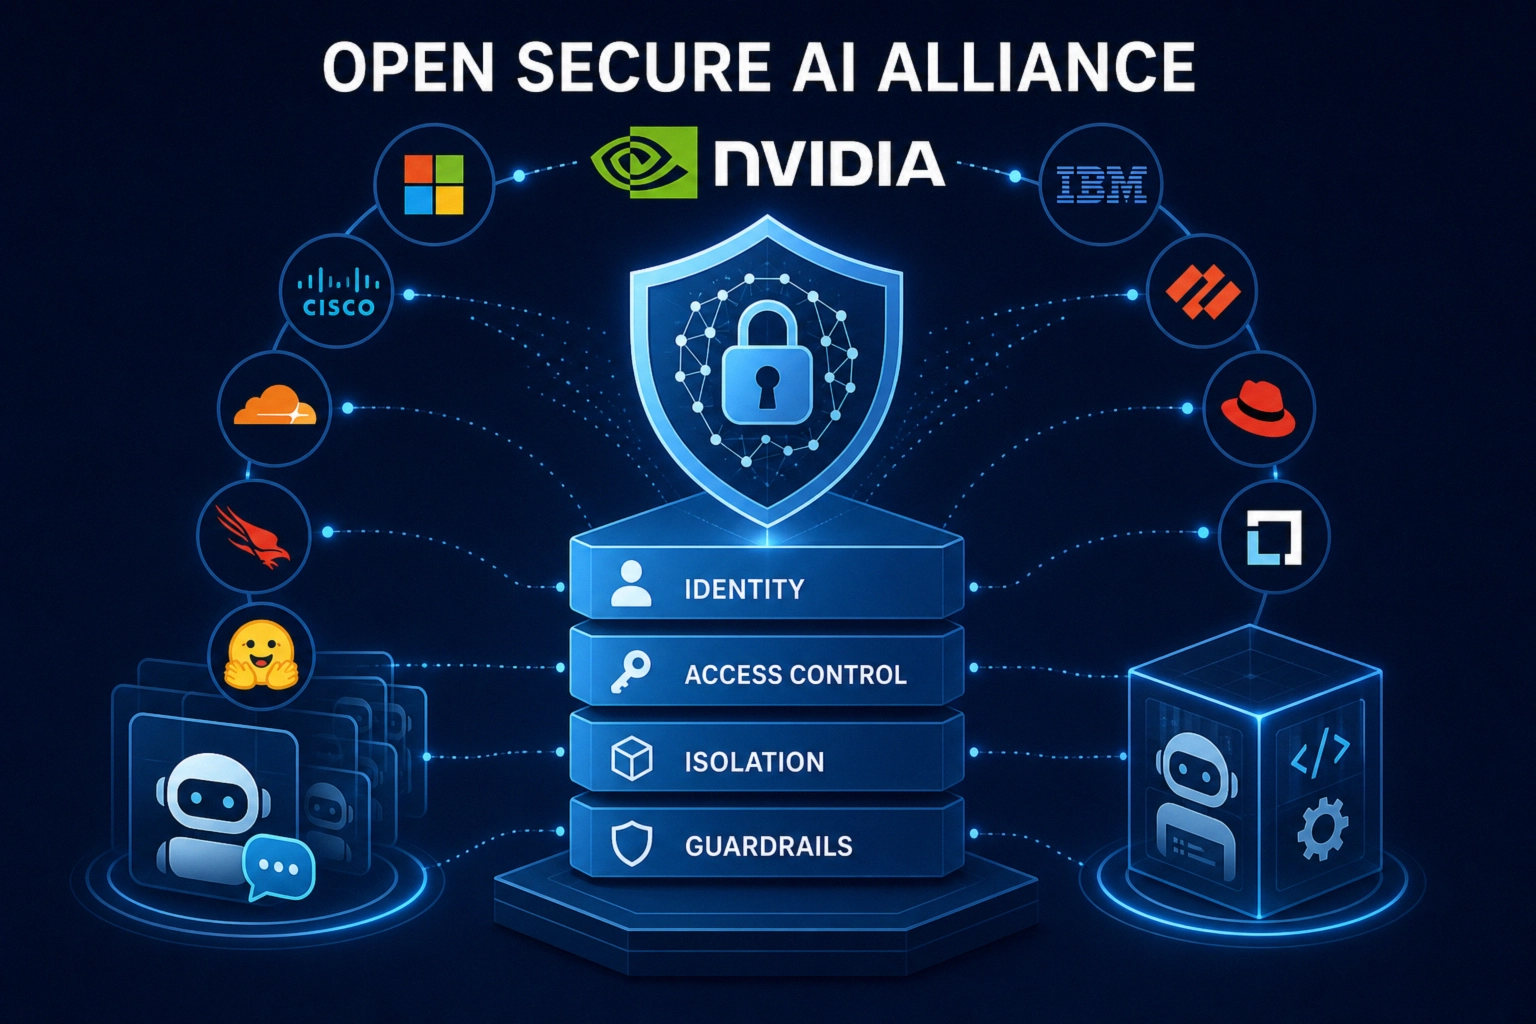
NVIDIA launches Open Secure AI Alliance for secure AI 🔗 https://cybersecurefox.com/en/nvidia-open-secure-ai-alliance-nooa-analysis #NVIDIA #Open #Secure #AI #Alliance #NOOA #Hugging #Face #incident #secure #AI
NVIDIA Launches Open Secure AI Alliance For Secure AI
CyberSecureFox

NVIDIA Launches Open Secure AI Alliance For Secure AI

NVIDIA, together with 36 organizations, announced the creation of the Open Secure AI Alliance—a coalition to develop open technologies for securing software

0
0
0
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
Critical Gitea RCE CVE-2026-60004: Update to 1.27.1 🔗 https://cybersecurefox.com/en/gitea-cve-2026-60004-critical-rce-vulnerability #gitea #cve-2026-60004 #rce #git #hooks #diffpatch
Critical Gitea RCE CVE-2026-60004: Update To 1.27.1
CyberSecureFox

Critical Gitea RCE CVE-2026-60004: Update To 1.27.1

Gitea has fixed a critical remote code execution vulnerability (CVE-2026-60004, CVSS 9.8) that allows a user with write access to a repository to inject an

0
0
0
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
CVE-2026-16812: Critical Arista VCO Flaw Exploited 🔗 https://cybersecurefox.com/en/arista-velocloud-orchestrator-cve-2026-16812-command-injection #arista #velocloud #orchestrator #cve-2026-16812 #sd-wan #command #injection #cisa #kev
CVE-2026-16812: Critical Arista VCO Flaw Exploited
CyberSecureFox

CVE-2026-16812: Critical Arista VCO Flaw Exploited

The critical vulnerability CVE-2026-16812 with a maximum CVSS score of 10.0 in on-premises versions of Arista VeloCloud Orchestrator (VCO) has been confirmed

0
0
0
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
Unpatched IPMI v2.0 Flaw Exposes 36K BMCs Online 🔗 https://cybersecurefox.com/en/ipmi-v20-cve-2013-4786-bmc-password-hash-leak #ipmi #vulnerability #cve-2013-4786 #bmc #security #remote #management #server #management #controller
Unpatched IPMI V2.0 Flaw Exposes 36K BMCs Online
CyberSecureFox

Unpatched IPMI V2.0 Flaw Exposes 36K BMCs Online

According to researchers at Lava, more than 36,000 Baseboard Management Controllers (BMC) using the IPMI protocol are reachable from the public internet, and

0
0
0
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
Cl0p Targets PTC Windchill via CVE-2026-12569 RCE Flaw 🔗 https://cybersecurefox.com/en/ptc-windchill-cve-2026-12569-flexplm-cl0p #ptc #windchill #cve-2026-12569 #cl0p #flexplm #plm #security
Cl0p Targets PTC Windchill Via CVE-2026-12569 RCE Flaw
CyberSecureFox

Cl0p Targets PTC Windchill Via CVE-2026-12569 RCE Flaw

The critical vulnerability CVE-2026-12569 in the PTC Windchill product is being actively exploited as part of a data-theft campaign allegedly linked to the

0
0
0
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
Zoom Patches Critical CVE-2026-53412 in Windows Apps 🔗 https://cybersecurefox.com/en/zoom-critical-cve-2026-53412-windows-update #zoom #cve-2026-53412 #windows #security #update #privilege #escalation
Zoom Patches Critical CVE-2026-53412 In Windows Apps
CyberSecureFox

Zoom Patches Critical CVE-2026-53412 In Windows Apps

Zoom has released emergency security updates addressing critical vulnerability CVE-2026-53412 with a CVSS score of 9.8 in the Zoom Workplace product line for

0
0
0
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
Suno Data Breach Exposes 55.3M User Emails via HIBP 🔗 https://cybersecurefox.com/en/suno-data-breach-have-i-been-pwned-stripe #suno #data #breach #have #i #been #pwned #hibp #stripe #leak #ai #music #security
Suno Data Breach Exposes 55.3M User Emails Via HIBP
CyberSecureFox

Suno Data Breach Exposes 55.3M User Emails Via HIBP

The Have I Been Pwned service has added to its database data stolen in the breach of Suno, a popular AI music generator. According to HIBP, the dump contains

0
0
0
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
Adobe Patches Critical CVE-2026-48449 in Campaign Classic 🔗 https://cybersecurefox.com/en/adobe-campaign-classic-cve-2026-48449-update #Adobe #Campaign #Classic #Adobe #Bridge #CVE-2026-48449 #CVE-2026-48448 #CVSS #10.0
Adobe Patches Critical CVE-2026-48449 In Campaign Classic
CyberSecureFox

Adobe Patches Critical CVE-2026-48449 In Campaign Classic

Adobe has released security updates that address the maximum‑severity vulnerability CVE-2026-48449 (CVSS 10.0) in the marketing automation platform Adobe

0
0
0
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
CVE-2026-8037: CISA Adds Progress LoadMaster Flaw to KEV 🔗 https://cybersecurefox.com/en/cve-2026-8037-progress-kemp-loadmaster #cve-2026-8037 #progress #kemp #loadmaster #cisa #kev #command #injection #exploited #vulnerability
CVE-2026-8037: CISA Adds Progress LoadMaster Flaw To KEV
CyberSecureFox

CVE-2026-8037: CISA Adds Progress LoadMaster Flaw To KEV

On August 7, 2026, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) added vulnerability CVE-2026-8037 to the Known Exploited Vulnerabilities

0
0
0
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
Firefox 151.0.3 Fixes Critical JIT RCE (CVE-2026-10702) 🔗 https://cybersecurefox.com/en/firefox-cve-2026-10702-ionstack-ghostlock #firefox #cve-2026-10702 #ionstack #ghostlock #jit #exploit
Firefox 151.0.3 Fixes Critical JIT RCE (CVE-2026-10702)
CyberSecureFox

Firefox 151.0.3 Fixes Critical JIT RCE (CVE-2026-10702)

Mozilla has released an emergency update Firefox 151.0.3 that fixes the high-severity vulnerability CVE-2026-10702 in the browser’s JIT compiler. The bug

0
0
0
0
Open post
CyberSecureFox :loading: @cybersecurefox@infosec.exchange
· 2mo ago
Malicious VS Code extension 'Solidity Pro' steals crypto 🔗 https://cybersecurefox.com/en/malicious-vscode-extension-solidity-pro #Visual #Studio #Code #Solidity #Pro #malicious #extension #crypto #wallet #stealer #Web3 #security
Malicious VS Code Extension 'Solidity Pro' Steals Crypto
CyberSecureFox

Malicious VS Code Extension 'Solidity Pro' Steals Crypto

Researchers from Yeeth Security discovered the malicious Solidity Pro extension for Microsoft Visual Studio Code which, while masquerading as a tool for

0
0
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Pricing
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 21:29:06 UTC