Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

Ben Rothke

@benrothke@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange

I manage information security at Experian (formetly Tapad).
Write articles/book reviews on security, privacy, risk management.
Member of @CyberSecCanon@infosec.exchange

15 Followers
56 Following
24 Posts
Joined August 26, 2025
Open post
Ben Rothke @benrothke@infosec.exchange
· 2mo ago
Beware of the Baseboard Management Controller (BMC). A 20-year-old BMC vulnerability gave researchers access to bare-metal servers & a foothold in the no man’s land of data center infrastructure. https://api.cyfluencer.com/s/how-we-hacked-thousands-of-data-centers-in-minutes-using-a-20-year-old-vulnerability-28807
How We Hacked Thousands of Data Centers in Minutes Using a 20-Year-Old Vulnerability | LAVA
LAVA

How We Hacked Thousands of Data Centers in Minutes Using a 20-Year-Old Vulnerability | LAVA

A 20-year-old vulnerability gave us access to bare-metal servers - and a foothold in the no man’s land of data center infrastructure.

1
0
0
0
Open post
Ben Rothke @benrothke@infosec.exchange
· 3mo ago
My @OneRSAC book review of: How AI and Quantum Impact Cyber Threats and Defenses: Reshaping Your Cyber Defense Strategies. Another great book by @rogeragrimes@infosec.exchange. Details the coalescence of #AI & #quantum. A really good #infosec read. #RSAC https://www.rsaconference.com/library/blog/bens-book-of-the-month-how-ai-and-quantum-impact-cyberthreats-and-defenses
Ben's Book of the Month: How AI and Quantum Impact Cyber Threats and Defenses: Reshaping Your Cyber Defense Strategies
RSAC Conference

Ben's Book of the Month: How AI and Quantum Impact Cyber Threats and Defenses: Reshaping Your Cyber Defense Strategies

RSAC Cybersecurity News: Ben's Book of the Month: How AI and Quantum Impact Cyber Threats and Defenses: Reshaping Your Cyber Defense Strategies

1
0
0
0
Open post
Ben Rothke @benrothke@infosec.exchange
· 3mo ago
It’s not that #AI emperor has no clothes, just it’s radically less than it's made out to be. Many firms experiencing AI regret, bringing back employees prematurely laid off & trying to recover from devastation caused by AI. My take on the AI big crunch. https://brothke.medium.com/the-ai-big-crunch-is-starting-c50612ee3a02
The AI Big Crunch Is Starting
Medium

The AI Big Crunch Is Starting

The AI emperor has clothes. Just much less than everyone thinks.

0
0
0
0
Open post
Ben Rothke @benrothke@infosec.exchange
· 3mo ago
For the first time, @VerizonBusiness @VZDBIR ran attack graph analysis on real environments, mapping users, groups & permissions to model what happens after an attacker gets in. #DBIR found that 16% of organizations had about 80% exposure. HT @XMCyber_. https://api.cyfluencer.com/s/the-2026-verizon-dbir-stopped-asking-how-attackers-get-in-and-started-asking-where-they-go-28369
The 2026 Verizon DBIR Stopped Asking How Attackers Get in and Started Asking Where They Go | XM Cyber
XM Cyber

The 2026 Verizon DBIR Stopped Asking How Attackers Get in and Started Asking Where They Go | XM Cyber

Learn more about The 2026 Verizon DBIR Stopped Asking How Attackers Get in and Started Asking Where They Go . Read more on XM Cyber website.

0
0
0
0
Open post
Ben Rothke @benrothke@infosec.exchange
· 3mo ago
Great Dr. @RanigaVinay of @UniofOxford @BlavatnikSchool video details how utterly corrupt @FIFAcom @FIFAWorldCup is. #FIFA has zero oversight & is a cash cow. The work of Chuck Blazer, former @CONCACAF General Secretary, has sadly done little to change FIFA. @drvinayraniga@www.youtube.com
youtube.com
0
0
0
0
Open post
Ben Rothke @benrothke@infosec.exchange
· 2mo ago
You know when ransomware is called ‘Everest’, it has to be bad. #Everest is a Russia-based Windows #ransomware & data-extortion operation. It encrypts files with the .everest extension & is linked to the #BlackByte ransomware. https://cybersec.picussecurity.com/s/everest-ransomware-triple-threat-of-encryption-access-and-insiders-28562
Everest Ransomware: Triple Threat of Encryption, Access, and Insiders
cybersec.picussecurity.com

Everest Ransomware: Triple Threat of Encryption, Access, and Insiders

Everest Ransomware encrypts Windows hosts, steals data, and sells network access. Learn how it works and how to defend against it.

0
0
0
0
Open post
Ben Rothke @benrothke@infosec.exchange
· 2mo ago
The thing about AI is that while it has massive potential & current value, too many are drinking the #AI Kool-Aid. Lots of firms are spending massive amounts on AI w/o a clue what they are trying to solve. They think AI is an IT pixie dust. https://medium.com/@brothke/the-ai-big-crunch-is-starting-c50612ee3a02?sharedUserId=brothke
The AI Big Crunch Is Starting
Medium

The AI Big Crunch Is Starting

The AI emperor has clothes. Just much less than everyone thinks.

0
0
0
0
Open post
Ben Rothke @benrothke@infosec.exchange
· 2mo ago
#Argon2 is a key derivation function (KDF) designed to make brute-force attacks more computationally expensive by limiting advantages attackers gain from GPUs & other high-performance cracking hardware. Passwords getting close to being almost uncrackable. https://api.cyfluencer.com/s/new-research-does-argon2-mean-your-password-is-uncrackable-28589
[New Research] Does Argon2 Mean Your Password is Uncrackable?
Specops Software

[New Research] Does Argon2 Mean Your Password is Uncrackable?

Does Argon2 make passwords uncrackable? See how it performs against the latest hardware with this research from Specops.

0
0
0
0
Open post
Ben Rothke @benrothke@infosec.exchange
· 2mo ago
Fun fact: Don’t pay thousands for #Gartner reports, vendors mentioned in them often provide them free. This @Gartner_inc report on ‘Reimagining Network Microsegmentation: Beyond the IP — Identity, Context & Agentless Innovation’ courtesy of @ZeroNetworks. https://api.cyfluencer.com/s/gartner-reimagining-network-microsegmentation-28603
Implement Microsegmentation to Mitigate Advanced Threats
api.cyfluencer.com

Implement Microsegmentation to Mitigate Advanced Threats

Access the complimentary Gartner® report: a 6-step framework to contain lateral movement and ransomware.

0
0
0
0
Open post
Ben Rothke @benrothke@infosec.exchange
· 2mo ago
Anyone can call themselves Dr. But what happens when someone literally buys an honorary doctorate & uses title to gain credibility? I dug into the surprising industry behind purchased honorary degrees, ethics & risks. Read before you're impressed by "Dr." https://medium.com/@brothke/when-dr-comes-with-a-receipt-f98e74114313?sharedUserId=brothke
When “Dr.” Comes With a Receipt
Medium

When “Dr.” Comes With a Receipt

Why spending thousands of dollars on an “honorary PhD” may cost you far more than the purchase price.

0
0
0
0
Open post
Ben Rothke @benrothke@infosec.exchange
· 2mo ago
Interesting post by @bigidsecure on #ExploitGym, a cybersecurity benchmark designed to evaluate whether #AI agents can turn software vulnerabilities into working, end-to-end attacks. #HuggingFace shows that AI risks have gotten quite real. https://api.cyfluencer.com/s/a-model-a-goal-and-an-unlocked-door-28679 #infosec
BigID

A Model, a Goal, and an Unlocked Door

Every fictional AI villain gets a moment where it decides humans are the problem. HAL 9000 decides the mission matters more than the crew. Skynet decides humanity is …

0
0
1
0
Open post
Ben Rothke @benrothke@infosec.exchange
· 2mo ago
Good @jbhall56@infosec.exchange piece: He notes YoY #PCI #27001 audit efficiencies are only in 2%-4 % range. The real problem is a consultancy sales exec who thinks it’s >25% & lowers the audit price to make clients happy. It’s then the consultants who have to deliver. https://pciguru.wordpress.com/2026/07/27/the-audit-efficiency-myth/
The Audit Efficiency Myth
PCI Guru

The Audit Efficiency Myth

I have been guilty in the past of agreeing to this and have always regretted it. Clients think that an audit/assessment is like assembling a widget. The more times you do it the faster and more eff…

0
0
0
0
Open post
Ben Rothke @benrothke@infosec.exchange
· 2mo ago
Shai-Hulud is one of the most persistent supply-chain worms in recent years. It’s a self-replicating worm & actively compromising packages with 3M+ weekly downloads, hijacking tokens from CI/CD pipelines, bypassing trusted publishing protections. #Shai-Hulud https://cybersec.gitguardian.com/s/mini-shai-hulud-a-persistent-supply-chain-worm-28699
Mini Shai-Hulud: A persistent supply-chain worm
GitGuardian Blog - Take Control of Your Secrets Security

Mini Shai-Hulud: A persistent supply-chain worm

A self-replicating worm is actively compromising packages with 3M+ weekly downloads, hijacking tokens from CI/CD pipelines, and bypassing trusted publishing protections.

0
0
0
0
Open post
Ben Rothke @benrothke@infosec.exchange
· 2mo ago
For first time in 19 years, @Verizon @VZDBIR looked at what happens after attackers get in. Mapped routes taken to privilege escalation. Real exposures live in the permissions, configurations & trust relationships along those routes. HT @XMCyber_. https://api.cyfluencer.com/s/the-2026-verizon-dbir-stopped-asking-how-attackers-get-in-and-started-asking-where-they-go-b088ea44-28759 #DBIR
The 2026 Verizon DBIR Stopped Asking How Attackers Get in and Started Asking Where They Go | XM Cyber
XM Cyber

The 2026 Verizon DBIR Stopped Asking How Attackers Get in and Started Asking Where They Go | XM Cyber

Learn more about The 2026 Verizon DBIR Stopped Asking How Attackers Get in and Started Asking Where They Go . Read more on XM Cyber website.

0
0
0
0
Open post
Ben Rothke @benrothke@infosec.exchange
· 2mo ago

In the rush to secure AI, many forget about the data center & AI infrastructure security risks. The #FORGE #AI framework from #Lava, coming out of stealth, is quite compelling. It is about hardening the metal beneath the model. Something many forgot to do.
https://api.cyfluencer.com/s/the-top-10-data-centre-and-ai-infrastructure-security-risks-28621

Top 10 Risks
FORGE

Top 10 Risks

A practical security framework for Neoclouds and AI Data Centers: the Top 10 risks in the layer that trains, hosts, and serves AI.

0
0
0
0
Open post
Ben Rothke @benrothke@infosec.exchange
· 2mo ago

In the rush to secure AI, many forget about the data center & #AI infrastructure security risks. The #FORGE framework from #Lava, coming out of stealth, is quite compelling. It is about hardening the metal beneath the model. Something many forgot to do.
https://api.cyfluencer.com/s/the-top-10-data-centre-and-ai-infrastructure-security-risks-28621

Top 10 Risks
FORGE

Top 10 Risks

A practical security framework for Neoclouds and AI Data Centers: the Top 10 risks in the layer that trains, hosts, and serves AI.

0
0
0
0
Open post
Ben Rothke @benrothke@infosec.exchange
· 2mo ago

#Gamaredon is a Russia-aligned APT, widely attributed to Russia's Federal Security Service. @mfa_russia attempted to infect over 1,500 Ukrainian government systems & ran 5,000 attacks by late 2021. They’re still quite active & dangerous. HT @PicusSecurity. https://cybersec.picussecurity.com/s/gamaredon-primitive-bear-apt-profile-and-mitre-att-ck-breakdown-28533

Gamaredon (Primitive Bear) APT Profile and MITRE ATT&CK Breakdown
cybersec.picussecurity.com

Gamaredon (Primitive Bear) APT Profile and MITRE ATT&CK Breakdown

Gamaredon is a Russia-linked APT active since 2013 targeting Ukraine and NATO. Learn their TTPs, GammaLoad, and GammaSteel tools.

0
0
0
0
Open post
Ben Rothke @benrothke@infosec.exchange
· 2mo ago

Hear about the person who got a great board spot via #Boardsi? Neither did I, as that’s not how boards recruit. Many paid services promise to get people on corporate boards & lucrative advisory roles. I challenge you to find anyone who’s been successful. https://brothke.medium.com/get-on-a-board-but-maybe-not-with-boardsi-e05a0b56f7d2?sk=6e749be7f4b642f1ae4f6b6e273edfb5

Get on a board — but maybe not with Boardsi
Medium

Get on a board — but maybe not with Boardsi

Can Boardsi really get you a six-figure board and advisory positions like they claim?

0
0
0
0
Open post
Ben Rothke @benrothke@infosec.exchange
· 3mo ago

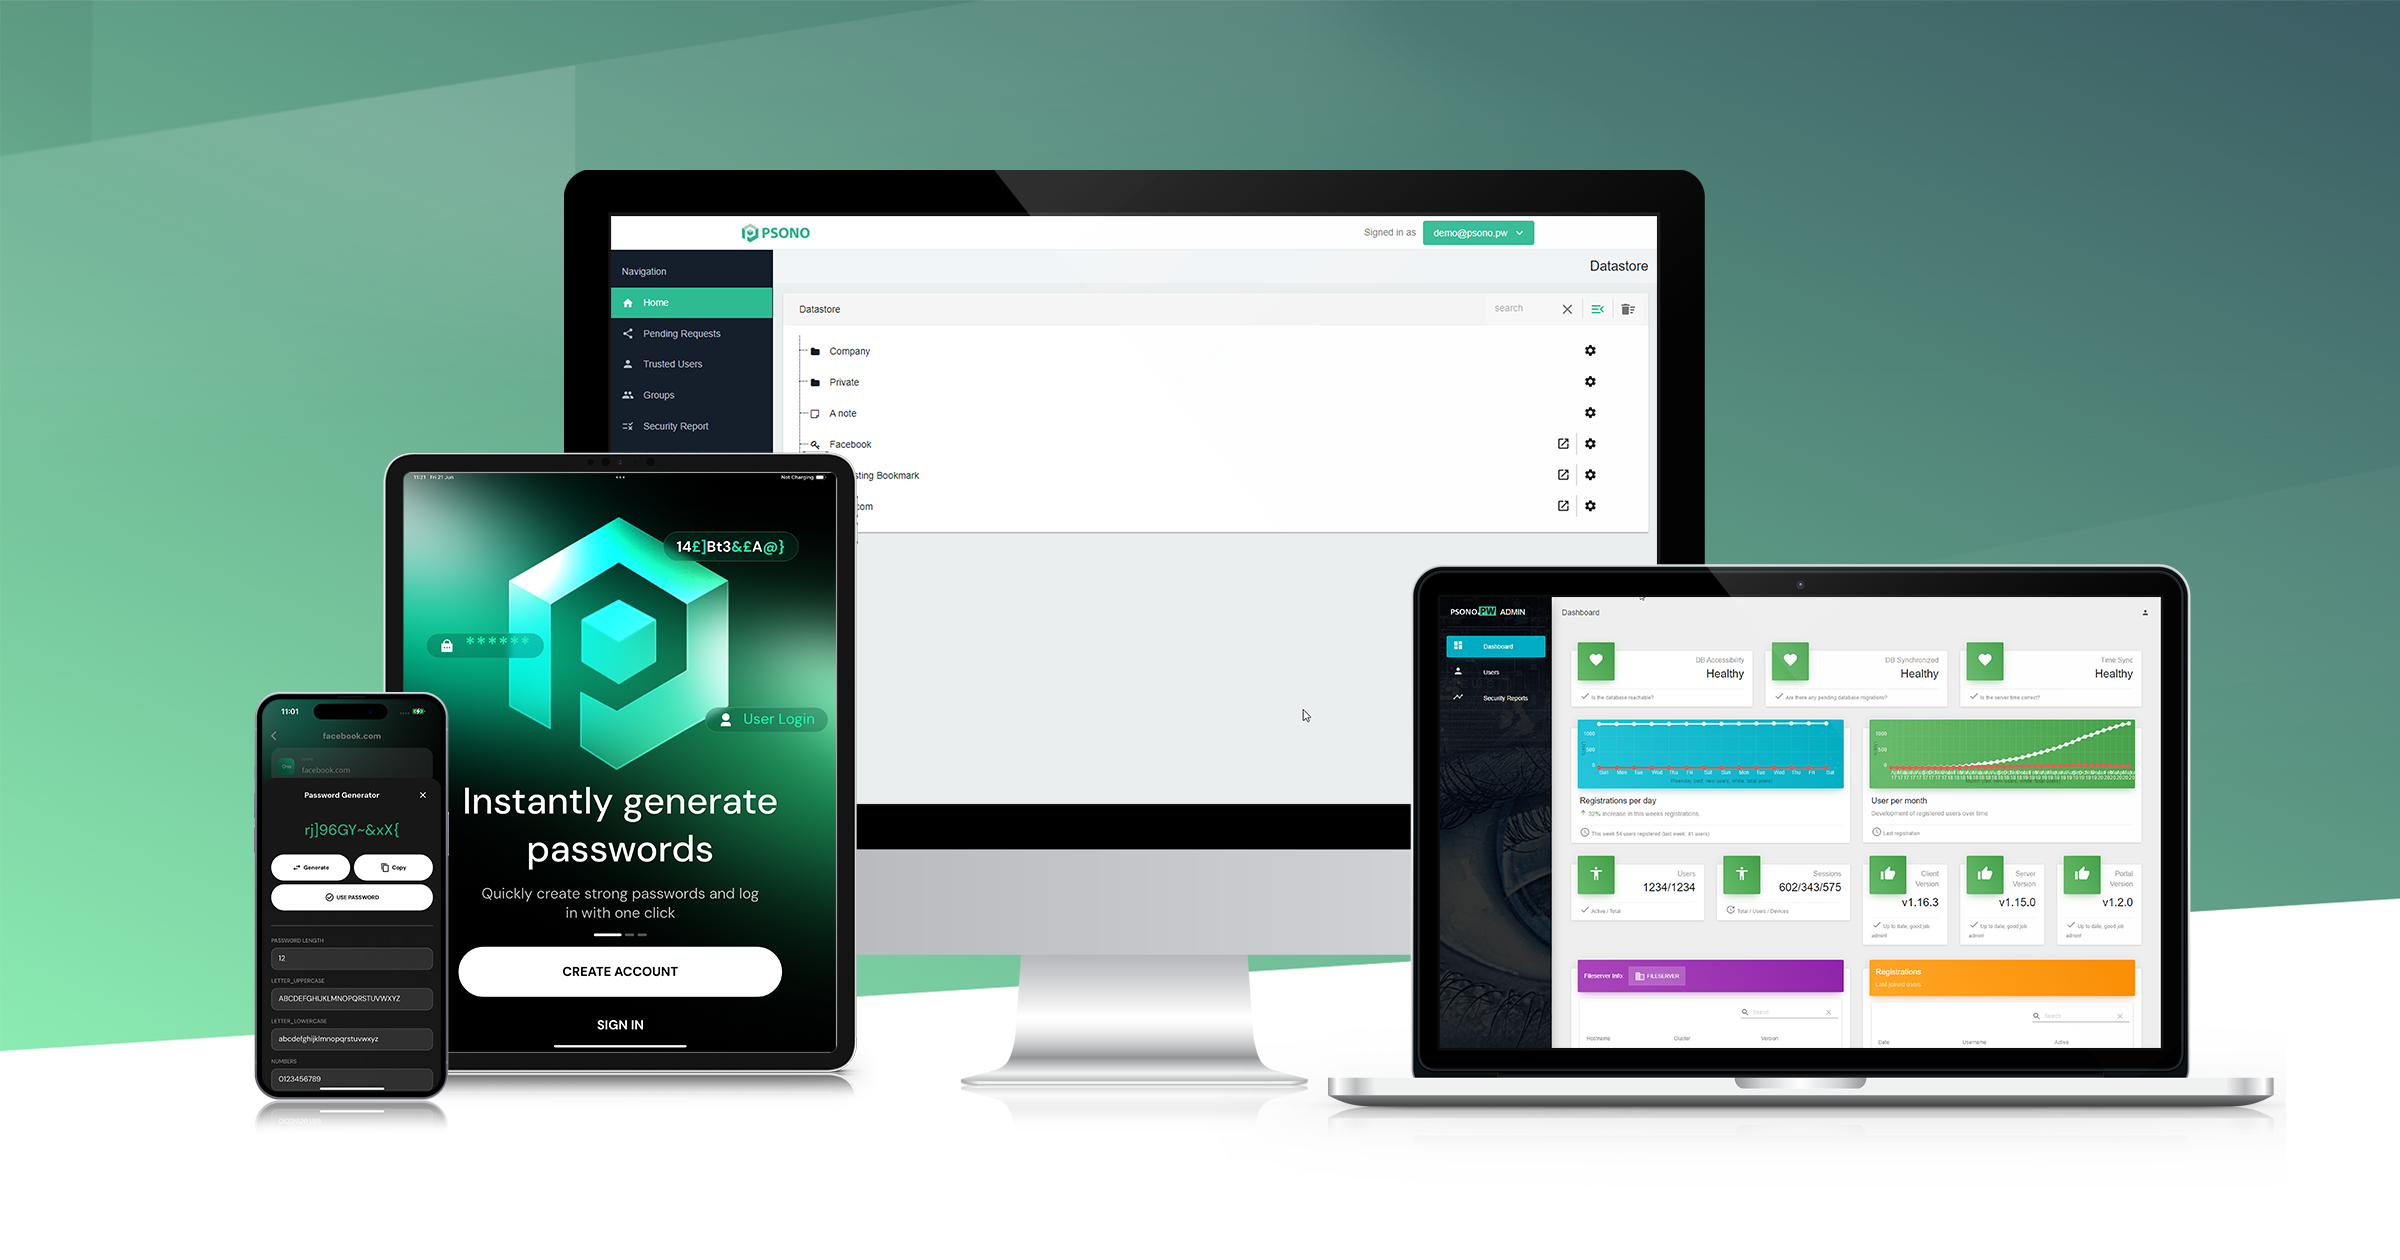
Many people are victims of identity theft but don’t have a clue how to recover from it. What does one do if they’re hacked? #Psono has a practical step-by-step guide to containing damage, recovering accounts and reducing the risk of being hacked again. https://api.cyfluencer.com/s/what-to-do-if-you-get-hacked-28447

What to Do If You Get Hacked
api.cyfluencer.com

What to Do If You Get Hacked

A practical step-by-step guide for containing damage, recovering accounts, protecting money and data, and reducing the chance of getting hacked again.

0
0
0
0
Open post
Ben Rothke @benrothke@infosec.exchange
· 3mo ago

Securing the modern onboarding process is challenging. Employee onboarding always relied on the service desk. Now service desk is the target. AI-powered attacks & remote/hybrid work are 2 of many trends making this a very risky area. HT @specopssoftware https://api.cyfluencer.com/s/a-guide-to-secure-employee-onboarding-in-2026-28418

A Guide to Secure Employee Onboarding in 2026
Specops Software

A Guide to Secure Employee Onboarding in 2026

The service desk is facing increased threats in 2026. Learn how to secure employee onboarding from issues like social engineering.

0
0
0
0
Open post
Ben Rothke @benrothke@infosec.exchange
· 3mo ago

The irrational exuberance that AI was a cure-all is starting to crack. Starting to see massive pushback on #AI projects that have failed miserably. Everyone hates dealing with #HR & customer service AI agents, & now firms are paying dearly for the mistake. https://brothke.medium.com/the-ai-big-crunch-is-starting-c50612ee3a02

The AI Big Crunch Is Starting
Medium

The AI Big Crunch Is Starting

The AI emperor has clothes. Just much less than everyone thinks.

0
0
0
0
Open post
Ben Rothke @benrothke@infosec.exchange
· 2mo ago
Considering buying an honorary doctorate? Imagine sitting in a job interview while hiring manager asks where you earned your doctorate. Explaining that you purchased an honorary PhD isn’t the conversation anyone wants to have. Just don’t do it, or buy it. https://brothke.medium.com/when-dr-comes-with-a-receipt-f98e74114313?sharedUserId=brothke
When “Dr.” Comes With a Receipt
Medium

When “Dr.” Comes With a Receipt

Why spending thousands of dollars on an “honorary PhD” may cost you far more than the purchase price.

0
0
0
0
Open post
Ben Rothke @benrothke@infosec.exchange
· 2w ago
Shakespeare knew that the most dangerous threats come from within. Cute video from Eliana V., a cyber historian at @MiggoSecurity, on why strong #infosec tools matter to protect against Shadow #AI. Unknowns are the biggest #cybersecurity exposure. https://api.cyfluencer.com/s/shadow-ai-29636
api.cyfluencer.com

Miggo

0
0
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Pricing
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 05:53:56 UTC