Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

Raj Samani

@Raj_Samani@ioc.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on ioc.exchange

Chief Scientist at Rapid7 (ex McAfee) | Cloud Security Alliance - Chief Innovation Officer | Co-author of Smart Grid Cyber Book & CSA Guide to Cloud | Advisor Europol European Cybercrime Centre (EC3)

579 Followers
46 Following
19 Posts
Joined October 31, 2022
Twiitter:
twitter.com/Raj_Samani
LinkedIn:
www.linkedin.com/in/rajsamani
Open post
Raj Samani @Raj_Samani@ioc.exchange
· 5mo ago

We’re happy to announce that Metasploit Framework had a big week, landing seven new modules alongside various bug fixes and enhancements

https://www.rapid7.com/blog/post/pt-metasploit-wrap-up-04-17-2026/

#metasploit #vulnerability

Rapid7
Rapid7

Rapid7

The Metasploit Framework received a major update, introducing seven new modules alongside various bug fixes and enhancements. Four new Remote Code Execution (RCE) exploit modules were added this week. These RCE modules target critical vulnerabilities in AVideo (unauthenticated SQLi for credential dumping), openDCIM (chained SQLi to RCE), ChurchCRM (file upload RCE), and a unified module for unauthenticated Selenium Grid/Selenoid instances. For post-exploitation, three new Windows persistence tec

1
0
0
0
Open post
Raj Samani @Raj_Samani@ioc.exchange
· 37mo ago

Our latest Rapid7 analysis details observed Exploitation of Cisco ASA SSL VPNs, further details including IoCs located here: https://www.rapid7.com/blog/post/2023/08/29/under-siege-rapid7-observed-exploitation-of-cisco-asa-ssl-vpns/

Under Siege: Rapid7-Observed Exploitation of Cisco ASA SSL VPNs | Rapid7 Blog
Rapid7

Under Siege: Rapid7-Observed Exploitation of Cisco ASA SSL VPNs | Rapid7 Blog

Rapid7’s managed detection and response (MDR) teams have observed increased threat activity targeting Cisco ASA SSL VPN appliances (physical and virtual) dating back to at least March 2023, including several incidents that ended in ransomware deployment.

4
0
4
0
Open post
Raj Samani @Raj_Samani@ioc.exchange
· 34mo ago

We are hiring! Great opportunity to join the vulnerability and exploit research team. More details here: https://careers.rapid7.com/jobs/lead-security-researcher-united-states #infosec #infosecjobs

careers.rapid7.com
3
0
3
0
Open post
Raj Samani @Raj_Samani@ioc.exchange
· 36mo ago

We are seeing multiple instances of WS_FTP exploitation in the wild. Further details of this and the vulnerabilities in the advisory, two of which are critical (CVE-2023-40044 and CVE-2023-42657) available in our
Rapid7 advisory: https://www.rapid7.com/blog/post/2023/09/29/etr-critical-vulnerabilities-in-ws_ftp-server/

rapid7.com
3
0
1
0
Open post
Raj Samani @Raj_Samani@ioc.exchange
· 38mo ago

Our latest analysis details CVE-2023-35082, a new vulnerability that allows unauthenticated attackers to access the API in older unsupported versions of MobileIron Core (11.2 and below). https://www.rapid7.com/blog/post/2023/08/02/cve-2023-35082-mobileiron-core-unauthenticated-api-access-vulnerability/ #infosec #cybersecurity

CVE-2023-35082 MobileIron Core Unauthenticated API Access | Rapid7 Blog
Rapid7

CVE-2023-35082 MobileIron Core Unauthenticated API Access | Rapid7 Blog

Rapid7 discovered a new vulnerability that allows unauthenticated attackers to access the API in unsupported versions of MobileIron Core (11.2 and below).

3
0
3
0
Open post
Raj Samani @Raj_Samani@ioc.exchange
· 40mo ago

New Velociraptor artifact now available that "enables scoping EventLogs from Progress Software’s MoveIT File Transfer. It is designed to assist in identifying exfiltration resulting from the exploitation of CVE-2023-34362" https://docs.velociraptor.app/exchange/artifacts/pages/moveitevtx/ #DFIR #Infosec #cybersecurity

Windows.EventLogs.MoveIt
docs.velociraptor.app

Windows.EventLogs.MoveIt

This Artifact enables scoping EventLogs from Progress Software's MoveIT File Transfer. It is designed to assist in identifying exfiltration resulting from the exploitation of CVE-2023-34362

2
0
0
0
Open post
Raj Samani @Raj_Samani@ioc.exchange
· 33mo ago

Our latest @rapid7@ioc.exchange analysis details Critical CVEs in Outdated Versions of Atlassian Confluence and VMware vCenter Server https://www.rapid7.com/blog/post/2024/01/19/etr-critical-cves-in-outdated-versions-of-atlassian-confluence-and-vmware-vcenter-server/

Critical CVEs in Outdated Versions of Atlassian Confluence & VMware | Rapid7 Blog
Rapid7

Critical CVEs in Outdated Versions of Atlassian Confluence & VMware | Rapid7 Blog

Rapid7 is highlighting two critical vulnerabilities in outdated versions of widely deployed software this week. CVE-2023-22527 & CVE-2023-34048.

1
0
1
0
Open post
Raj Samani @Raj_Samani@ioc.exchange
· 33mo ago

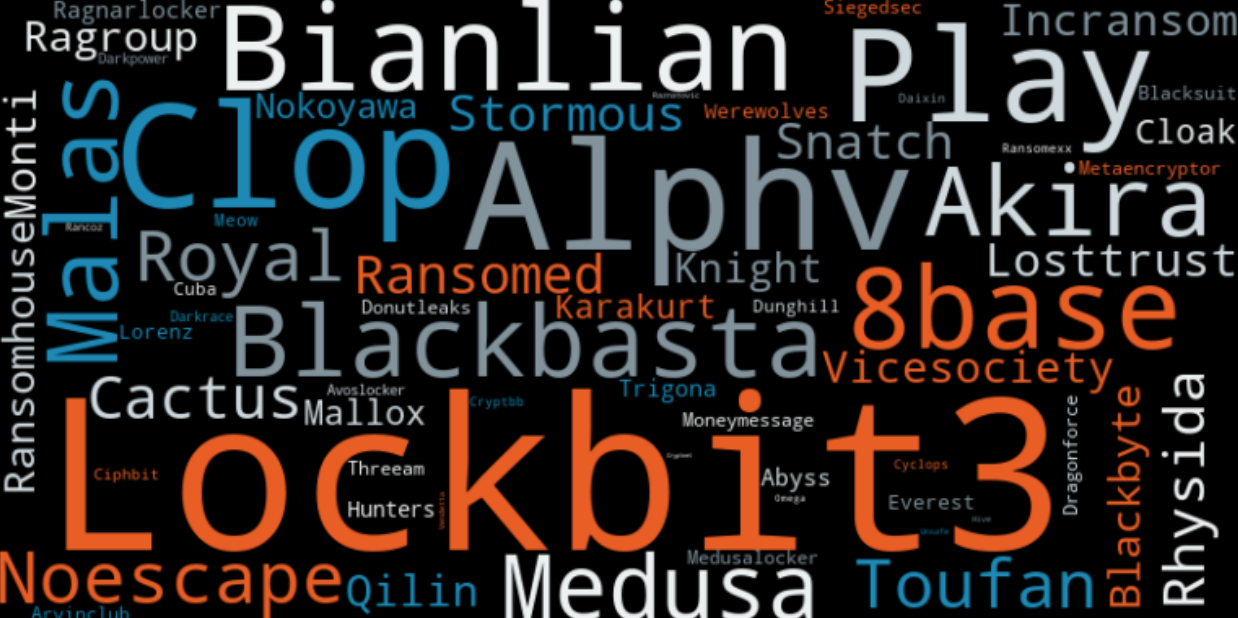
Our latest Rapid7 Labs publication details an assessment of the hashtag#ransomware landscape detailing the most common threat groups and the common patterns and methodologies observed in the majority of ransomware attacks.: https://www.rapid7.com/blog/post/2024/01/12/2023-ransomware-stats-a-look-back-to-plan-ahead/ #infosec #cybersecurity H/T @ChristiaanB@infosec.exchange

2023 Ransomware Stats | Rapid7 Blog
Rapid7

2023 Ransomware Stats | Rapid7 Blog

What can the 2023 ransomware stats tell us about the year that was, and how can we use them to plan for the year ahead?

1
0
0
0
Open post
Raj Samani @Raj_Samani@ioc.exchange
· 34mo ago

@theomegabit@infosec.exchange nice to meet you. We have a lot of the team here who are posting and also @metasploit@infosec.exchange posts much of our content.

1
0
0
0
Open post
Raj Samani @Raj_Samani@ioc.exchange
· 36mo ago

We have now posted our @rapid7@ioc.exchange analysis into CVE-2023-40044, a .NET deserialization vulnerability affecting the Ad Hoc Transfer module of WS_FTP Server. Now available on @AttackerKb https://attackerkb.com/topics/bn32f9sNax/cve-2023-40044/rapid7-analysis

attackerkb.com

CVE-2023-40044: Deserialization of Untrusted Data | Rapid7 Vulnerability Database

CVE-2023-40044: Deserialization of Untrusted Data. View severity, references, and remediation details from Rapid7.

1
0
0
0
Open post
Raj Samani @Raj_Samani@ioc.exchange
· 38mo ago

Our latest research analyses a dozen medical infusion pumps available for purchase on the secondary market, and how these were not properly decommissioned before being sold: https://www.rapid7.com/blog/post/2023/08/02/security-implications-improper-deacquisition-medical-infusion-pumps/ #infosec

Poorly Purged Medical Devices Present Security Concerns After Sale on Secondary Market | Rapid7 Blog
Rapid7

Poorly Purged Medical Devices Present Security Concerns After Sale on Secondary Market | Rapid7 Blog

In Security Implications from Improper De-acquisition of Medical Infusion Pumps Rapid7 performs a physical and technical teardown of more than a dozen medical infusion pumps.

1
0
0
0
Open post
Raj Samani @Raj_Samani@ioc.exchange
· 40mo ago

Further details on CVE-2023-2868: Total Compromise of Physical Barracuda ESG Appliances - note we have identified malicious activity that took place as far back as November 2022: https://www.rapid7.com/blog/post/2023/06/08/etr-cve-2023-2868-total-compromise-of-physical-barracuda-esg-appliances/ #cybersecurity #înfosec

CVE-2023-2868: Total Compromise of Physical Barracuda ESG Appliances | Rapid7 Blog
Rapid7

CVE-2023-2868: Total Compromise of Physical Barracuda ESG Appliances | Rapid7 Blog

Rapid7 incident response teams are investigating exploitation of physical Barracuda Networks Email Security Gateway (ESG) appliances.

1
1
2
0
Open post
Raj Samani @Raj_Samani@ioc.exchange
· 4mo ago

More on the Cisco SD-WAN 0day on the latest Hacktics and Telemetry podcast with @fulmetalpackets@infosec.exchange https://www.youtube.com/watch?v=tg4TkzDIrKw

#infosec #vulnerability

Hacktics and Telemetry, E6: Cisco SD-WAN Zero-Days, Mythos AI, and Pwn2Own Drama (ft. Stephen Fewer)

0
0
0
0
Open post
Raj Samani @Raj_Samani@ioc.exchange
· 35mo ago

Our latest @rapid7analysis details CVE-2023-47426, a zero-day path traversal vulnerability affecting on-premise SysAid servers. Including IoCs and @velocidex
artifact: https://www.rapid7.com/blog/post/2023/11/09/etr-cve-2023-47246-sysaid-zero-day-vulnerability-exploited-by-lace-tempest/ #infosec

SysAid Zero-Day Vulnerability Exploited By Lace Tempest | Rapid7 Blog
Rapid7

SysAid Zero-Day Vulnerability Exploited By Lace Tempest | Rapid7 Blog

A new zero-day vulnerability in SysAid IT service management software is being exploited by the threat group responsible for the MOVEit Transfer attack.

0
0
0
0
Open post
Raj Samani @Raj_Samani@ioc.exchange
· 36mo ago

Our latest @rapid7@ioc.exchange advisory details CVE-2023-20198: Active Exploitation of Cisco IOS XE Zero-Day Vulnerability - IoCs and observed attacker behaviour included; https://www.rapid7.com/blog/post/2023/10/17/etr-cve-2023-20198-active-exploitation-of-cisco-ios-xe-zero-day-vulnerability/

Active Exploitation of Cisco IOS XE Zero-Day Vulnerability | Rapid7 Blog
Rapid7

Active Exploitation of Cisco IOS XE Zero-Day Vulnerability | Rapid7 Blog

On October 16, Cisco’s Talos group released a blog on an active threat campaign exploiting CVE-2023-20198, a zero-day vuln in Cisco IOS XE software.

0
0
0
0
Open post
Raj Samani @Raj_Samani@ioc.exchange
· 37mo ago

Our latest @rapid7@ioc.exchange advisory details CVE-2023-42793: Critical Authentication Bypass in JetBrains TeamCity CI/CD Servers. More details here https://www.rapid7.com/blog/post/2023/09/25/etr-cve-2023-42793-critical-authentication-bypass-in-jetbrains-teamcity-ci-cd-servers/

rapid7.com
0
0
0
0
Open post
Raj Samani @Raj_Samani@ioc.exchange
· 37mo ago

Our latest @rapid7@ioc.exchange analysis details a new loader to execute infostealers on compromised systems including StealC and Lumma. More details including IoCs available here https://www.rapid7.com/blog/post/2023/08/31/fake-update-utilizes-new-idat-loader-to-execute-stealc-and-lumma-infostealers/?utm_campaign=sm-EA&utm_source=linkedin&utm_medium=organic-social #infosec #malware

Fake Update Utilizes New IDAT Loader To Execute StealC and Lumma Infostealers | Rapid7 Blog
Rapid7

Fake Update Utilizes New IDAT Loader To Execute StealC and Lumma Infostealers | Rapid7 Blog

Rapid7 has observed the Fake Browser Update lure utilizing a sophisticated new loader to execute infostealers.

0
0
0
0
Open post
Raj Samani @Raj_Samani@ioc.exchange
· 38mo ago

Our @metasploit@infosec.exchange weekly wrap up details two new exploit modules leveraging CVE-2023-34960 Chamilo versions 1.11.18 and below and CVE-2023-26469 in Jorani 1.0.0 - more details here: https://www.rapid7.com/blog/post/2023/08/25/metasploit-weekly-wrap-up-24/ #infosec

Metasploit Weekly Wrap-Up: Aug. 25, 2023 | Rapid7 Blog
Rapid7

Metasploit Weekly Wrap-Up: Aug. 25, 2023 | Rapid7 Blog

New features & improvements start with two new exploit modules leveraging CVE-2023-34960 Chamilo versions 1.11.18 & CVE-2023-26469 in Jorani 1.0.0

0
0
1
0
Open post
Raj Samani @Raj_Samani@ioc.exchange
· 40mo ago

ICYMI We recently released @velocidex Artifact that "enables scoping EventLogs from Progress Software’s MoveIT File Transfer. It is designed to assist in identifying exfiltration resulting from the exploitation of CVE-2023-34362" https://docs.velociraptor.app/exchange/artifacts/pages/moveitevtx/
Windows.EventLogs.MoveIt
docs.velociraptor.app

Windows.EventLogs.MoveIt

This Artifact enables scoping EventLogs from Progress Software's MoveIT File Transfer. It is designed to assist in identifying exfiltration resulting from the exploitation of CVE-2023-34362

0
0
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Pricing
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 07:13:19 UTC