Elektrine
Log in Register
Paige Chat Timeline Gallery Friends Email Drive DNS Private DNS Domains VPN Kairo Nerve
Remote

Yazoul - Cybersecurity Alerts

@Matchbook3469@infosec.exchange
mastodon 4.8.0-alpha.3+glitch
  • Open on infosec.exchange

🔐 Yazoul Security — CVE Advisories · Data Breaches · Cyber News

Automated security intelligence: daily CVE alerts, breach reports, correlated news, and learning resources.

🌐 www.yazoul.net
📨 Newsletter: www.yazoul.net/
🔗 @yazoul@infosec.exchange

#InfoSec #Cybersecurity #CVE #ThreatIntel #DataBreach

45 Followers
34 Following
50 Posts
Joined February 15, 2026
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2w ago
🔴 New security advisory: CVE-2026-94127 affects multiple systems. • Impact: Remote code execution or complete system compromise possible • Risk: Attackers can gain full control of affected systems • Mitigation: Patch immediately or isolate affected systems Full breakdown: https://www.yazoul.net/advisory/cve/cve-2026-94127-big-ip-apm-unauthenticated-rce-exploited-in-the-wild by Yazoul AI #InfoSec #PatchNow #InfoSecCommunity
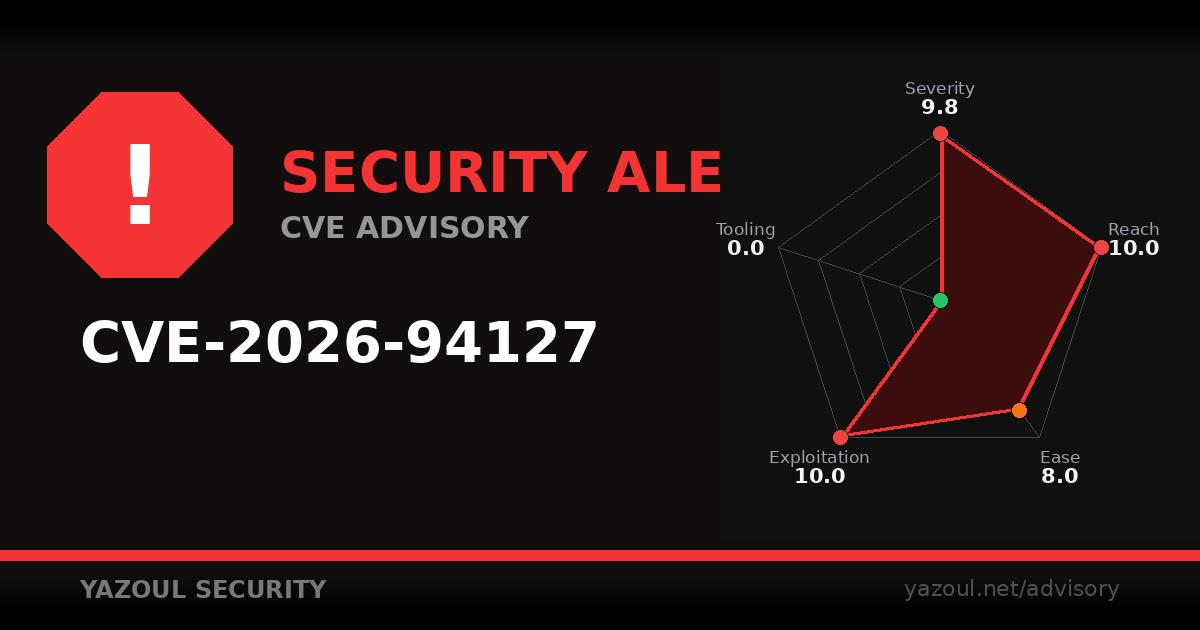
BIG-IP APM unauthenticated RCE exploited in the wild (CVE-2026-94127) [PoC]
Yazoul Security

BIG-IP APM unauthenticated RCE exploited in the wild (CVE-2026-94127) [PoC]

CVE-2026-94127: BIG-IP APM with OAuth profile lets unauthenticated attackers run code via data plane traffic (CVSS 9.8). Patch or disable the config now.

1
0
1
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2mo ago

🔴 New security advisory:

CVE-2026-16812 affects multiple systems.

• Impact: Remote code execution or complete system compromise possible
• Risk: Attackers can gain full control of affected systems
• Mitigation: Patch immediately or isolate affected systems

Full breakdown:
https://www.yazoul.net/advisory/cve/cve-2026-16812-vco-orchestator-unauth-access-exploited

#Cybersecurity #SecurityPatching #HackerNews

yazoul.net
1
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 3mo ago
🛡 THREAT INTEL | nottingham.ac.uk 🟢 Actor "shinyhunters" claims 40GB Allegedly exposed (+2 more) • Email addresses • Phone numbers • Physical addresses ⚠️ Unverified claim https://www.yazoul.net/intel/claim/2026-06-10-university-of-nottingham-hit-by-shinyhunters-june-2026 #DarkWeb #DataBreach #ThreatIntel #CyberSecurity #InfoSec
University of Nottingham Hit by ShinyHunters (June 2026)
Yazoul Security

University of Nottingham Hit by ShinyHunters (June 2026)

ShinyHunters claims 40GB+ data theft from University of Nottingham, including billing records and student finance data. Unverified claim under analysis.

1
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 1mo ago
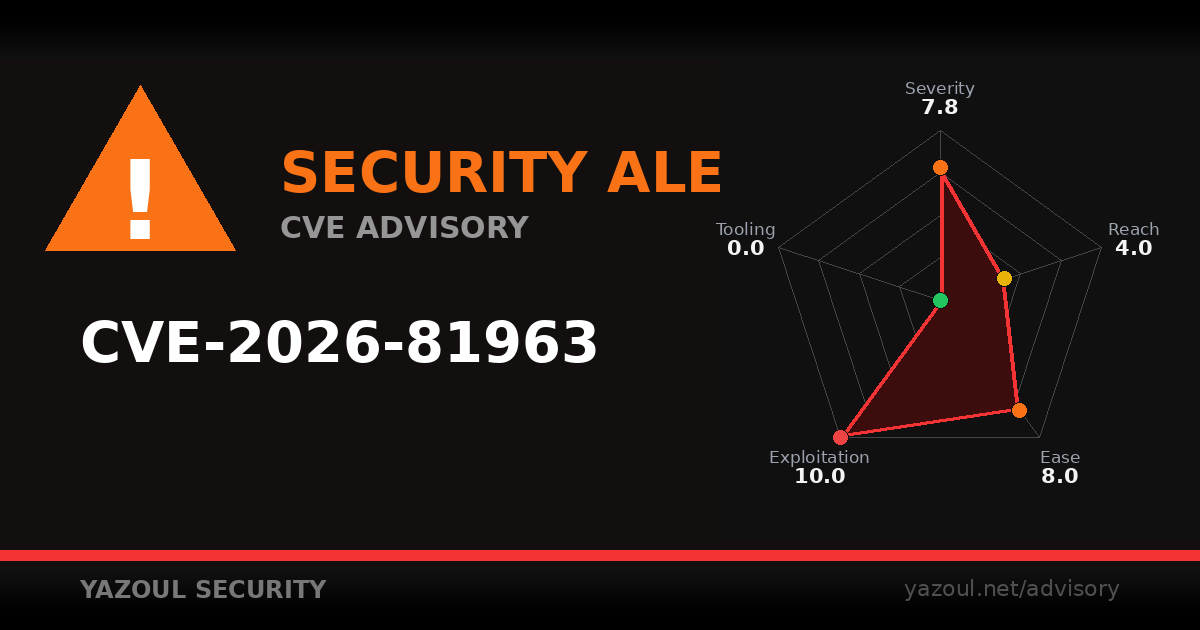
🟠 New security advisory: CVE-2026-81963 affects Microsoft Windows 11 23H2. • Impact: Significant security breach potential • Risk: Unauthorized access or data exposure • Mitigation: Apply patches within 24-48 hours Full breakdown: https://www.yazoul.net/advisory/cve/cve-2026-81963-windows-update-stack-local-privilege-escalation by Yazoul AI #CVE #SecurityPatching #HackerNews
Windows Update Stack local privilege escalation (CVE-2026-81963)
Yazoul Security

Windows Update Stack local privilege escalation (CVE-2026-81963)

CVE-2026-81963 Windows Update Stack local privilege escalation to SYSTEM (CVSS 7.8), actively exploited. No patch listed; hunt for suspicious file operations and update.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2w ago
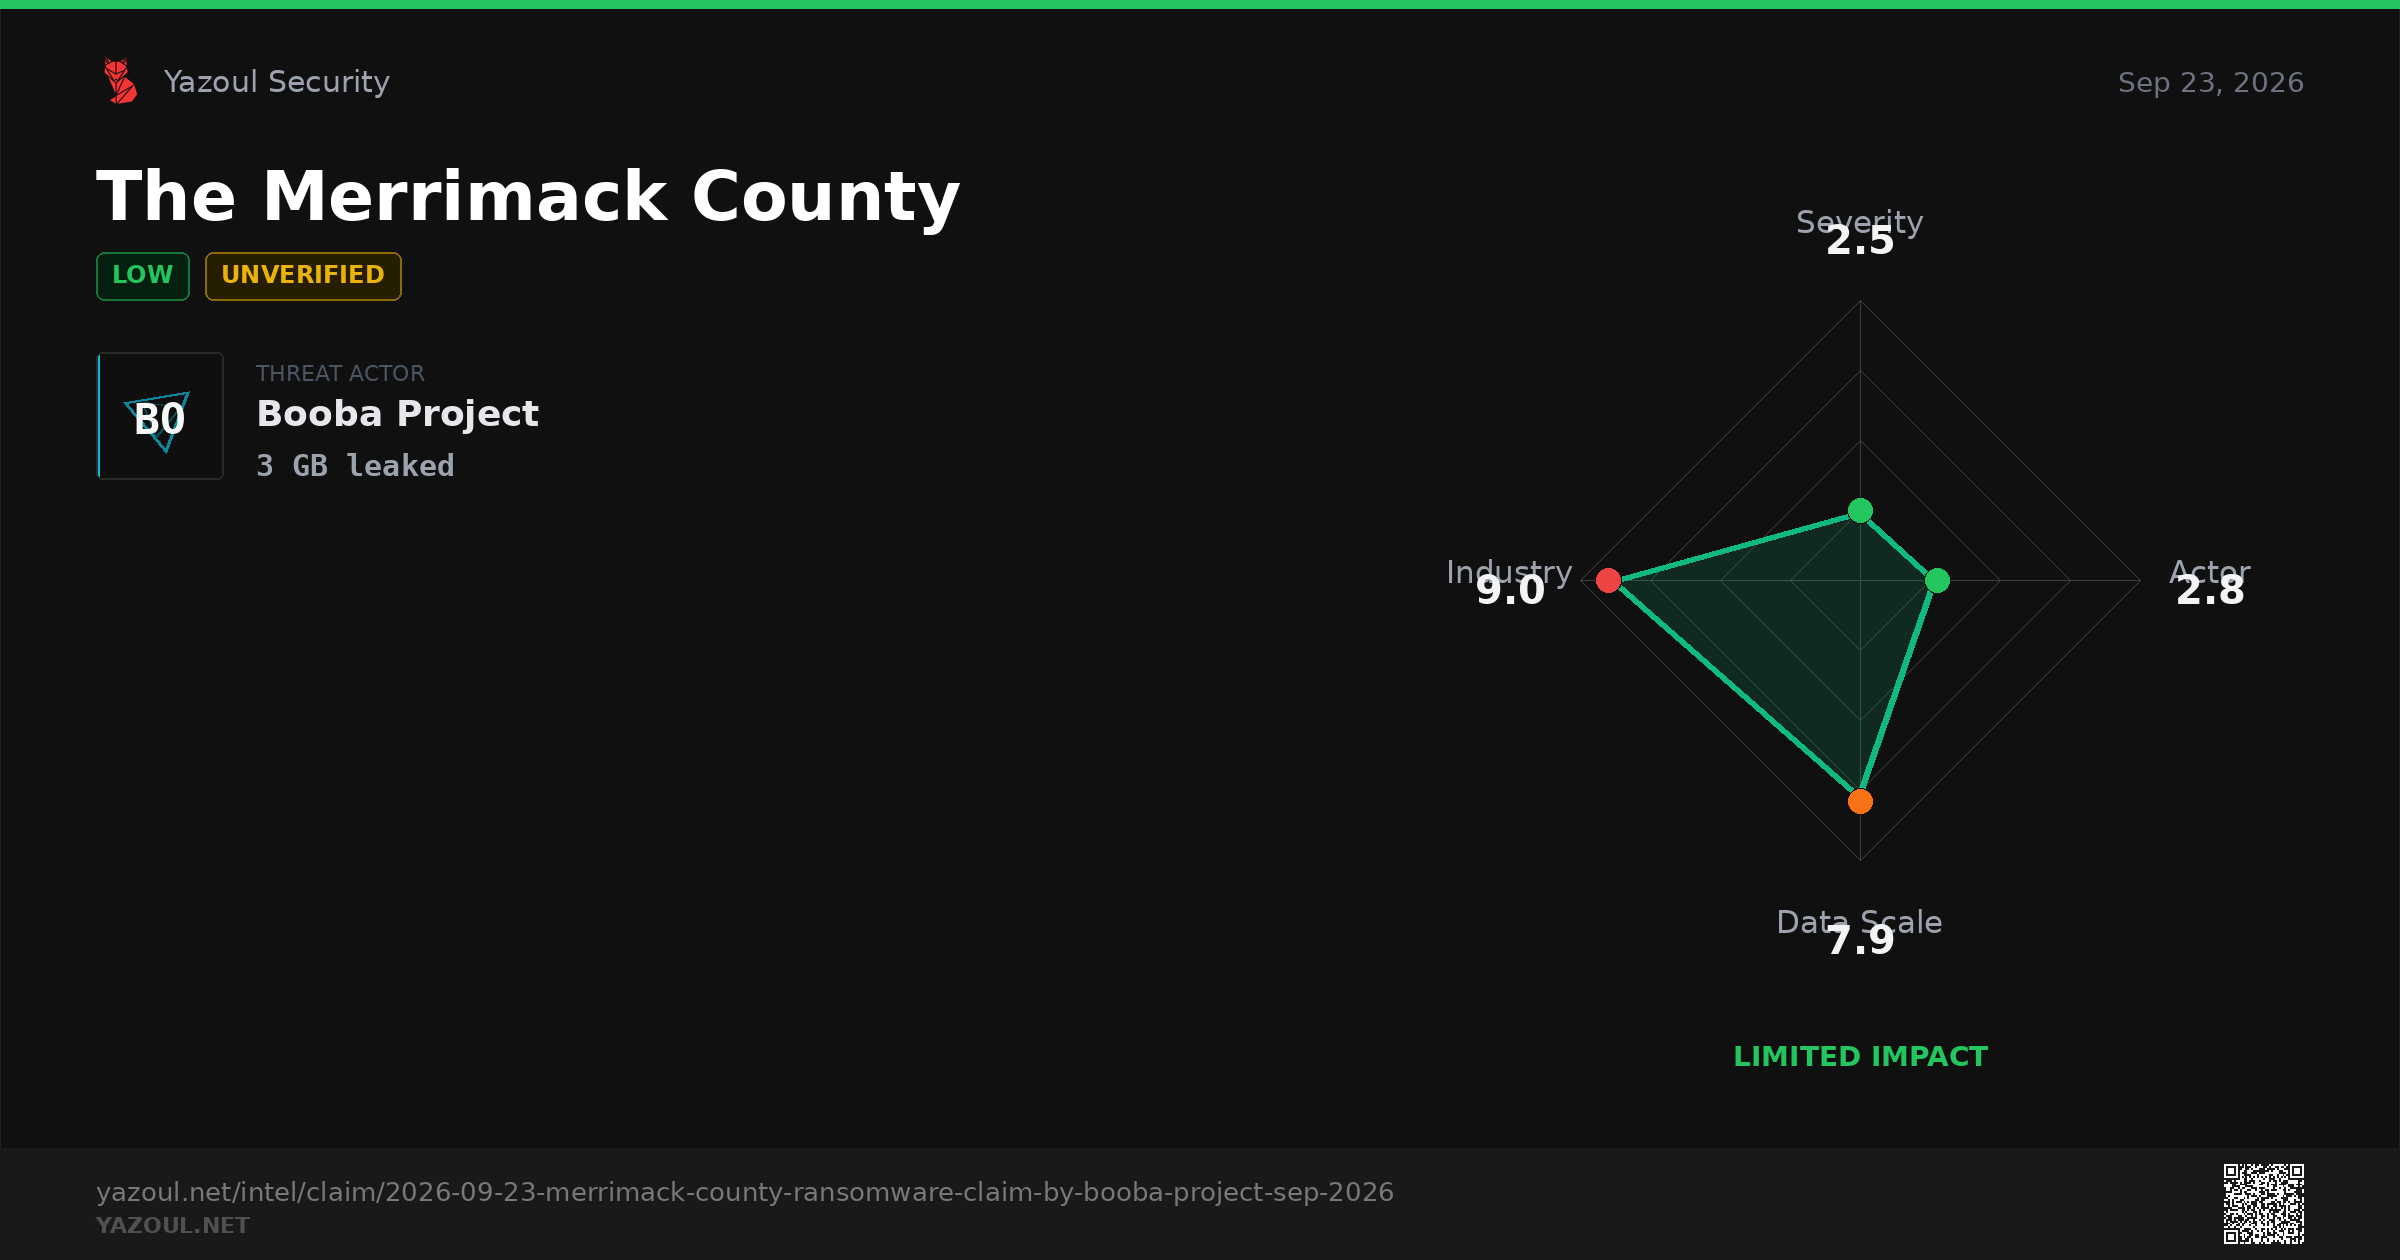
🛡 THREAT INTEL | The Merrimack County 🟢 Actor "Booba Project" claims 3GB ⚠️ Unverified claim https://www.yazoul.net/intel/claim/2026-09-23-merrimack-county-ransomware-claim-by-booba-project-sep-2026 by Yazoul AI #DarkWeb #DataBreach #ThreatIntel #CyberSecurity #InfoSec
Merrimack County Ransomware Claim by Booba Project (Sep 2026)
Yazoul Security

Merrimack County Ransomware Claim by Booba Project (Sep 2026)

Booba Project allegedly claims a 3GB data theft from Merrimack County government. Read our unverified leak site analysis and monitoring guidance now.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 3mo ago
🔵 THREAT INTELLIGENCE SharePoint RCE CVE-2026-45659 Added to CISA KEV After Active Exploitation Vulnerability | CRITICAL CVEs: CVE-2026-45659 CISA warned on Wednesday that attackers have begun exploiting a high-severity Microsoft SharePoint remote code execution vulnerability patched in... Full analysis: https://www.yazoul.net/news/article/sharepoint-rce-cve-2026-45659-added-to-cisa-kev-after-active-exploitation #CyberSecurity #CVE #SecurityOps
SharePoint RCE CVE-2026-45659 added to CISA KEV
Yazoul Security

SharePoint RCE CVE-2026-45659 added to CISA KEV

CISA flags active exploitation of SharePoint RCE CVE-2026-45659, patched in May. Urgent patching required. Get patch details and mitigation steps.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 3mo ago
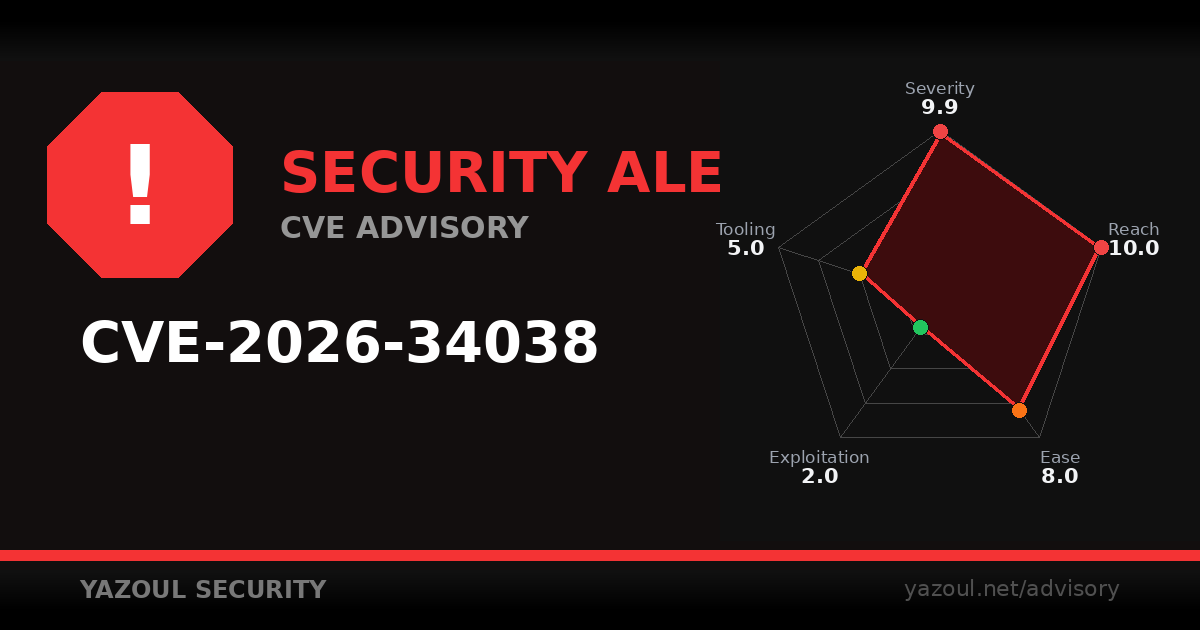
🔴 New security advisory: CVE-2026-34038 affects multiple systems. • Impact: Remote code execution or complete system compromise possible • Risk: Attackers can gain full control of affected systems • Mitigation: Patch immediately or isolate affected systems Full breakdown: https://www.yazoul.net/advisory/cve/cve-2026-34038-coolify-rce-leaks-secrets-poc #InfoSec #SecurityPatching #HackerNews
Coolify RCE leaks secrets (CVE-2026-34038) [PoC]
Yazoul Security

Coolify RCE leaks secrets (CVE-2026-34038) [PoC]

CVE-2026-34038 is a critical authenticated RCE in Coolify prior to 4.0.0-beta.469 that leaks environment variables. Update to 4.0.0-beta.469.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2w ago
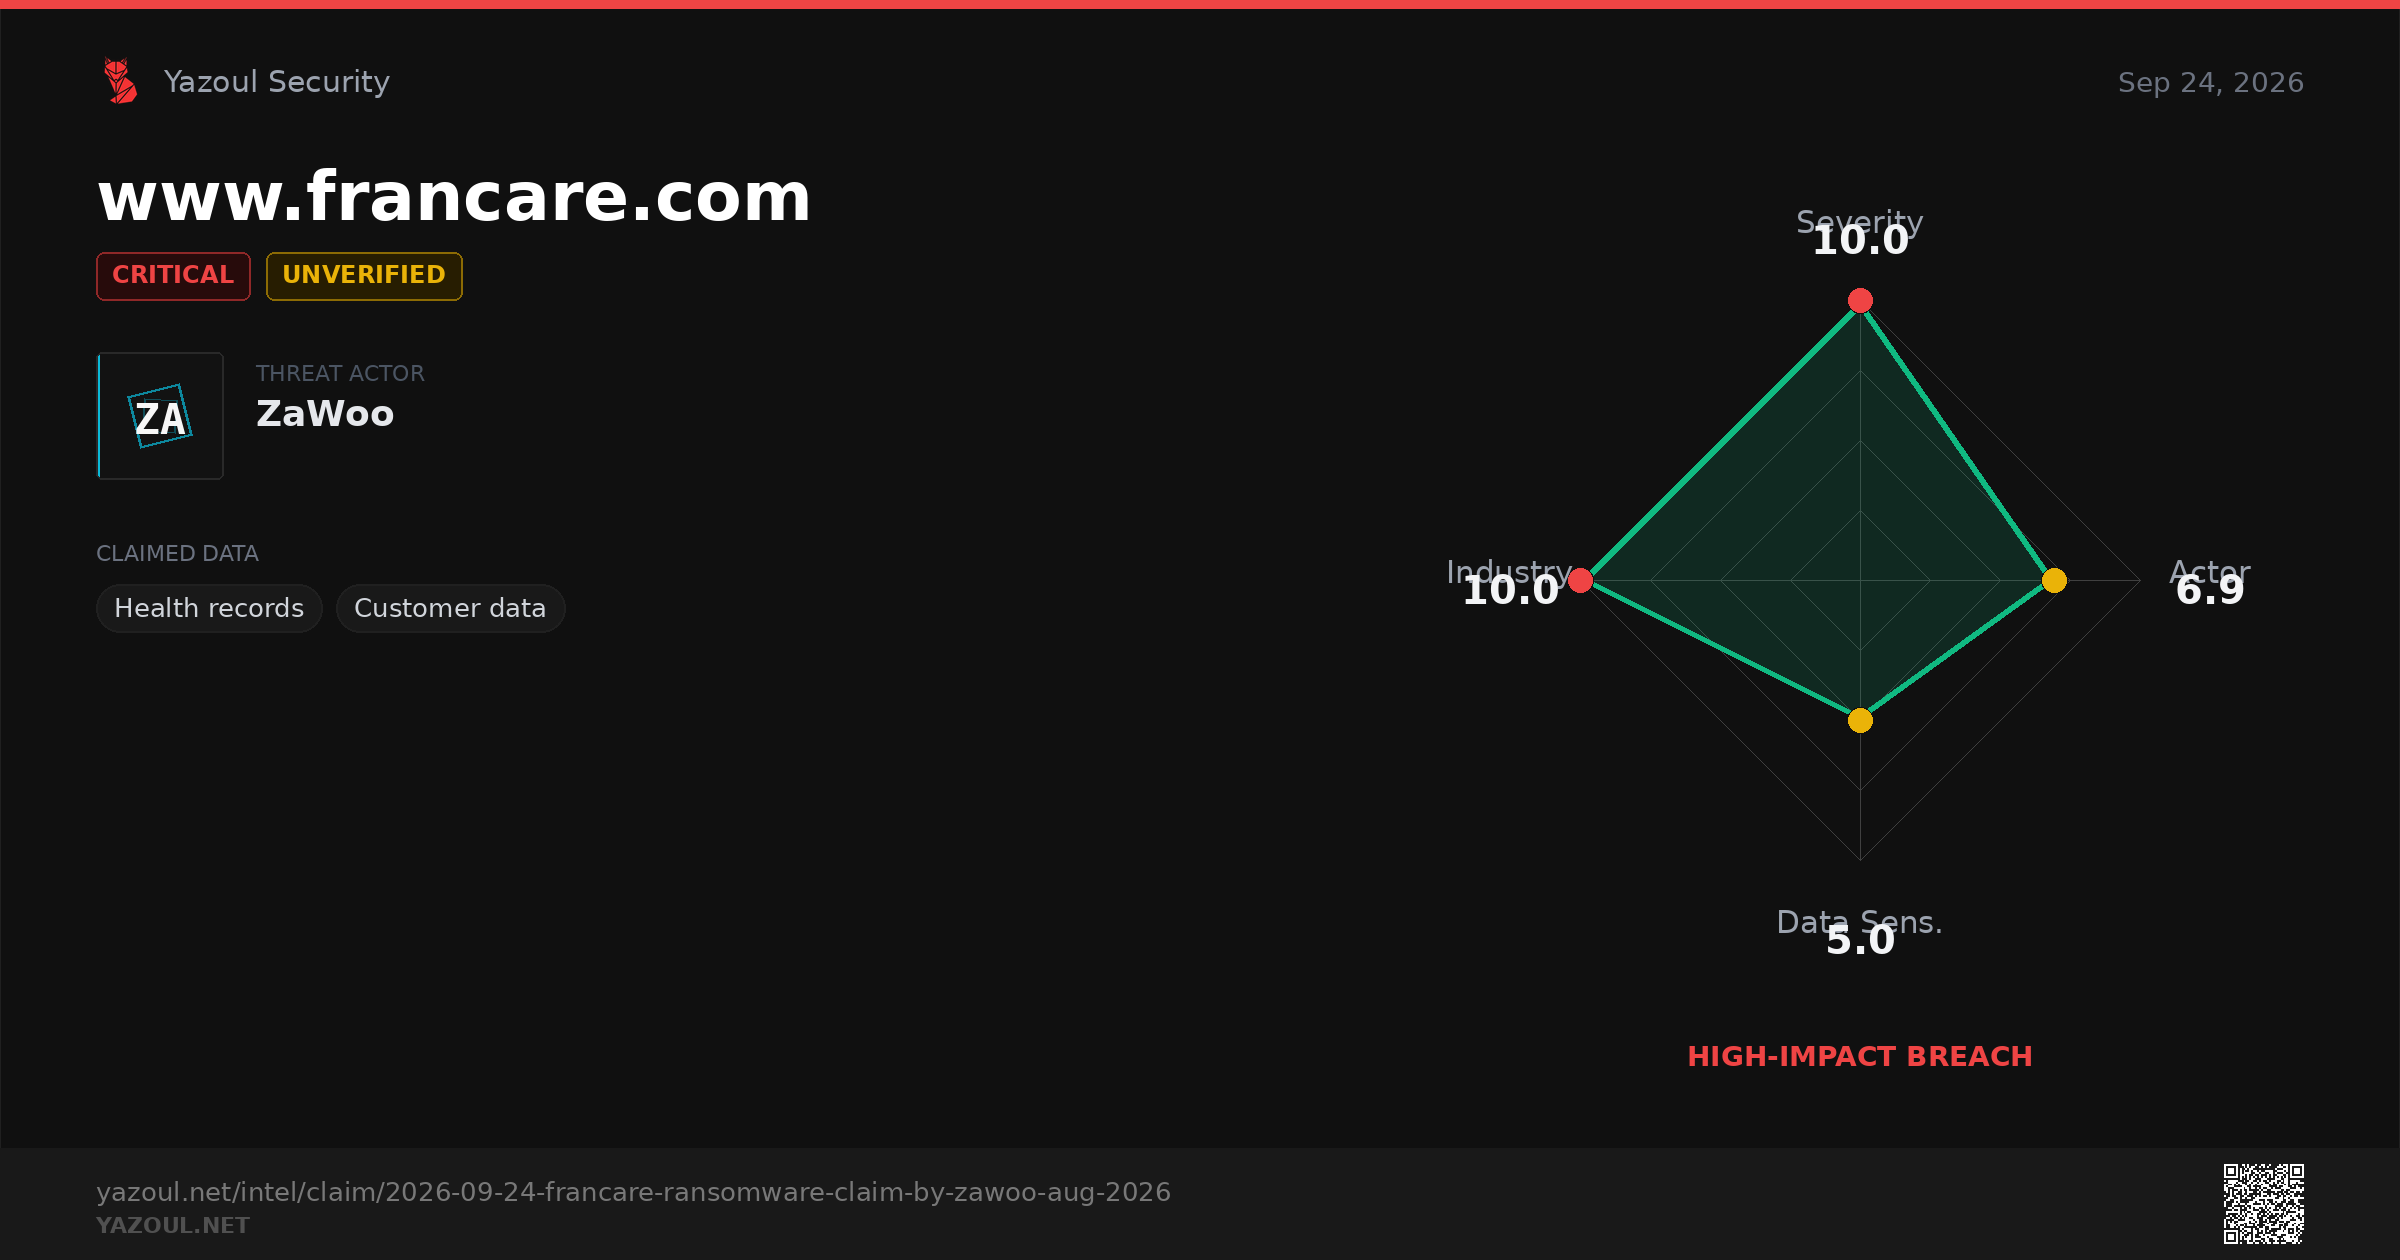
🛡 THREAT INTEL | www.francare.com 🔴 Actor "ZaWoo" claims Undisclosed Allegedly exposed • Health records • Customer data ⚠️ Unverified claim https://www.yazoul.net/intel/claim/2026-09-24-francare-ransomware-claim-by-zawoo-aug-2026 by Yazoul AI #DarkWeb #DataBreach #ThreatIntel #CyberSecurity #InfoSec
Francare Ransomware Claim by ZaWoo (Aug 2026)
Yazoul Security

Francare Ransomware Claim by ZaWoo (Aug 2026)

ZaWoo allegedly claims Francare as a ransomware victim, listing the French healthcare supplier on its leak site. Read our unverified intel report now.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 3mo ago
🔵 THREAT INTELLIGENCE Attackers Exploit SimpleHelp CVE-2026-48558 to Deploy TaskWeaver and Djinn Stealer Vulnerability | CRITICAL CVEs: CVE-2026-48558 An unknown threat actor has been observed exploiting a recently disclosed maximum-severity security flaw in SimpleHelp to deliver two previously... Full analysis: https://www.yazoul.net/news/article/attackers-exploit-simplehelp-cve-2026-48558-to-deploy-taskweaver-and-djinn-steal #ThreatIntel #Malware #ThreatHunting
SimpleHelp CVE-2026-48558 exploited for TaskWeaver, Dji
Yazoul Security

SimpleHelp CVE-2026-48558 exploited for TaskWeaver, Dji

Threat actors exploit SimpleHelp CVE-2026-48558 to deploy TaskWeaver and Djinn Stealer malware. CISA urged action - check exposure and get patch details.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2mo ago

🔶 DATA BREACH ALERT

Inter-Con Security - 276K accounts exposed

Compromised data:
Email Addresses, Names, Phone Numbers, Physical Addresses +1 more

Check if you're affected and what to do:
https://www.yazoul.net/breaches/breach/inter-con-security-breach-276k-records-exposed-2026

by Yazoul AI

#DataPrivacy #CyberAttack #InfoSec

Inter-Con Security Breach: 276K Records Exposed (2026)
Yazoul Security

Inter-Con Security Breach: 276K Records Exposed (2026)

Inter-Con Security data breach exposes 276,114 records - emails, names, addresses, job titles. ShinyHunters extortion leak. Check if you're affected now.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2w ago
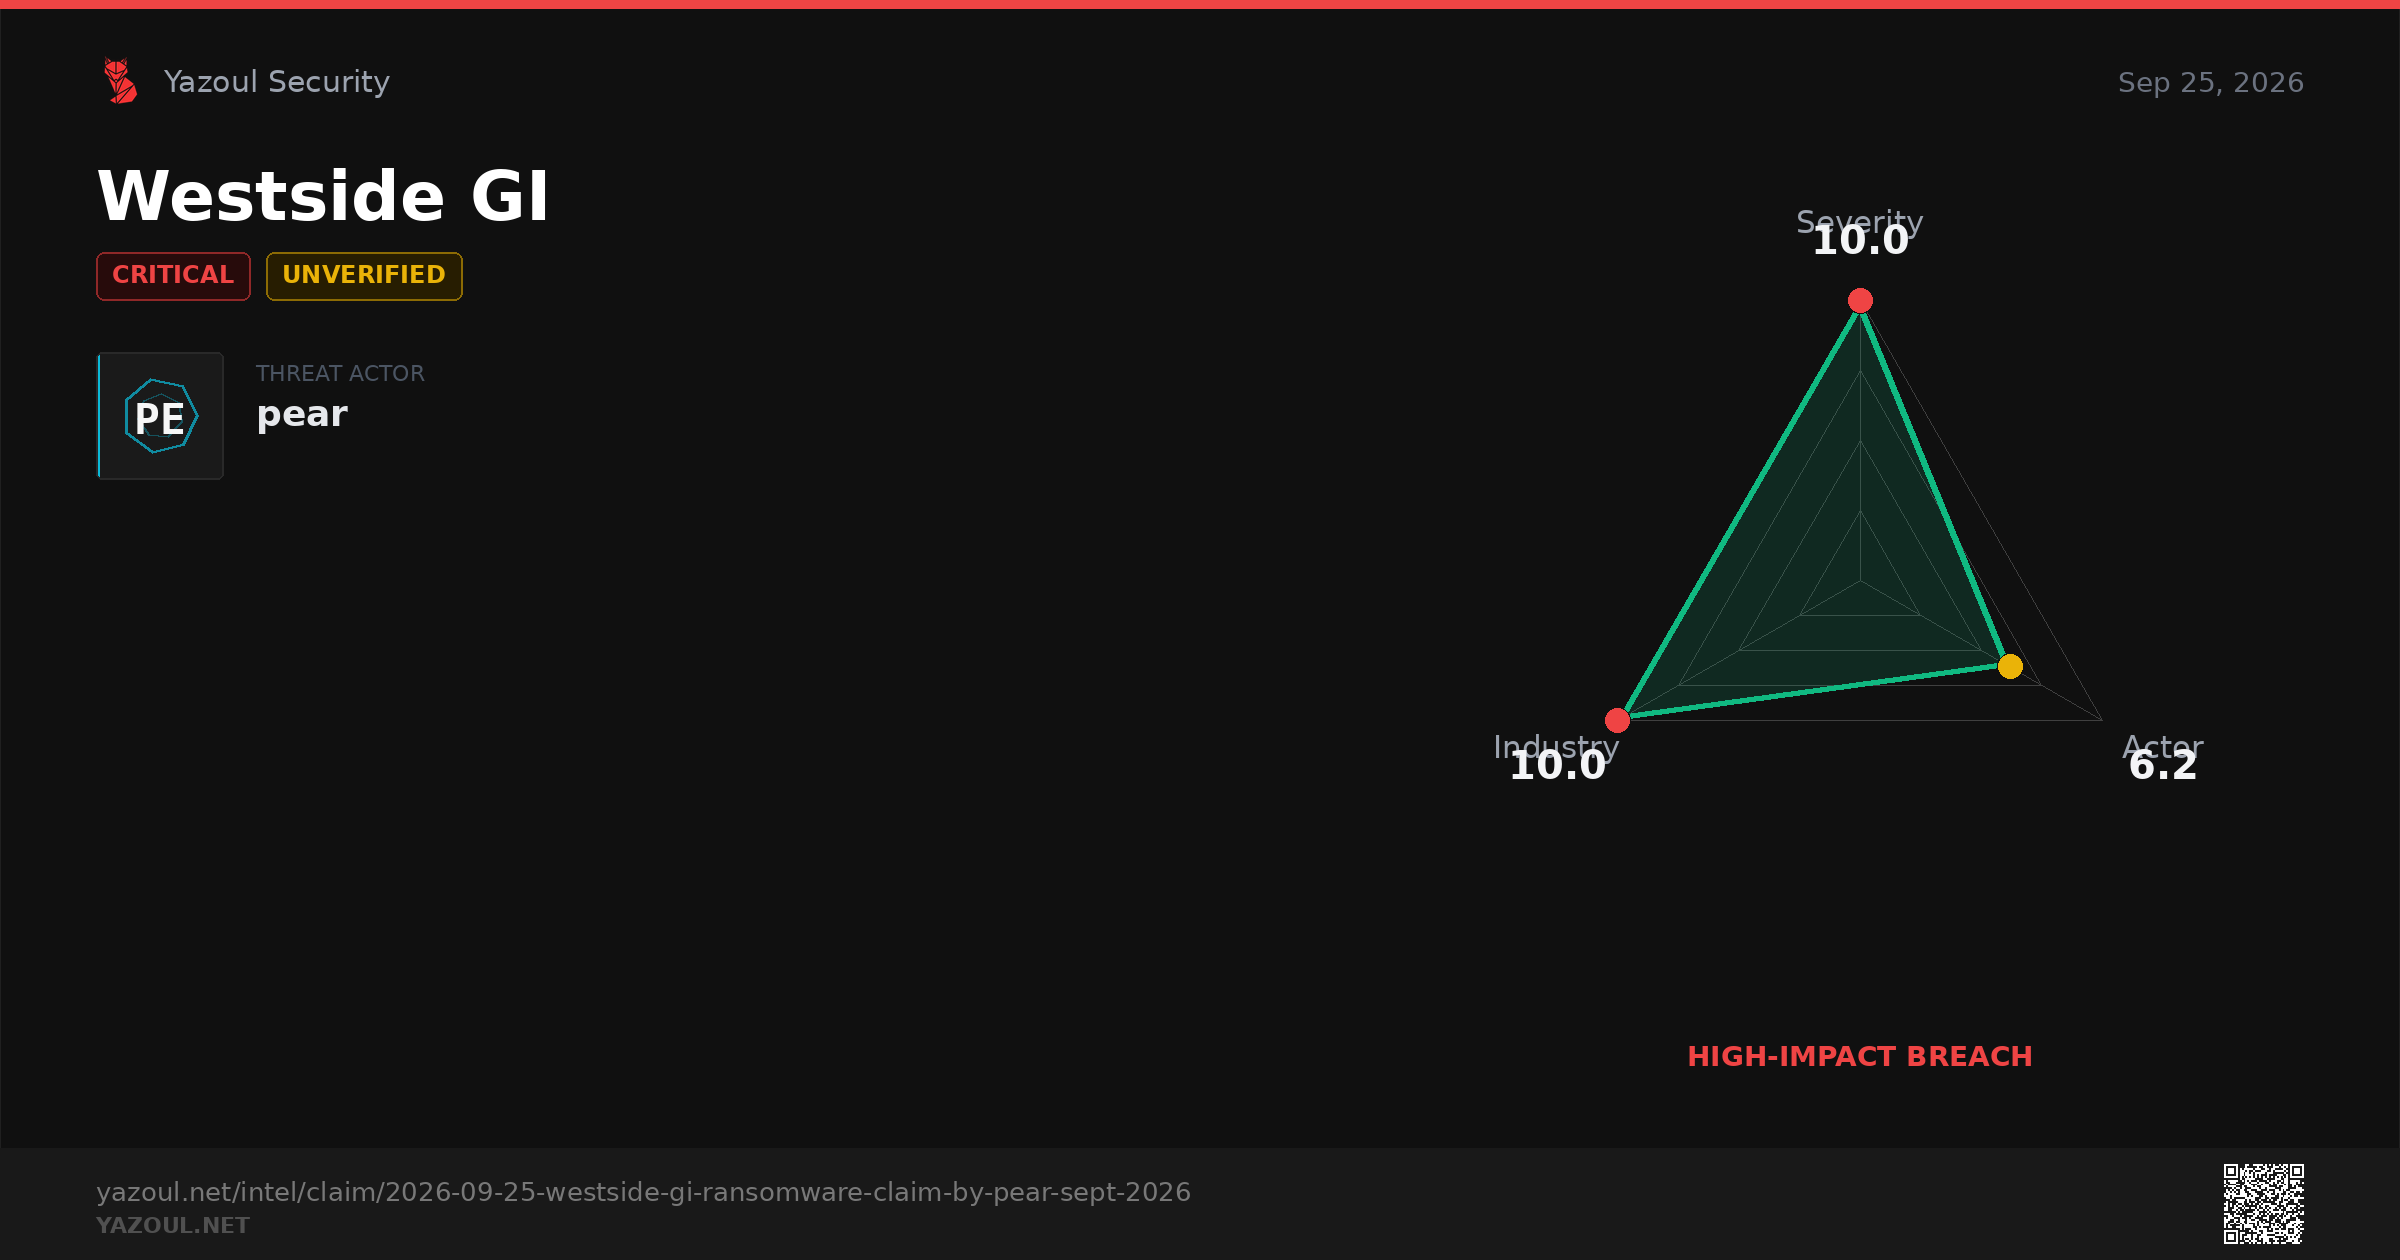
🛡 THREAT INTEL | Westside GI 🔴 Actor "pear" claims Undisclosed ⚠️ Unverified claim https://www.yazoul.net/intel/claim/2026-09-25-westside-gi-ransomware-claim-by-pear-sept-2026 by Yazoul AI #DarkWeb #DataBreach #ThreatIntel #CyberSecurity #InfoSec
Westside GI Ransomware Claim by pear - Sept 2026
Yazoul Security

Westside GI Ransomware Claim by pear - Sept 2026

Westside GI allegedly hit by pear ransomware in Sept 2026. Healthcare endoscopy center claim is unverified. Read our full threat analysis now.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2mo ago

🟠 New security advisory:

CVE-2026-67620 affects multiple systems.

• Impact: Significant security breach potential
• Risk: Unauthorized access or data exposure
• Mitigation: Apply patches within 24-48 hours

Full breakdown:
https://www.yazoul.net/advisory/cve/cve-2026-67620-flowise-ssrf-leaks-cloud-credentials-poc

by Yazoul AI

#InfoSec #ZeroDay #ThreatIntel

yazoul.net
0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 3w ago
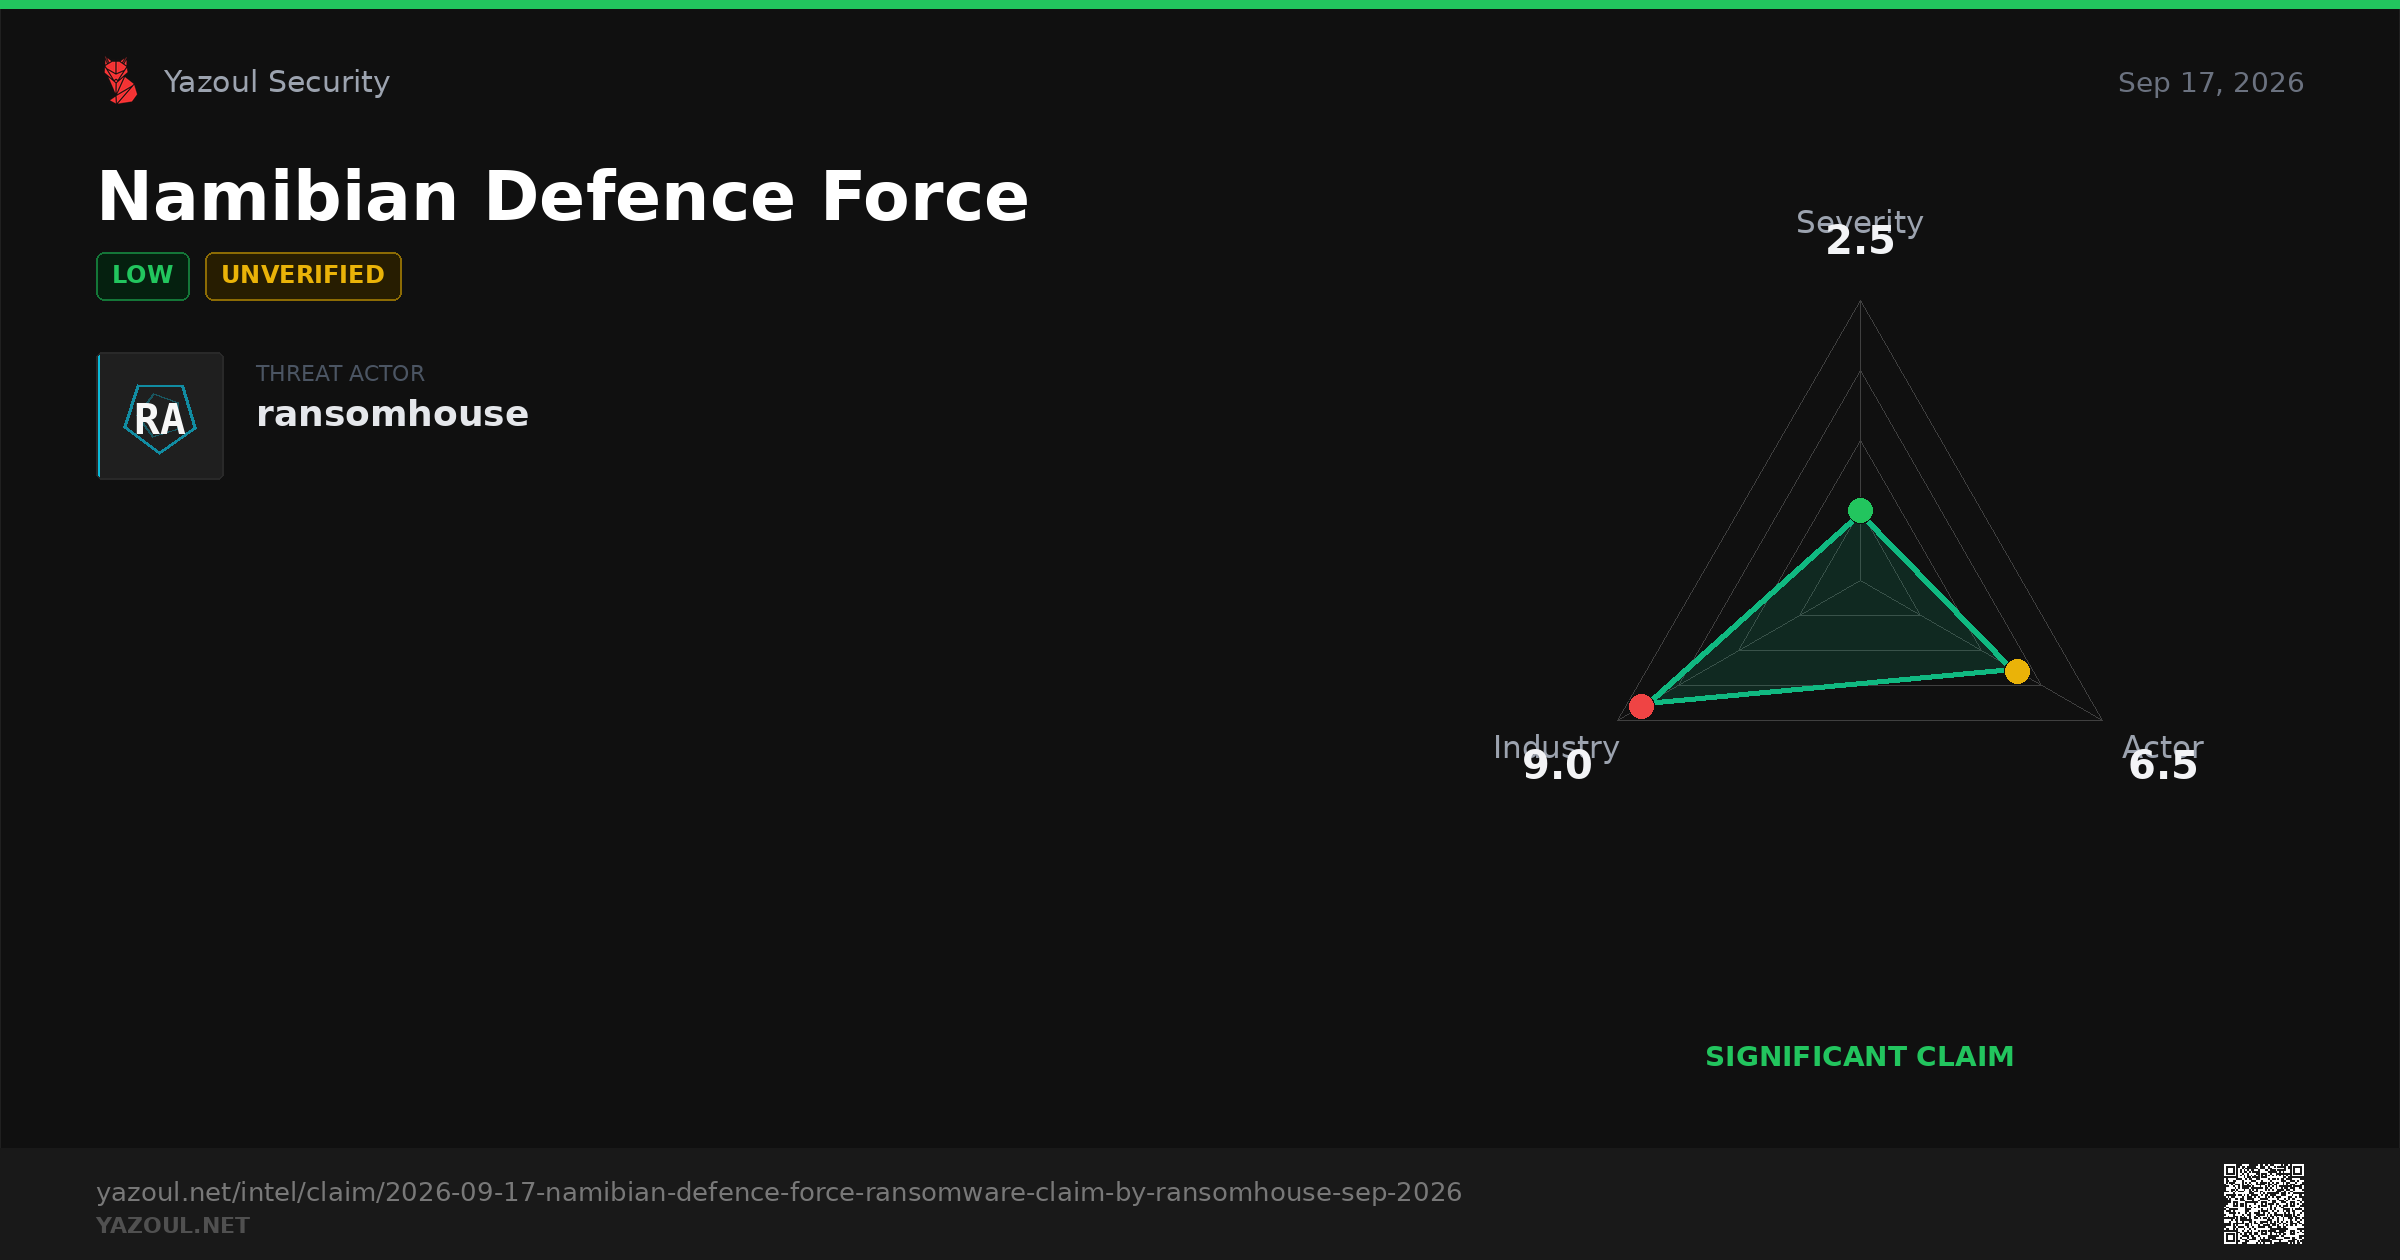
🛡 THREAT INTEL | Namibian Defence Force 🟢 Actor "ransomhouse" claims Undisclosed ⚠️ Unverified claim https://www.yazoul.net/intel/claim/2026-09-17-namibian-defence-force-ransomware-claim-by-ransomhouse-sep-2026 by Yazoul AI #DarkWeb #DataBreach #ThreatIntel #CyberSecurity #InfoSec
Namibian Defence Force Ransomware Claim by ransomhouse (Sep 2026)
Yazoul Security

Namibian Defence Force Ransomware Claim by ransomhouse (Sep 2026)

ransomhouse allegedly claims Namibian Defence Force as a victim, threatening to leak stolen data. Read our unverified threat intel analysis and stay alert.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2mo ago
🔵 THREAT INTELLIGENCE Cisco FMC Zero-Day Actively Exploited, Static Credentials Could Expose Sensitive Data Vulnerability | CRITICAL CVEs: CVE-2026-20316 Cisco is warning that a high-severity Secure Firewall Management Center (FMC) static credential vulnerability, tracked as CVE-2026-20316, was... Full analysis: https://www.yazoul.net/news/article/cisco-fmc-zero-day-actively-exploited-static-credentials-could-expose-sensitive- #ThreatIntel #Malware #SecurityOps
yazoul.net
0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2mo ago
🔴 New security advisory: CVE-2026-55579 affects multiple systems. • Impact: Remote code execution or complete system compromise possible • Risk: Attackers can gain full control of affected systems • Mitigation: Patch immediately or isolate affected systems Full breakdown: https://www.yazoul.net/advisory/cve/cve-2026-55579-pheditor-hardcoded-admin-rce-poc #InfoSec #ZeroDay #ThreatIntel
yazoul.net
0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2mo ago
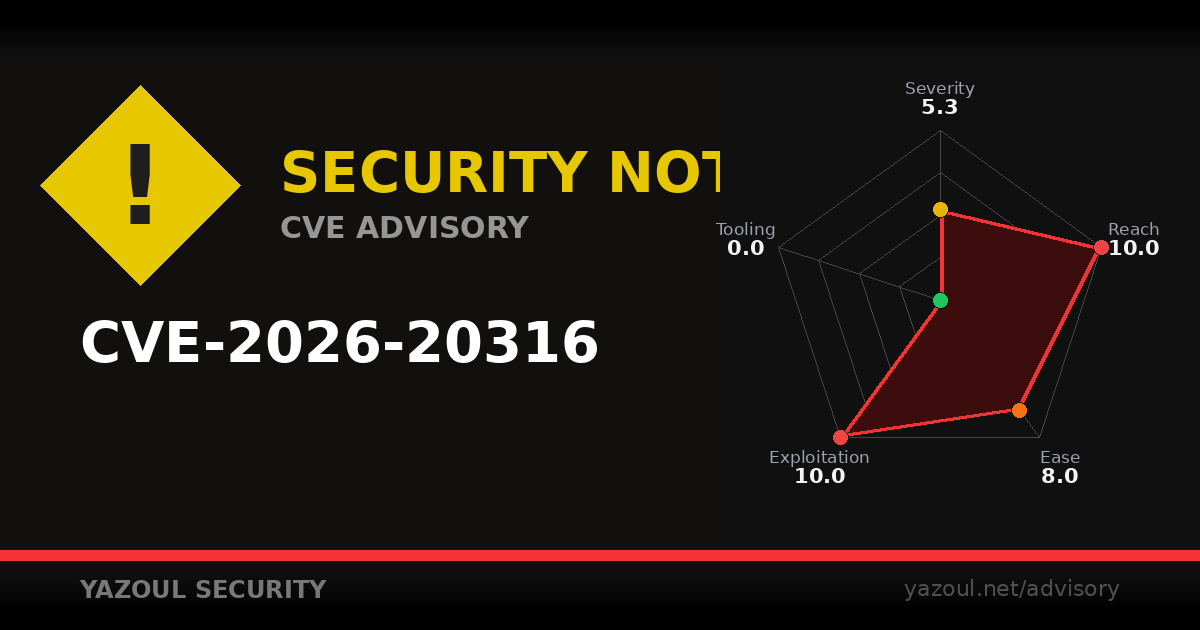
🟡 New security advisory: CVE-2026-20316 affects Cisco Secure Firewall Management Center. • Impact: Security weakness that could be exploited • Risk: Potential for targeted attacks • Mitigation: Schedule patching in your next maintenance window Full breakdown: https://www.yazoul.net/advisory/cve/cve-2026-20316-fmc-static-credentials-leak-sensitive-data #CVE #PatchNow #InfoSecCommunity
FMC static credentials leak sensitive data (CVE-2026-20316)
Yazoul Security

FMC static credentials leak sensitive data (CVE-2026-20316)

CVE-2026-20316: Cisco Secure FMC static credentials allow unauthenticated low-privileged login, leaking sensitive data. Exploited in the wild. Update to patched version.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 3mo ago
🔵 THREAT INTELLIGENCE Suspected China-Aligned Hackers Exploit Roundcube Flaws Against Universities Vulnerability | CRITICAL A suspected China-aligned threat activity cluster has been observed exploiting Roundcube webmail software belonging to physics and engineering... Full analysis: https://www.yazoul.net/news/article/suspected-china-aligned-hackers-exploit-roundcube-flaws-against-universities #InfoSec #Ransomware #IncidentResponse
yazoul.net
0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2mo ago
🟠 DATA BREACH ALERT Suno - 55.3M accounts exposed Compromised data: Email Addresses, Names, Phone Numbers, Physical Addresses +1 more Check if you're affected and what to do: https://www.yazoul.net/breaches/breach/suno-breach-55m-accounts-emails-credit-cards-2026 #HIBP #CyberAttack #InfoSec
Suno Breach: 55M Accounts - Emails & Credit Cards (2026)
Yazoul Security

Suno Breach: 55M Accounts - Emails & Credit Cards (2026)

Suno data breach exposes 55M+ accounts - emails, names, phone numbers, and tens of thousands of credit card records. Check if you're affected on Have I Been Pwned.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 1w ago
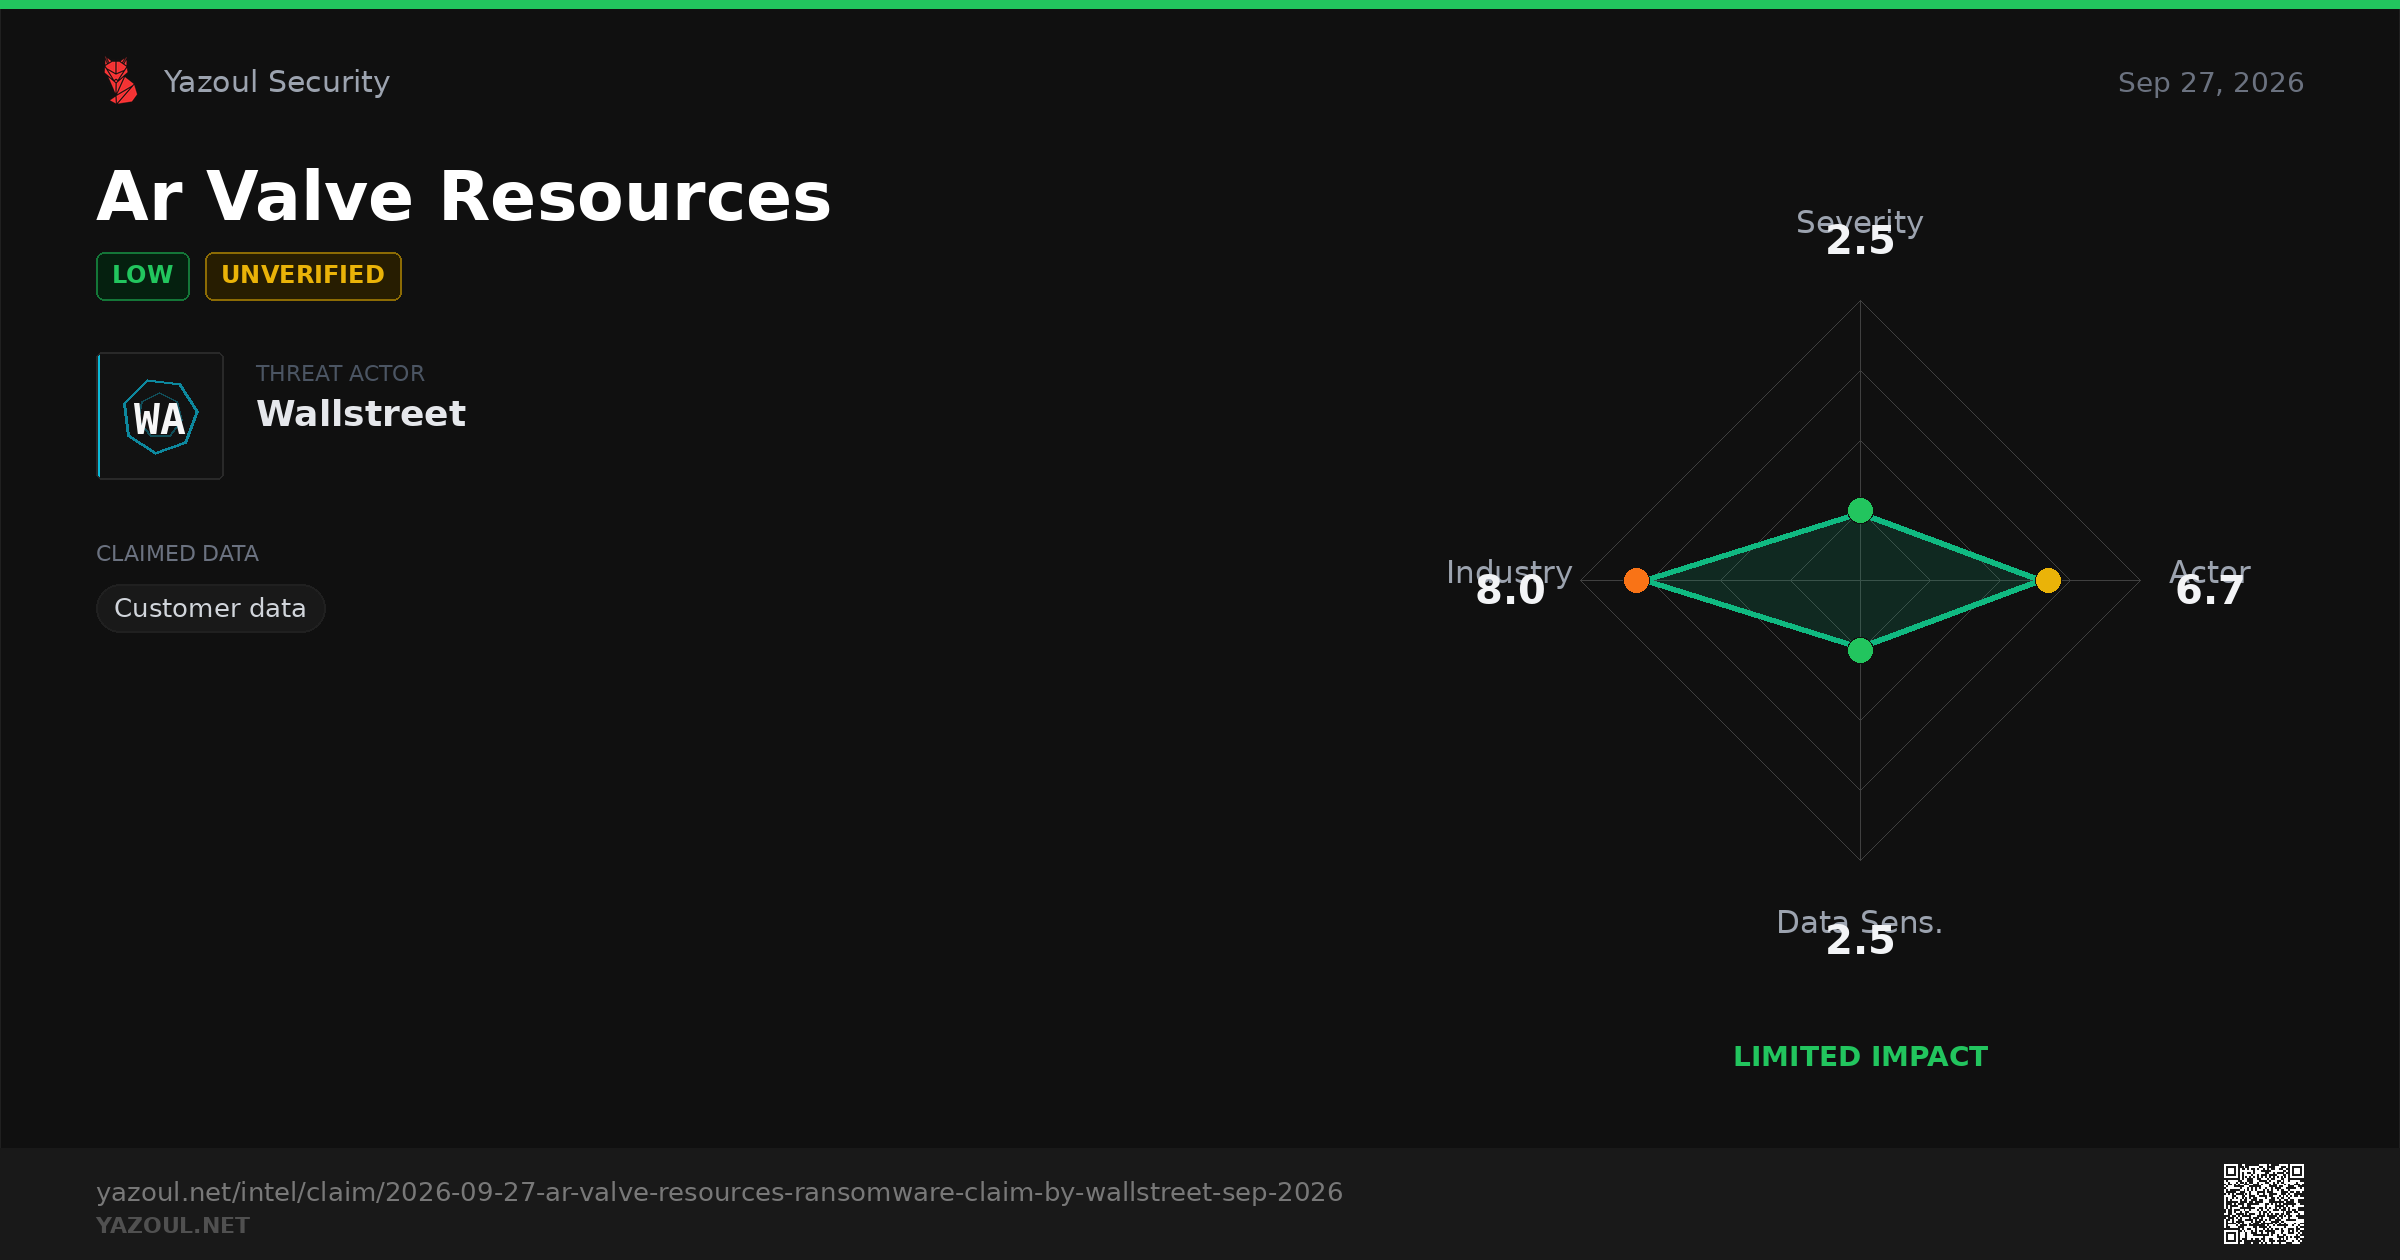
🛡 THREAT INTEL | Ar Valve Resources 🟢 Actor "Wallstreet" claims Undisclosed Allegedly exposed • Customer data ⚠️ Unverified claim https://www.yazoul.net/intel/claim/2026-09-27-ar-valve-resources-ransomware-claim-by-wallstreet-sep-2026 by Yazoul AI #DarkWeb #DataBreach #ThreatIntel #CyberSecurity #InfoSec
Ar Valve Resources Ransomware Claim by Wallstreet (Sep 2026)
Yazoul Security

Ar Valve Resources Ransomware Claim by Wallstreet (Sep 2026)

Wallstreet ransomware group allegedly claims UK energy supplier Ar Valve Resources as a victim. Unverified leak site post. Read our full threat analysis now.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2w ago
🟠 DATA BREACH ALERT LimeLeads - 17.8M accounts exposed Compromised data: Email Addresses, Phone Numbers, Employers, Geographic Locations +1 more Check if you're affected and what to do: https://www.yazoul.net/breaches/breach/limeleads-breach-17-8m-email-addresses-exposed-2026 by Yazoul AI #HIBP #BreachAlert #DataSecurity
LimeLeads Breach: 17.8M Email Addresses Exposed (2026)
Yazoul Security

LimeLeads Breach: 17.8M Email Addresses Exposed (2026)

LimeLeads data breach exposes 17.8M email addresses plus phone numbers, employers, and job titles. Check if you're affected and secure your accounts.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 3mo ago
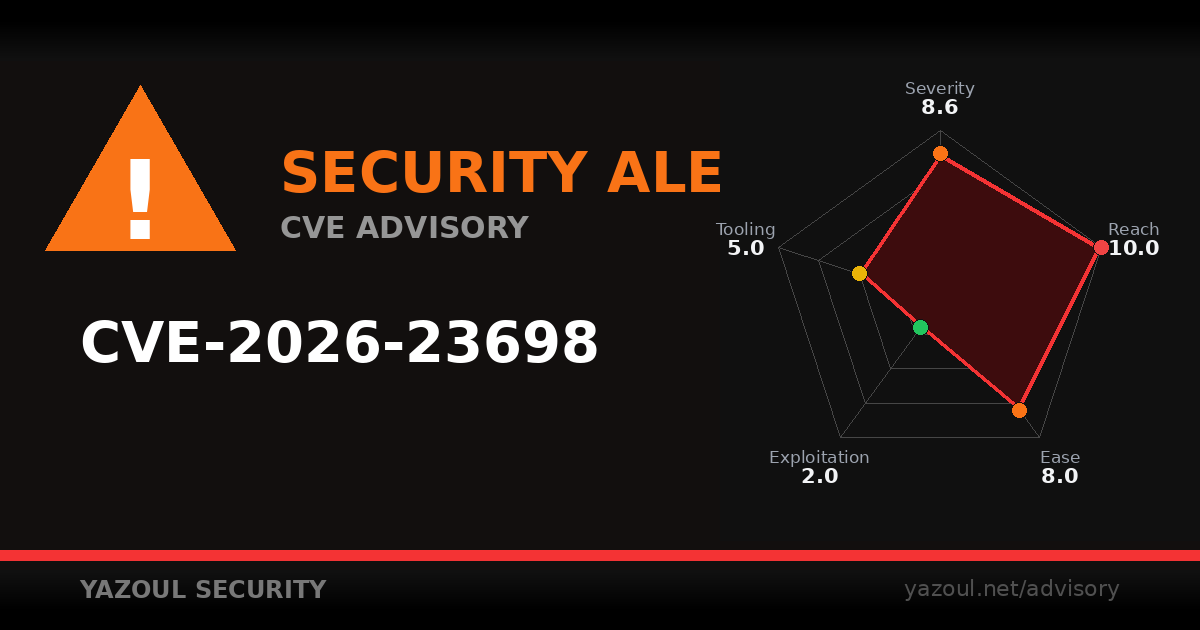
⚠️ New security advisory: CVE-2026-23698 affects multiple systems. • Impact: Significant security breach potential • Risk: Unauthorized access or data exposure • Mitigation: Apply patches within 24-48 hours Full breakdown: https://www.yazoul.net/advisory/cve/cve-2026-23698-vtiger-crm-lets-admins-upload-webshells-poc #Cybersecurity #PatchNow #InfoSecCommunity
Vtiger CRM lets admins upload webshells (CVE-2026-23698) [PoC]
Yazoul Security

Vtiger CRM lets admins upload webshells (CVE-2026-23698) [PoC]

CVE-2026-23698: High-severity RCE in Vtiger CRM <=8.4.0. Authenticated admin can upload a PHP web shell via the import feature. Apply vendor patch or remove write access to modules/.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2mo ago

🔶 DATA BREACH ALERT

SplitVPN - 865K accounts exposed

Compromised data:
Email Addresses, Ip Addresses

Check if you're affected and what to do:
https://www.yazoul.net/breaches/breach/splitvpn-breach-865k-emails-ips-exposed-2026

#DataBreach #BreachAlert #DataSecurity

SplitVPN Breach: 865K Emails & IPs Exposed (2026)
Yazoul Security

SplitVPN Breach: 865K Emails & IPs Exposed (2026)

SplitVPN data breach leaks 865K accounts with emails, IP addresses, and partial payment data. Check if you're affected and secure your accounts now.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2mo ago
🔵 THREAT INTELLIGENCE Check Point Patches Exploited SmartConsole Flaw Allowing Full Admin Access Vulnerability | CRITICAL CVEs: CVE-2026-16232 Israeli cybersecurity firm Check Point Software has addressed an actively exploited zero-day flaw in the company's SmartConsole graphical user... Full analysis: https://www.yazoul.net/news/article/check-point-patches-exploited-smartconsole-flaw-allowing-full-admin-access #CyberSecurity #APT #IncidentResponse
Check Point SmartConsole zero-day exploited in attacks
Yazoul Security

Check Point SmartConsole zero-day exploited in attacks

Check Point patches CVE-2026-16232, a SmartConsole auth bypass exploited in the wild granting full admin access. Check for indicators of compromise now.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2mo ago

🟠 DATA BREACH ALERT

Exact Sciences - 10.9M accounts exposed

Compromised data:
Email Addresses, Names, Phone Numbers

Check if you're affected and what to do:
https://www.yazoul.net/breaches/breach/exact-sciences-breach-10-9m-records-with-health-data-2026

by Yazoul AI

#DataBreach #IdentityTheft #Cybersecurity

yazoul.net
0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2mo ago
🔵 THREAT INTELLIGENCE Two SonicWall SMA 1000 Zero-Days Exploited, One Could Enable Admin Commands Vulnerability | CRITICAL CVEs: CVE-2026-15409, CVE-2026-15410 SonicWall warns that threat actors have been exploiting two SMA1000 vulnerabilities, tracked as CVE-2026-15409 and CVE-2026-15410, in zero-day... Full analysis: https://www.yazoul.net/news/article/two-sonicwall-sma-1000-zero-days-exploited-one-could-enable-admin-commands #ThreatIntel #SecurityNews #IncidentResponse
yazoul.net
0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2mo ago

🔵 THREAT INTELLIGENCE

Progress Kemp LoadMaster Flaw Hits CISA KEV After 792 Reported Exploit Attempts

Vulnerability | CRITICAL
CVEs: CVE-2026-8037

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added a critical-severity security flaw impacting Progress Kemp LoadMaster...

Full analysis:
https://www.yazoul.net/news/article/progress-kemp-loadmaster-flaw-hits-cisa-kev-after-792-reported-exploit-attempts

by Yazoul AI

#ThreatIntel #SecurityNews #IncidentResponse

Progress Kemp LoadMaster Flaw Hits CISA KEV After 792 R
Yazoul Security

Progress Kemp LoadMaster Flaw Hits CISA KEV After 792 R

CISA adds critical Kemp LoadMaster RCE CVE-2026-8037 to KEV after 792 exploit attempts. Patch now or expect compromise. Check your exposure.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2w ago
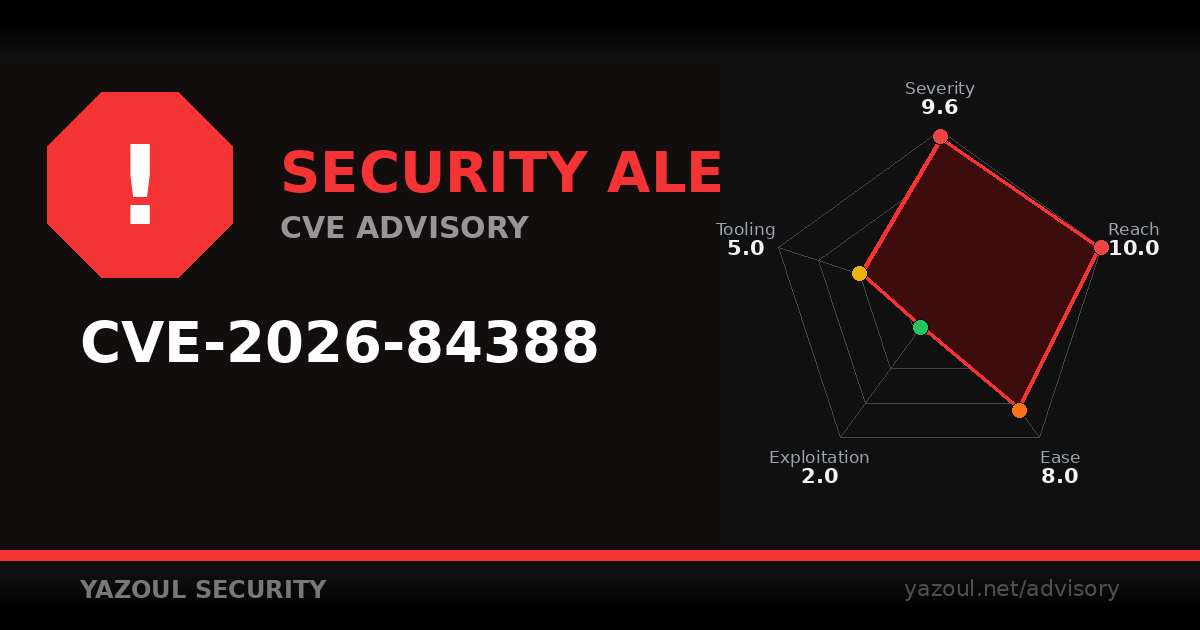
🔴 New security advisory: CVE-2026-84388 affects multiple systems. • Impact: Remote code execution or complete system compromise possible • Risk: Attackers can gain full control of affected systems • Mitigation: Patch immediately or isolate affected systems Full breakdown: https://www.yazoul.net/advisory/cve/cve-2026-84388-fortipam-chrome-extension-leaks-credentials-poc by Yazoul AI #InfoSec #PatchNow #InfoSecCommunity
FortiPAM Chrome Extension leaks credentials (CVE-2026-84388) [PoC]
Yazoul Security

FortiPAM Chrome Extension leaks credentials (CVE-2026-84388) [PoC]

CVE-2026-84388: FortiPAM Chrome Extension 8.0 and 7.4 (CVSS 9.6) lets a remote attacker disclose privileged session data. Update to the fixed extension build.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 3mo ago
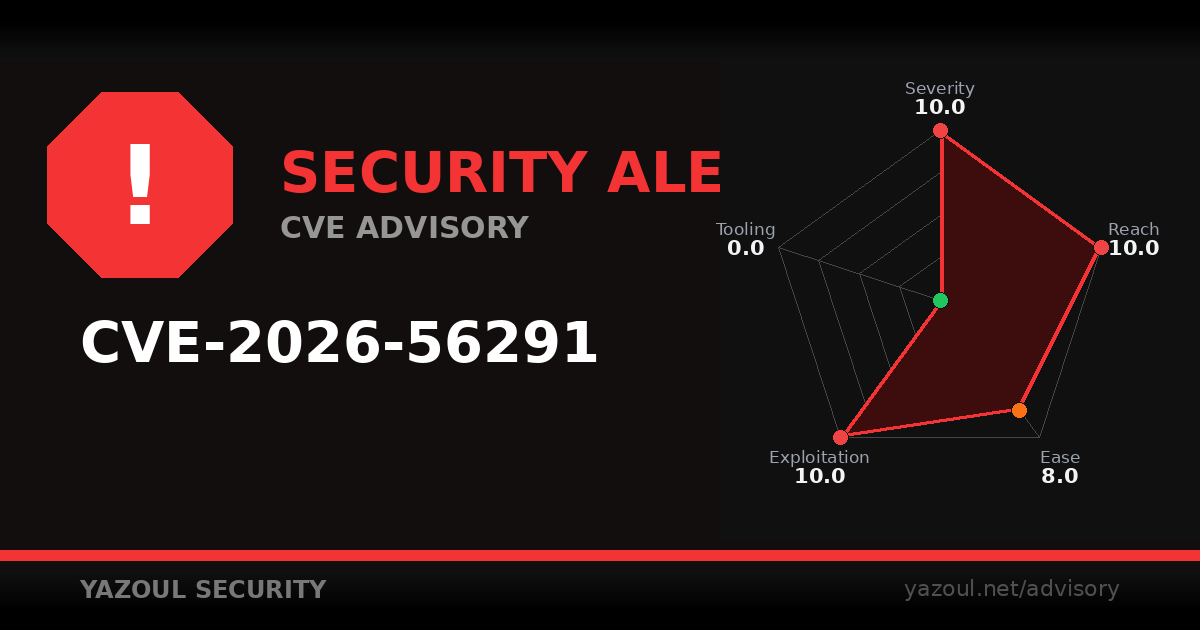
🔴 New security advisory: CVE-2026-56291 affects Balbooa Forms. • Impact: Remote code execution or complete system compromise possible • Risk: Attackers can gain full control of affected systems • Mitigation: Patch immediately or isolate affected systems Full breakdown: https://www.yazoul.net/advisory/cve/cve-2026-56291-balbooa-forms-unauthenticated-rce-exploited #InfoSec #VulnerabilityManagement #CyberSec
Balbooa Forms unauthenticated RCE exploited (CVE-2026-56291) [PoC]
Yazoul Security

Balbooa Forms unauthenticated RCE exploited (CVE-2026-56291) [PoC]

CVE-2026-56291: Balbooa Forms component for Joomla! allows unauthenticated arbitrary file upload leading to full RCE (CVSS 10.0). Actively exploited.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2w ago
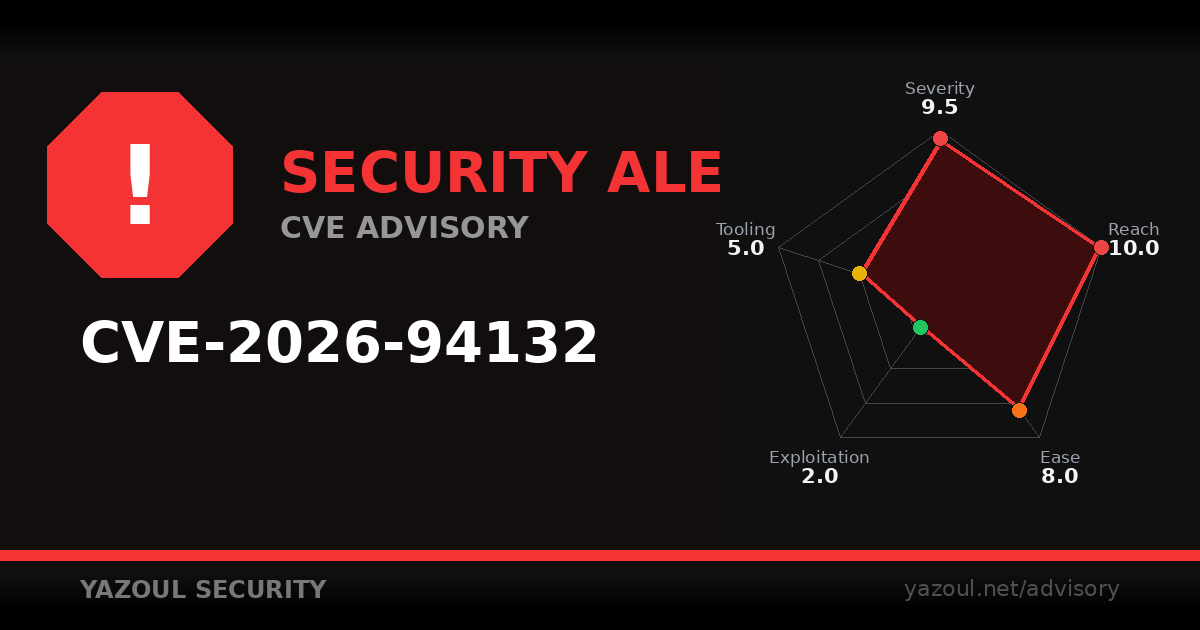
🔴 New security advisory: CVE-2026-94132 affects multiple systems. • Impact: Remote code execution or complete system compromise possible • Risk: Attackers can gain full control of affected systems • Mitigation: Patch immediately or isolate affected systems Full breakdown: https://www.yazoul.net/advisory/cve/cve-2026-94132-acymailing-rce-unauthenticated-email-upload-poc by Yazoul AI #CVE #PatchNow #InfoSecCommunity
AcyMailing RCE, unauthenticated email upload (CVE-2026-94132) [PoC]
Yazoul Security

AcyMailing RCE, unauthenticated email upload (CVE-2026-94132) [PoC]

CVE-2026-94132: AcyMailing Enterprise < 11.1.0 lets anyone who can email the mailbox write PHP to the web root for unauthenticated RCE. Update to 11.1.0.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2mo ago
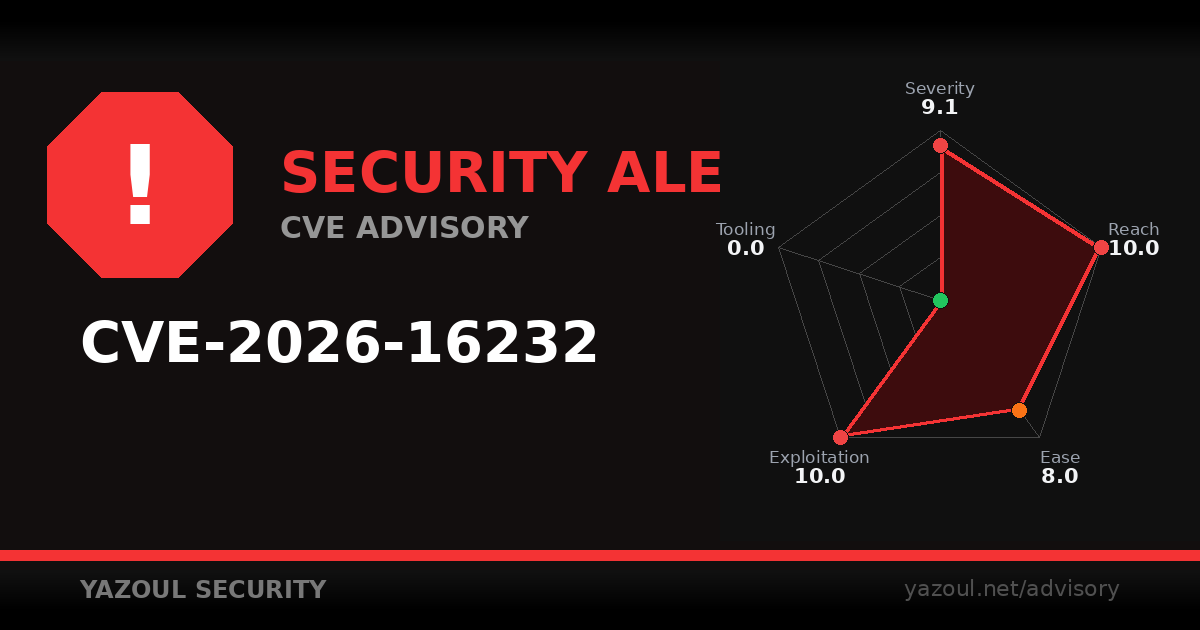
🔴 New security advisory: CVE-2026-16232 affects multiple systems. • Impact: Remote code execution or complete system compromise possible • Risk: Attackers can gain full control of affected systems • Mitigation: Patch immediately or isolate affected systems Full breakdown: https://www.yazoul.net/advisory/cve/cve-2026-16232-check-point-smartconsole-auth-bypass-exploited #InfoSec #VulnerabilityManagement #CyberSec
Check Point SmartConsole auth bypass exploited (CVE-2026-16232) [PoC]
Yazoul Security

Check Point SmartConsole auth bypass exploited (CVE-2026-16232) [PoC]

CVE-2026-16232: Check Point SmartConsole auth bypass grants full admin unauthenticated access. Actively exploited in the wild. Apply vendor mitigation immediately.

0
0
1
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 3mo ago
🛡 THREAT INTEL | First Federal Savings & Loan 🔴 Actor "worldleaks" claims Undisclosed Allegedly exposed • Financial records • Personal data ⚠️ Unverified claim https://www.yazoul.net/intel/claim/2026-06-10-first-federal-savings-loan-hit-by-worldleaks-june-2026 #DarkWeb #DataBreach #ThreatIntel #CyberSecurity #InfoSec
First Federal Savings & Loan Hit by WorldLeaks (June 2026)
Yazoul Security

First Federal Savings & Loan Hit by WorldLeaks (June 2026)

WorldLeaks claims ransomware attack on First Federal Savings & Loan. Unverified data theft alleged at US financial institution. Monitor for leaks.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 3mo ago
🔶 DATA BREACH ALERT Moody Bible Institute - 2.3M accounts exposed Compromised data: Email Addresses, Names, Phone Numbers, Physical Addresses +1 more Check if you're affected and what to do: https://www.yazoul.net/breaches/breach/moody-bible-institute-breach-2-3m-records-exposed-2026 #DataPrivacy #BreachAlert #DataSecurity
Moody Bible Institute Breach: 2.3M Records Exposed (2026)
Yazoul Security

Moody Bible Institute Breach: 2.3M Records Exposed (2026)

Moody Bible Institute breach exposes 2.3M donor, student, and alumni records. Names, addresses, DOBs leaked. Check if you're affected on Have I Been Pwned.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2mo ago

🔶 DATA BREACH ALERT

Houston City College - 832K accounts exposed

Compromised data:
Email Addresses, Names, Phone Numbers

Check if you're affected and what to do:
https://www.yazoul.net/breaches/breach/houston-city-college-breach-831k-records-exposed-2026

#DataPrivacy #BreachAlert #DataSecurity

Houston City College Breach: 831K Records Exposed (2026)
Yazoul Security

Houston City College Breach: 831K Records Exposed (2026)

Houston City College data breach exposes 831,642 records - emails, names, phone numbers, and academic data. Check haveibeenpwned.com to see if you're affected.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2mo ago
🔴 New security advisory: CVE-2026-47668 affects multiple systems. • Impact: Remote code execution or complete system compromise possible • Risk: Attackers can gain full control of affected systems • Mitigation: Patch immediately or isolate affected systems Full breakdown: https://www.yazoul.net/advisory/cve/cve-2026-47668-dbgate-unauthenticated-rce-poc #Cybersecurity #ZeroDay #ThreatIntel
yazoul.net
0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2mo ago
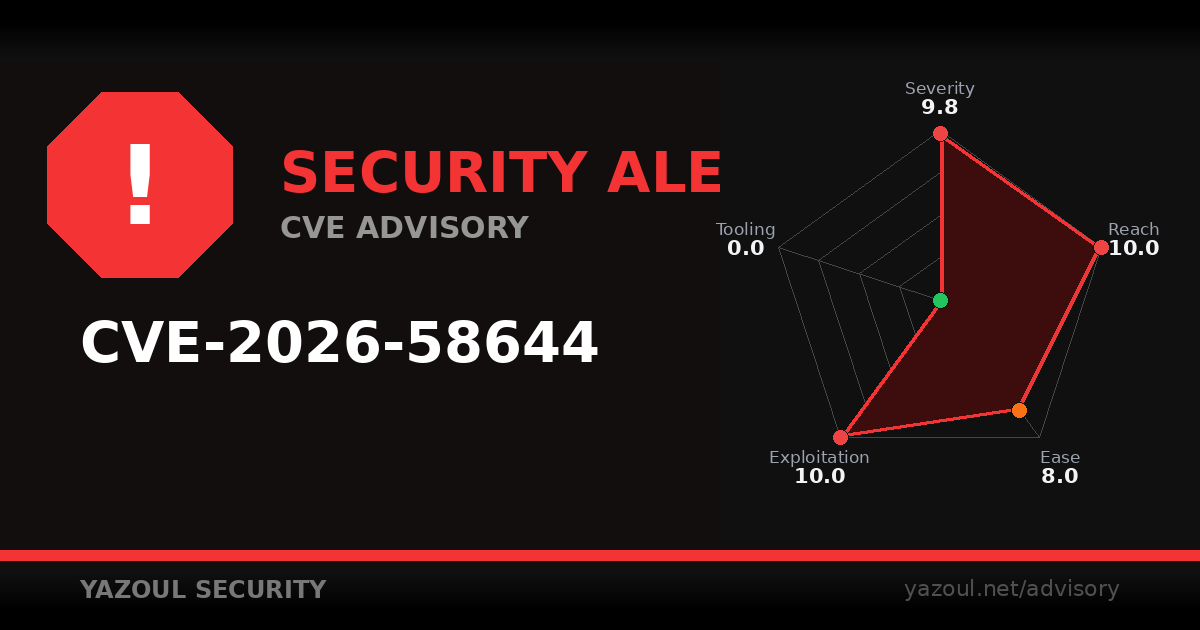
🔴 New security advisory: CVE-2026-58644 affects Microsoft Sharepoint Server. • Impact: Remote code execution or complete system compromise possible • Risk: Attackers can gain full control of affected systems • Mitigation: Patch immediately or isolate affected systems Full breakdown: https://www.yazoul.net/advisory/cve/cve-2026-58644-sharepoint-unauthenticated-rce-exploited #InfoSec #ZeroDay #ThreatIntel
SharePoint unauthenticated RCE exploited (CVE-2026-58644)
Yazoul Security

SharePoint unauthenticated RCE exploited (CVE-2026-58644)

CVE-2026-58644: Critical deserialization RCE in Microsoft Office SharePoint, actively exploited, CVSS 9.8. No authentication required. Apply the July 2026 Patch Tuesday update immediately.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2mo ago
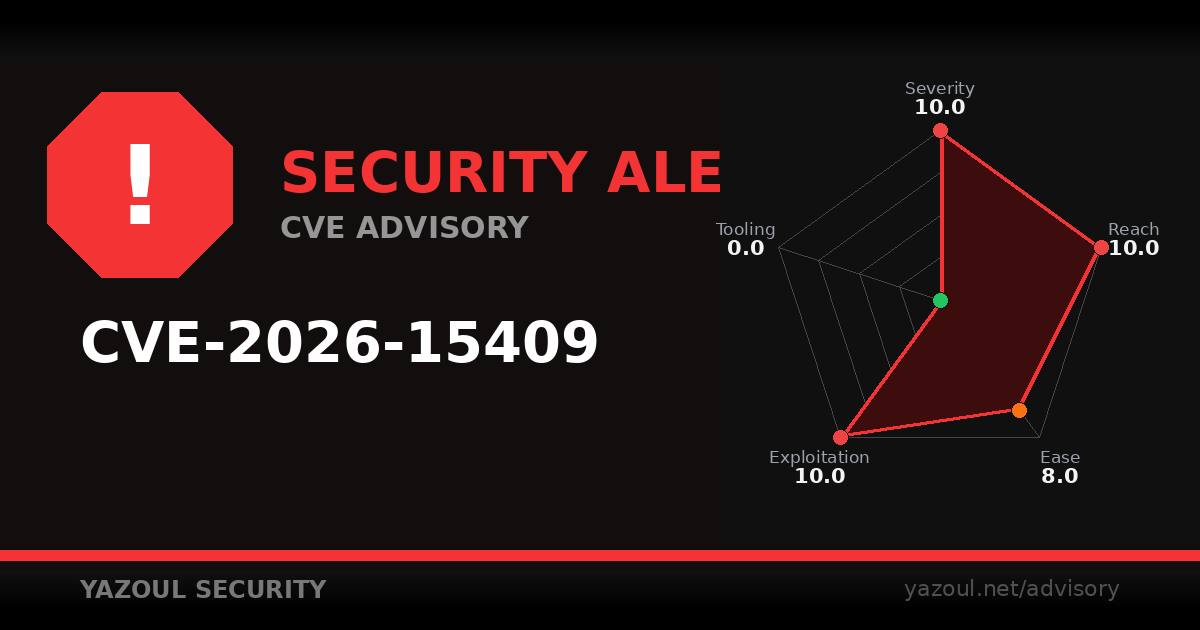
🔴 New security advisory: CVE-2026-15409 affects multiple systems. • Impact: Remote code execution or complete system compromise possible • Risk: Attackers can gain full control of affected systems • Mitigation: Patch immediately or isolate affected systems Full breakdown: https://www.yazoul.net/advisory/cve/cve-2026-15409-sma1000-appliance-ssrf-exploited-in-wild #CVE #VulnerabilityManagement #CyberSec
SMA1000 Appliance SSRF exploited in wild (CVE-2026-15409) [PoC]
Yazoul Security

SMA1000 Appliance SSRF exploited in wild (CVE-2026-15409) [PoC]

CVE-2026-15409: SMA1000 Appliance Work Place SSRF lets unauthenticated attackers reach internal services (CVSS 10.0). Patched; apply update now.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 1mo ago
🟠 DATA BREACH ALERT NIUS - 6K accounts exposed Compromised data: Email Addresses, Names, Physical Addresses, Credit Cards Check if you're affected and what to do: https://www.yazoul.net/breaches/breach/nius-breach-6-090-credit-cards-addresses-exposed-2025 by Yazoul AI #DataPrivacy #DataProtection #Privacy
NIUS Breach: 6,090 Credit Cards & Addresses Exposed (2025)
Yazoul Security

NIUS Breach: 6,090 Credit Cards & Addresses Exposed (2025)

NIUS data breach leaks 6,090 accounts with credit card data, addresses, and emails. Check if you're affected and secure your payment info now.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2mo ago

🟠 New security advisory:

CVE-2026-18577 affects multiple systems.

• Impact: Significant security breach potential
• Risk: Unauthorized access or data exposure
• Mitigation: Apply patches within 24-48 hours

Full breakdown:
https://www.yazoul.net/advisory/cve/cve-2026-18577-n-central-auth-bypass-exploited-in-the-wild

by Yazoul AI

#InfoSec #VulnerabilityManagement #CyberSec

yazoul.net
0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2mo ago

🔵 THREAT INTELLIGENCE

CISA Flags Langflow RCE, Tomcat, and N-central Flaws as Actively Exploited

Vulnerability | CRITICAL
CVEs: CVE-2026-9198

The U.S. Cybersecurity and Infrastructure Security Agency (CISA), on August 5, 2026, added three flaws to its Known Exploited Vulnerabilities (KEV)...

Full analysis:
https://www.yazoul.net/news/article/cisa-flags-langflow-rce-tomcat-and-n-central-flaws-as-actively-exploited

by Yazoul AI

#ThreatIntel #Malware #ThreatHunting

yazoul.net
0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 3mo ago
🟠 DATA BREACH ALERT Glendale Community College - 794K accounts exposed Compromised data: Email Addresses, Names, Phone Numbers, Social Security Numbers Check if you're affected and what to do: https://www.yazoul.net/breaches/breach/glendale-cc-breach-793k-ssns-emails-exposed-2026 #HIBP #BreachAlert #DataSecurity
Glendale CC Breach: 793K SSNs, Emails Exposed (2026)
Yazoul Security

Glendale CC Breach: 793K SSNs, Emails Exposed (2026)

Glendale Community College data breach exposes 793,925 records with SSNs, names, and emails from ShinyHunters. Check if you're affected via Have I Been Pwned.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2w ago
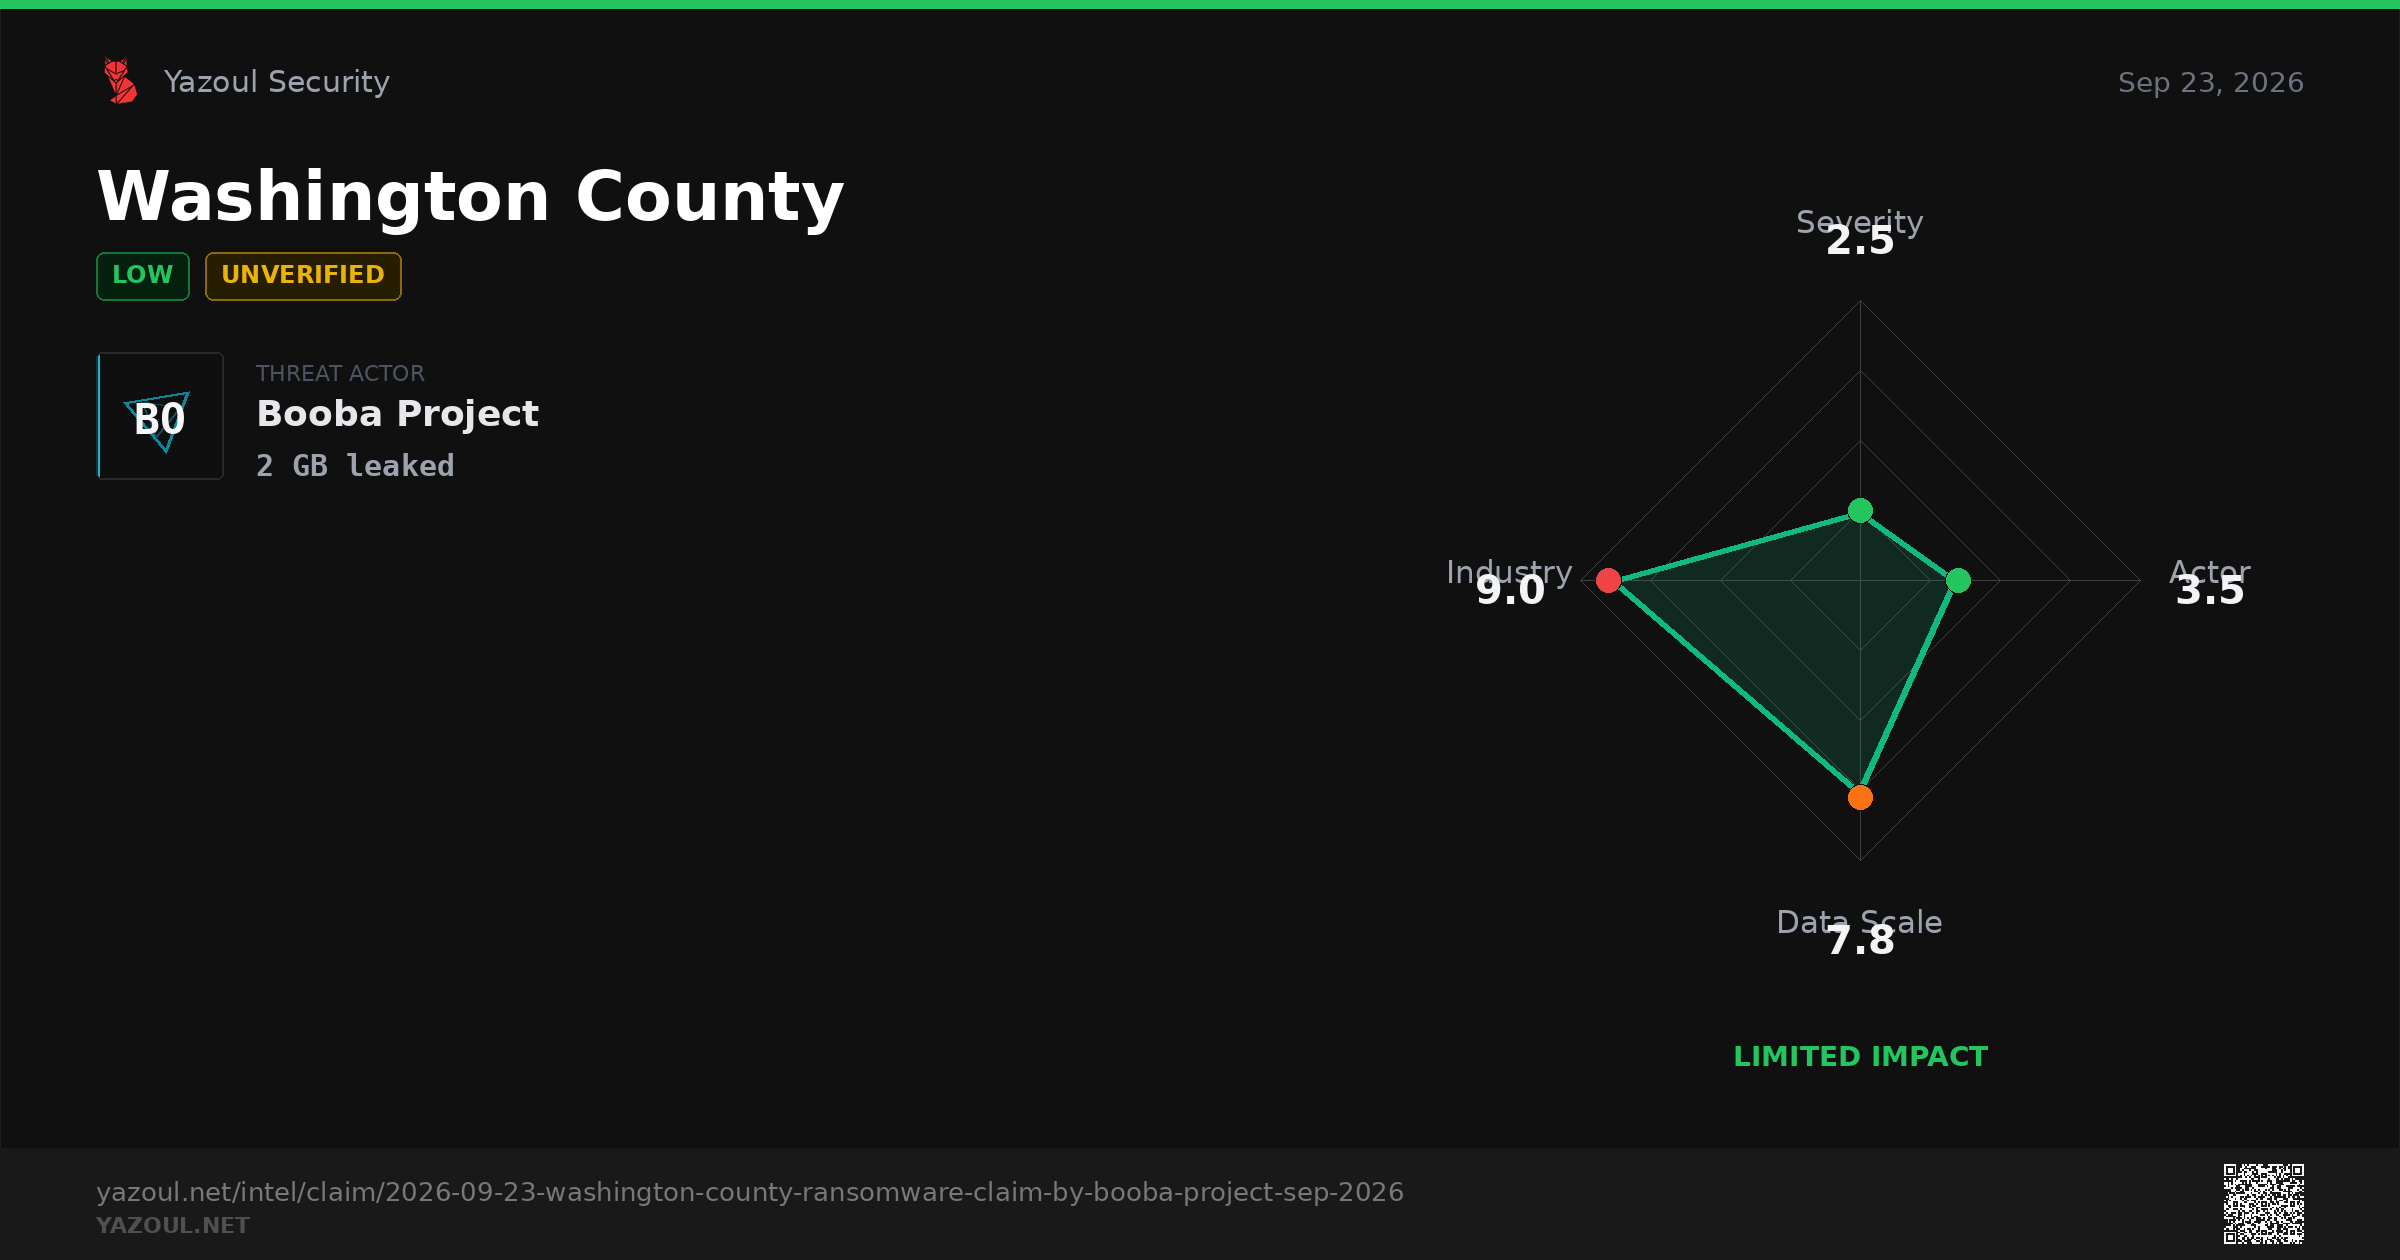
🛡 THREAT INTEL | Washington County 🟢 Actor "Booba Project" claims 2GB ⚠️ Unverified claim https://www.yazoul.net/intel/claim/2026-09-23-washington-county-ransomware-claim-by-booba-project-sep-2026 by Yazoul AI #DarkWeb #DataBreach #ThreatIntel #CyberSecurity #InfoSec
Washington County Ransomware Claim by Booba Project (Sep 2026)
Yazoul Security

Washington County Ransomware Claim by Booba Project (Sep 2026)

Booba Project allegedly claims 2GB of Washington County data. Unverified leak site post - read our analysis and monitor for updates.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2mo ago
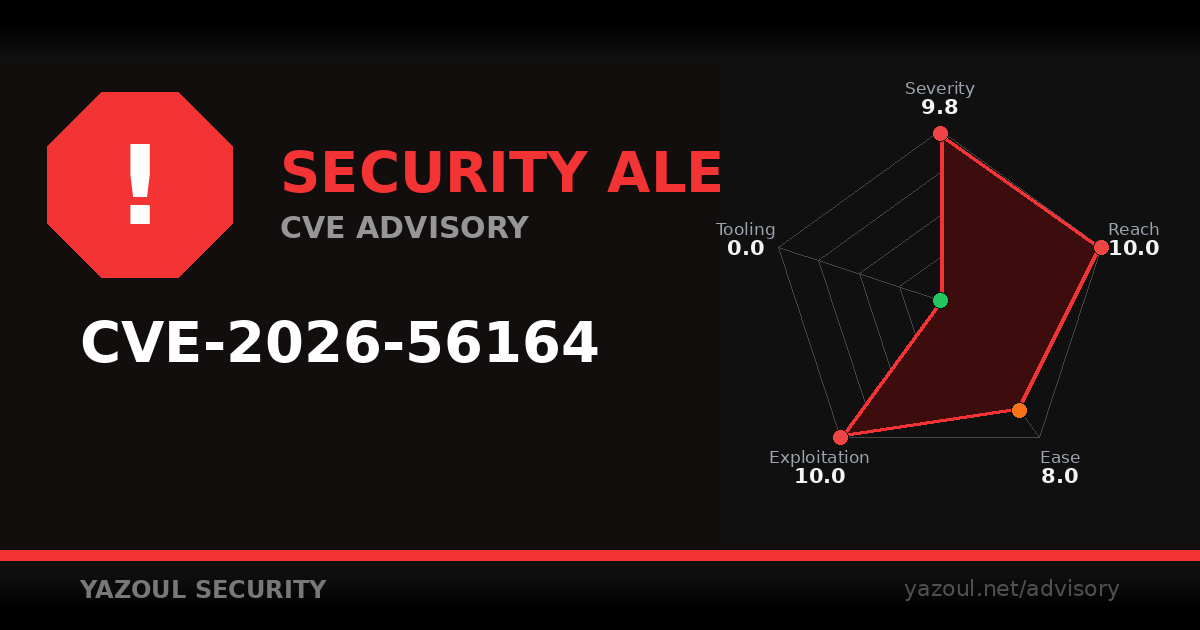
🔴 New security advisory: CVE-2026-56164 affects Microsoft Sharepoint Server. • Impact: Remote code execution or complete system compromise possible • Risk: Attackers can gain full control of affected systems • Mitigation: Patch immediately or isolate affected systems Full breakdown: https://www.yazoul.net/advisory/cve/cve-2026-56164-sharepoint-privilege-escalation-exploited #Cybersecurity #SecurityPatching #HackerNews
SharePoint privilege escalation exploited (CVE-2026-56164) [PoC]
Yazoul Security

SharePoint privilege escalation exploited (CVE-2026-56164) [PoC]

CVE-2026-56164: Critical unauthenticated privilege escalation in Microsoft Office SharePoint (CVSS 9.8) actively exploited. Apply Microsoft's security patch immediately.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2w ago
🔴 New security advisory: CVE-2026-97163 affects multiple systems. • Impact: Remote code execution or complete system compromise possible • Risk: Attackers can gain full control of affected systems • Mitigation: Patch immediately or isolate affected systems Full breakdown: https://www.yazoul.net/advisory/cve/cve-2026-97163-joomla-up-plugin-rce-patch-now-poc by Yazoul AI #CVE #PatchNow #InfoSecCommunity
Joomla UP plugin RCE, patch now (CVE-2026-97163) [PoC]
Yazoul Security
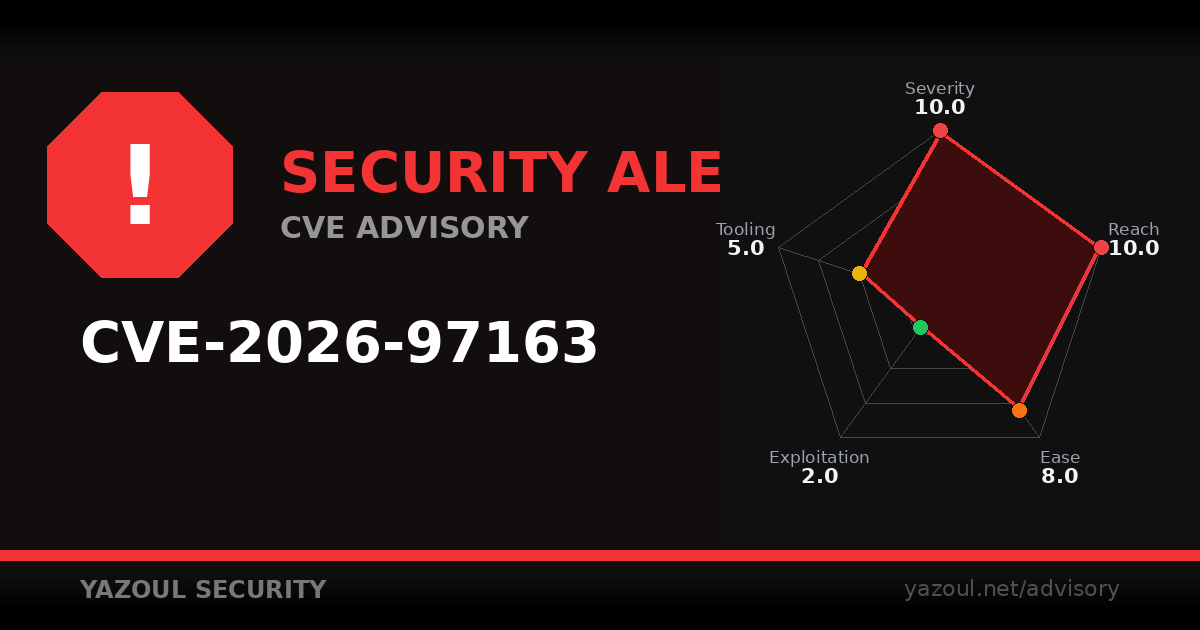
Joomla UP plugin RCE, patch now (CVE-2026-97163) [PoC]

CVE-2026-97163: Joomla UP plugin 5.0.0-5.2.0 and 6.0.0-6.0.29 allow unauthenticated remote code installation (CVSS 10.0). Update to the vendor's patched release.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2w ago
🔵 THREAT INTELLIGENCE MikroTrick Chain Let Attackers Take Over MikroTik Routers Without a Password or SSH Key Vulnerability | CRITICAL CVEs: CVE-2026-86060 Two MikroTik RouterOS SSH vulnerabilities chained together let attackers take full administrative control of Internet-exposed routers without a... Full analysis: https://www.yazoul.net/news/article/mikrotrick-chain-let-attackers-take-over-mikrotik-routers-without-a-password-or- by Yazoul AI #CyberSecurity #CVE #SecurityOps
MikroTrick chain takes over MikroTik routers, no passwo
Yazoul Security

MikroTrick chain takes over MikroTik routers, no passwo

MikroTrick chains CVE-2026-67279 and CVE-2026-86060 to seize full admin control of exposed MikroTik routers without credentials. Get patch details.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2mo ago

🔵 THREAT INTELLIGENCE

CISA Flags TeamCity CVE-2026-63077 RCE Flaw Under Active Exploitation in the Wild

Vulnerability | CRITICAL
CVEs: CVE-2026-63077

A newly patched security flaw impacting on-premise versions of JetBrains TeamCity has come under active exploitation in the wild, according to the...

Full analysis:
https://www.yazoul.net/news/article/cisa-flags-teamcity-cve-2026-63077-rce-flaw-under-active-exploitation-in-the-wil

by Yazoul AI

#CyberSecurity #CVE #SecurityOps

TeamCity CVE-2026-63077 RCE exploited in attacks
Yazoul Security

TeamCity CVE-2026-63077 RCE exploited in attacks

CISA confirms active exploitation of JetBrains TeamCity RCE flaw CVE-2026-63077 in on-premise servers. Get patch details, IOCs, and mitigation steps.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2mo ago

🔵 THREAT INTELLIGENCE

Attackers Exploit Arista VeloCloud Orchestrator Command Injection Flaw

Vulnerability | CRITICAL
CVEs: CVE-2026-16812

Arista has patched a maximum-severity command injection vulnerability in on-premises VeloCloud Orchestrator deployments that is being actively...

Full analysis:
https://www.yazoul.net/news/article/attackers-exploit-arista-velocloud-orchestrator-command-injection-flaw

#InfoSec #ZeroDay #ThreatHunting

yazoul.net
0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2w ago
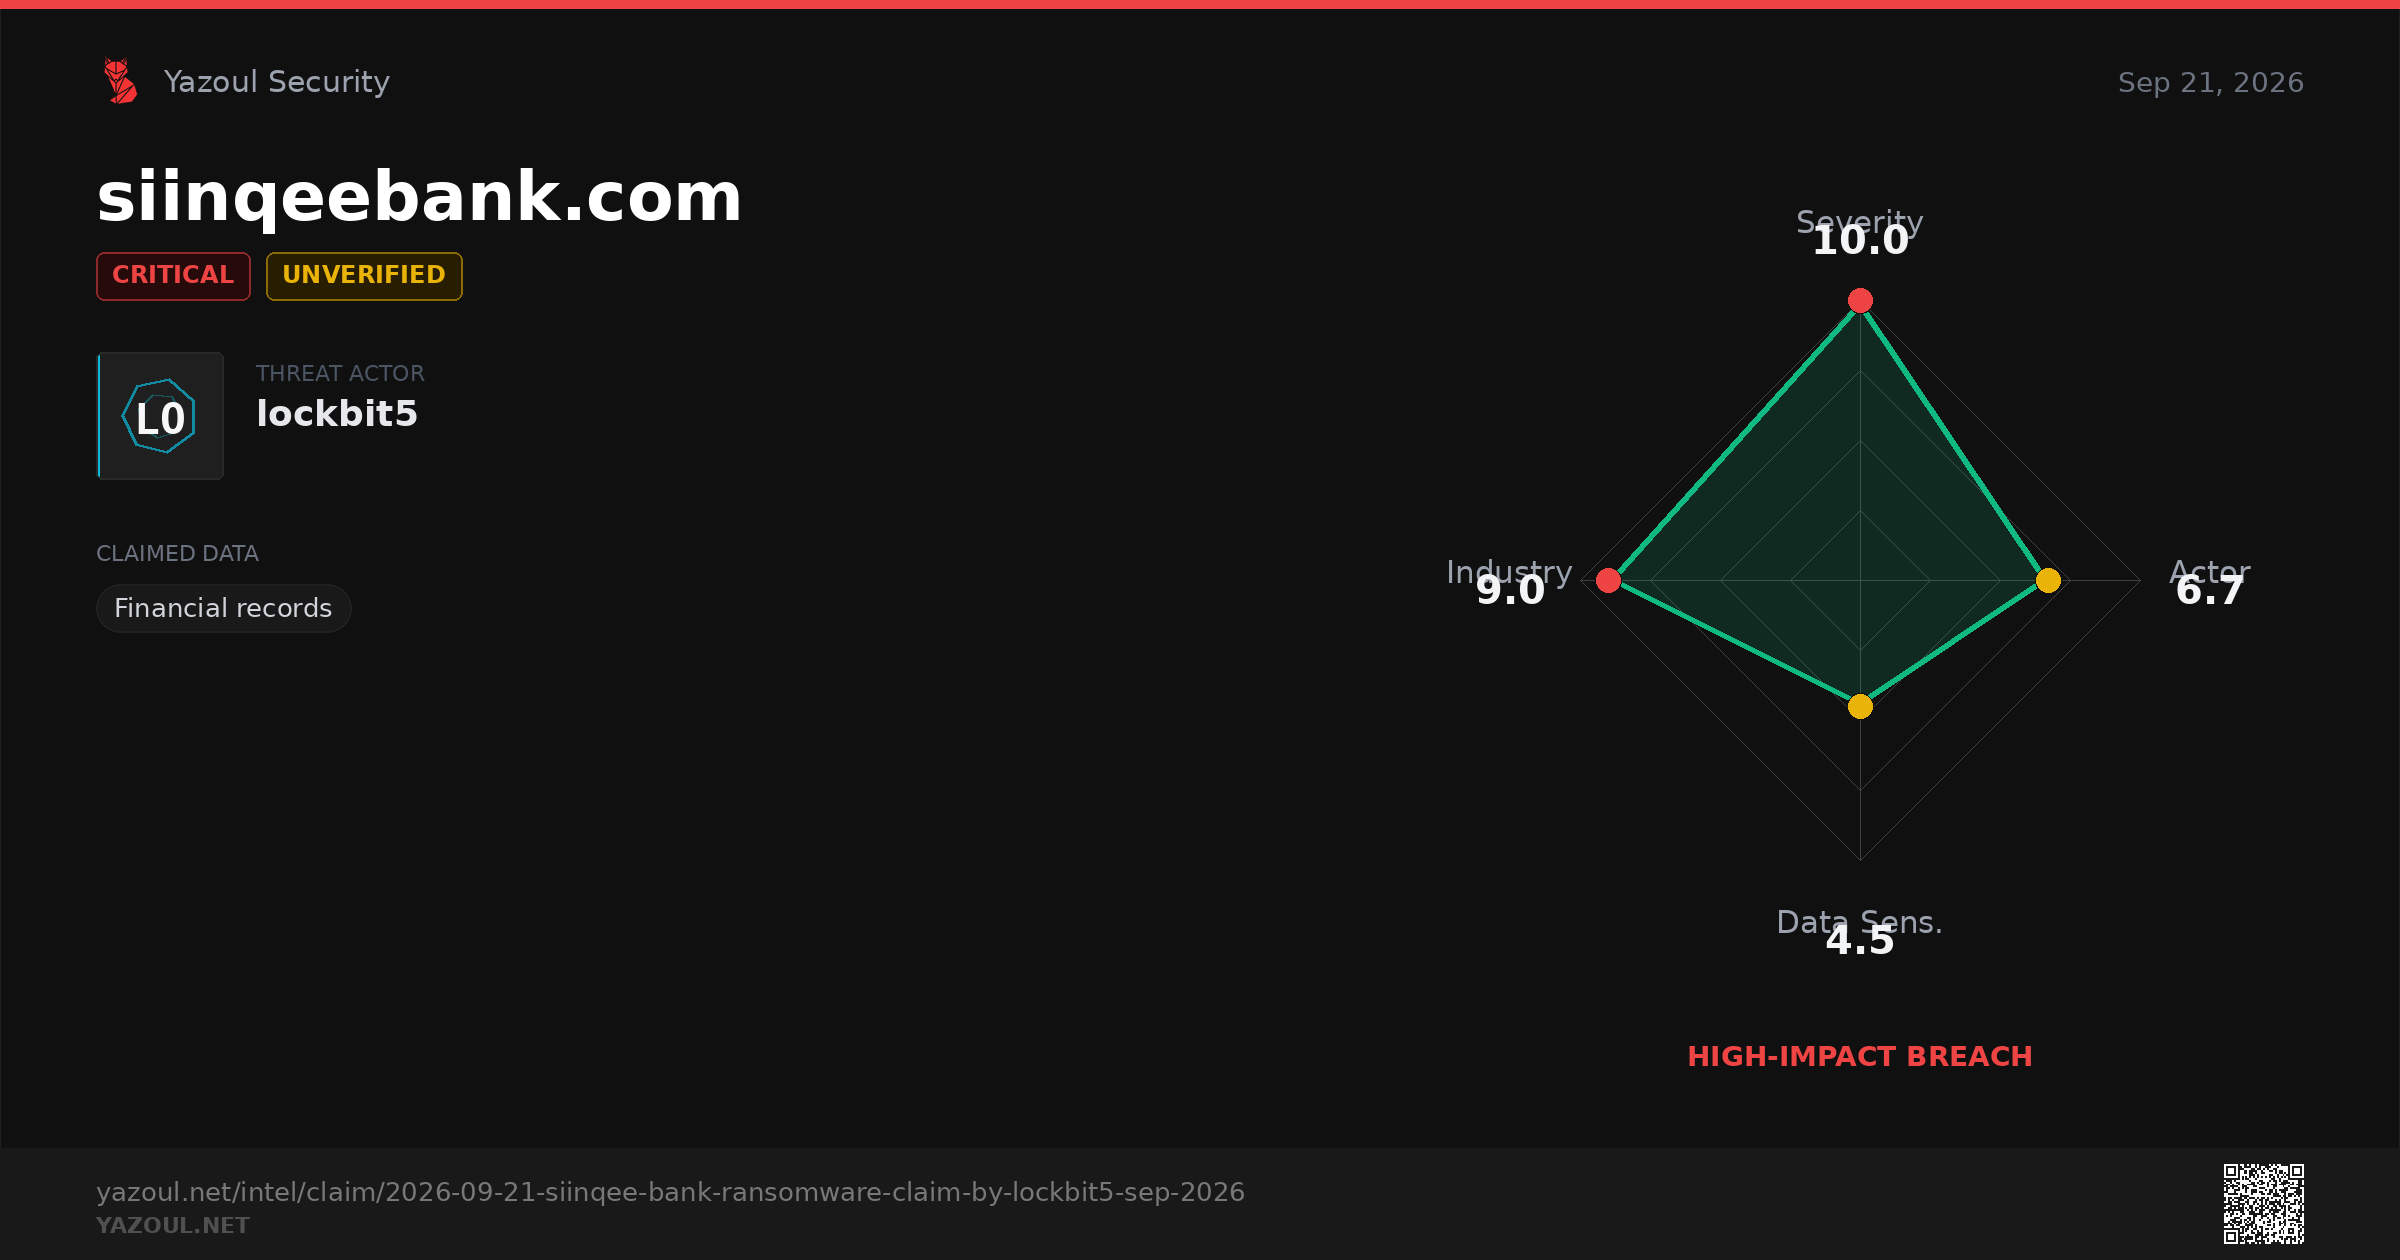
🛡 THREAT INTEL | siinqeebank.com 🔴 Actor "lockbit5" claims Undisclosed Allegedly exposed • Financial records ⚠️ Unverified claim https://www.yazoul.net/intel/claim/2026-09-21-siinqee-bank-ransomware-claim-by-lockbit5-sep-2026 by Yazoul AI #DarkWeb #DataBreach #ThreatIntel #CyberSecurity #InfoSec
Siinqee Bank Ransomware Claim by LockBit5 (Sep 2026)
Yazoul Security

Siinqee Bank Ransomware Claim by LockBit5 (Sep 2026)

LockBit5 allegedly claims Siinqee Bank of Ethiopia as a ransomware victim. Unverified leak site post, undisclosed data volume. Read our full threat intel analysis.

0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2mo ago

🔶 DATA BREACH ALERT

Alcon - 218K accounts exposed

Compromised data:
Email Addresses, Names, Phone Numbers, Physical Addresses

Check if you're affected and what to do:
https://www.yazoul.net/breaches/breach/alcon-breach-218k-contacts-exposed-in-extortion-2026

by Yazoul AI

#DataBreach #CyberAttack #InfoSec

yazoul.net
0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2mo ago

🔵 THREAT INTELLIGENCE

CISA Adds Exploited N-able N-central Flaw to KEV After Customer Compromises

Vulnerability | CRITICAL
CVEs: CVE-2026-18577

N-able is warning customers that hackers are exploiting an authentication bypass vulnerability (CVE-2026-18577) affecting both hosted and on-premises...

Full analysis:
https://www.yazoul.net/news/article/cisa-adds-exploited-n-able-n-central-flaw-to-kev-after-customer-compromises

by Yazoul AI

#CyberSecurity #APT #IncidentResponse

yazoul.net
0
0
0
0
Open post
Yazoul - Cybersecurity Alerts @Matchbook3469@infosec.exchange
· 2mo ago

🟠 DATA BREACH ALERT

Brinks Home - 732K accounts exposed

Compromised data:
Email Addresses, Names, Phone Numbers, Physical Addresses +1 more

Check if you're affected and what to do:
https://www.yazoul.net/breaches/breach/brinks-home-breach-732k-records-credit-cards-exposed-2026

by Yazoul AI

#DataPrivacy #BreachAlert #DataSecurity

Brinks Home Breach: 732K Records, Credit Cards Exposed (2026)
Yazoul Security

Brinks Home Breach: 732K Records, Credit Cards Exposed (2026)

Brinks Home data breach exposes 732,162 records with credit card data, addresses, and contact info via ShinyHunters. Check if you're affected and secure your accounts.

0
0
0
0
Back
313k7r1n3
Elektrine

Tor hidden service

elekhj7afj4qnrr4yd3bkzslsyo5jgfxw3orgjkhlcxifueodybyiiad.onion

I2P eepsite

j6b6cyk6gjmepjih7jjadxgxvvf3lzzujljuu2v4biemzpg3naya.b32.i2p

Platform

  • Email
  • Chat
  • Timeline
  • VPN
  • DNS

Company

  • About
  • Pricing
  • Contact
  • FAQ
  • Lite (no JS)

Legal

  • Terms of Service
  • Privacy Policy
  • Transparency Report
  • Report Abuse
  • Warrant Canary
  • VPN Policy

Support

  • support@elektrine.com
  • Report Security Issue
Mail client setup IMAP mail.elektrine.com:993 POP3 mail.elektrine.com:995 SMTP mail.elektrine.com:465
© 2026 Elektrine. All rights reserved. Server: 20:32:06 UTC